Who should own blockchain infrastructure inside a large organization
By Jeremy Ryan, Founder & CEO · September 2026
Blockchain infrastructure should usually be owned as a shared enterprise platform, operated by platform engineering or IT, secured by security teams, governed through formal change control, and funded by accountable business owners. That is the short answer to who should own blockchain infrastructure inside a large organization.
A single department should not attempt to own every part of the system. Node operations, validator permissions, cryptographic keys, smart contract upgrades, compliance evidence, data rights, and business outcomes create different forms of accountability. Treating them as one ownership question is how organizations end up with an expensive pilot that nobody can safely operate after launch.
The organization that pays for a blockchain program is not necessarily the organization that should run it. Sustainable ownership separates business accountability from technical control without separating either from governance.
Key Takeaways
I recommend a federated ownership model for most large organizations. The CIO or CTO organization should provide the technical operating home. A business product owner should remain accountable for the workflow, adoption, funding, and measurable commercial or operational result. Security, compliance, legal, and procurement need explicit control responsibilities rather than advisory roles that activate only after a problem occurs.
The practical division is straightforward:
• Platform engineering or enterprise IT operates nodes, environments, observability, backups, capacity, patching, and production support.
• Security owns identity standards, key management controls, privileged access review, incident response integration, and security assurance.
• Business product ownership owns the use case, budget, success metrics, user adoption, and decisions about whether the network should continue to scale.
• Legal and compliance own the interpretation of contractual, records, privacy, and regulatory obligations that shape what can be written to the ledger and retained off chain.
• A governance body approves material protocol, validator, smart contract, and data access changes.
This arrangement may feel more complex than assigning ownership to one executive. It is more honest. Blockchain infrastructure combines a distributed technical system with a shared decision system. Those are different jobs.
Choose The Right Operating Home
Start With The Default: Platform Engineering Owns Production Operations
For a production deployment, I would normally place blockchain infrastructure within platform engineering, enterprise IT, or a closely related cloud operations function. This does not mean IT “owns the business.” It means the team already accountable for production reliability should operate the production components.
A permissioned blockchain is not merely an application database with unusual terminology. It may include validator nodes, peer connectivity, certificate authorities, key custody arrangements, smart contract deployment pipelines, ledger monitoring, log collection, backup processes, and incident runbooks. These are operational systems. They need on call coverage, controlled access, and documented recovery procedures.
Permissioned enterprise networks generally use known validators, which makes operator identity and accountability central rather than optional. Kaleido’s enterprise blockchain production guide makes this point directly: known validators require explicit operational accountability. If a validator is unavailable, compromised, or improperly permissioned, the issue is not theoretical governance. It is a production incident.
Consider a manufacturer using a permissioned ledger to track regulated parts across procurement, assembly, and service partners. The supply chain group may understand the workflow best, but it should not be expected to manage certificate rotation at 2:00 a.m., investigate node resource exhaustion, or validate a cloud failover. Those tasks belong in a technical operating model with clear service commitments.
Use A Center Of Excellence When Reuse Is The Real Goal
A blockchain center of excellence, or CoE, becomes useful when the organization expects repeated adoption across business units. Its role is not to become a permanent bottleneck or a shadow IT department. Its purpose is to create reusable architecture patterns, vendor standards, governance templates, security guardrails, and shared expertise.
A separate blockchain platform team is more defensible when several conditions exist at once:
• Multiple business units need the same node, identity, wallet, or smart contract capabilities.
• The organization supports more than one network or protocol family.
• Operations cross jurisdictions, legal entities, or regulated business lines.
• Shared controls are needed for validators, permissions, key custody, and audit evidence.
• The cost of rebuilding the same integration and governance process repeatedly is becoming visible.
There is no universal staffing threshold that proves when a dedicated team is required. The available evidence supports a context dependent decision, not a single org chart. Still, a useful test is this: if every new blockchain project must independently solve identity, validator operations, smart contract review, and vendor due diligence, central platform capability is probably overdue.
Keep The Business Product Owner Accountable For Value
Business ownership is essential, but business ownership alone is inadequate. A business product owner should be accountable for whether the blockchain-enabled workflow produces a measurable result: fewer reconciliation disputes, faster settlement, better provenance evidence, improved partner coordination, or another defined outcome.
The business owner should also decide whether the ledger is still justified when conditions change. For example, a retail loyalty team may sponsor a tokenized rewards program. If partner participation stays low, the product owner must be able to stop investment rather than allowing technical inertia to preserve a system without business value.
Blockchain4Europe argues that projects should define both intellectual property ownership and success metrics early. Its governance report on IP ownership and success measures supports a critical distinction: technical ownership and commercial accountability should be connected, but they should not be conflated.
Avoid The Two Ownership Extremes
Both common extremes create predictable failures.
| Ownership Extreme | What It Gets Right | What Commonly Breaks | Better Correction |
|---|---|---|---|
| Business team owns everything | Strong domain context and urgency | Weak operational resilience, inconsistent security controls, fragile handoff after launch | Retain business accountability while platform engineering runs production services |
| Central IT owns everything | Standardized operations, identity, and change controls | Slow decisions, poor workflow fit, unclear value ownership | Give a named product owner decision rights over outcomes and roadmap priorities |
| Separate blockchain CoE owns everything | Concentrated expertise and reusable patterns | Becomes a gatekeeper detached from operations or business value | Use the CoE for standards and enablement, not permanent unilateral control |
The goal is not compromise for its own sake. The goal is to assign decisions to the people who have the right incentives and capabilities to make them.
Separate Governance From Daily Operations
Treat “Ownership” As A Set Of Decision Rights
Blockchain systems often separate economic ownership from control over protocol changes. Fordham Law Review’s analysis of crypto governance and upgrade control highlights the broader principle: the parties with value at stake may not be the parties able to adopt an update. Large organizations should design around that reality rather than assuming funding authority automatically creates change authority.
I recommend documenting at least five ownership categories:
-
Infrastructure operations: Who runs nodes, monitors services, patches hosts, manages backups, and responds to outages?
-
Protocol governance: Who can approve validator changes, consensus parameter changes, network membership rules, and platform upgrades?
-
Application governance: Who can deploy or upgrade smart contracts, APIs, and integrations?
-
Security control: Who owns keys, certificates, privileged access, identity lifecycle, threat response, and security exceptions?
-
Business and data accountability: Who decides the legitimate purpose of processing, success metrics, data classification, retention requirements, and partner obligations?
A blockchain may be decentralized in how consensus is reached, yet highly centralized in how an enterprise manages access. That is especially true for private blockchain deployments. The University of Arkansas Blockchain Center of Excellence notes that private blockchain programs must explicitly settle data ownership, control, software ownership, and liability questions; its white paper on private blockchain ownership and liability frames these issues as governance decisions, not just technical details.
Use A RACI That Reflects The System You Actually Run
A RACI matrix is useful only when it names concrete decisions. “Technology owns blockchain” is too vague to govern an incident or an upgrade window.
| Decision Or Control | Responsible | Accountable | Consulted | Informed |
|---|---|---|---|---|
| Node uptime, monitoring, and patching | Platform engineering | Platform engineering leader | Security, application team | Product owner, governance body |
| Validator admission and removal | Network operations | Governance body | Security, legal, consortium members | Product owners |
| Key custody and privileged access | Security operations | CISO or delegated security leader | Platform engineering, legal | Governance body |
| Smart contract release | Application engineering | Business product owner | Security, platform engineering, legal | Support teams, affected partners |
| Protocol or network upgrade | Platform engineering | Governance body | Security, legal, business owners | All participants |
| Audit evidence and records retention | Compliance operations | Compliance leader | Security, platform engineering, legal | Internal audit |
| Vendor renewal and exit readiness | Vendor management | Executive sponsor | Platform engineering, security, legal | Governance body |
This model clarifies a subtle but important distinction: a team can be responsible for executing a task without being accountable for the resulting business or risk decision. For example, platform engineering may execute a validator upgrade, but a governance body should approve it when the change affects other business units or external consortium members.
Managed Infrastructure Does Not Outsource Accountability
Managed blockchain infrastructure can be sensible when internal teams lack specialized capability, need faster deployment, or want to avoid running nodes around the clock. But a managed service changes the control plane; it does not eliminate it.
BitGo’s comparison of blockchain infrastructure build versus buy describes the core tradeoff: in house operation provides greater control but can add deployment time and compliance exposure, while outsourcing can shift operational and maintenance burdens. The key word is shift. The enterprise still owns vendor oversight, access decisions, evidence requirements, contractual obligations, incident escalation, and exit planning.
Before selecting a managed provider, assign an internal control owner for each of these areas:
• Service level agreements and operational level agreements
• Node administrative access and break glass procedures
• Security event notification and joint incident response
• Ledger data export, backup access, and recovery testing
• Key ownership, certificate lifecycle, and identity revocation
• Migration rights, termination support, and provider concentration risk
Fair warning: a provider may operate the node while your organization remains accountable for a regulatory record, a contractual commitment, or an access decision made through that node. A service contract is not a governance model.
Design Day Two Before Day One Ends
Many ownership problems appear after a successful pilot. During a pilot, a small delivery group can make decisions quickly. In production, every change becomes more consequential because real users, partners, data, and controls are involved.
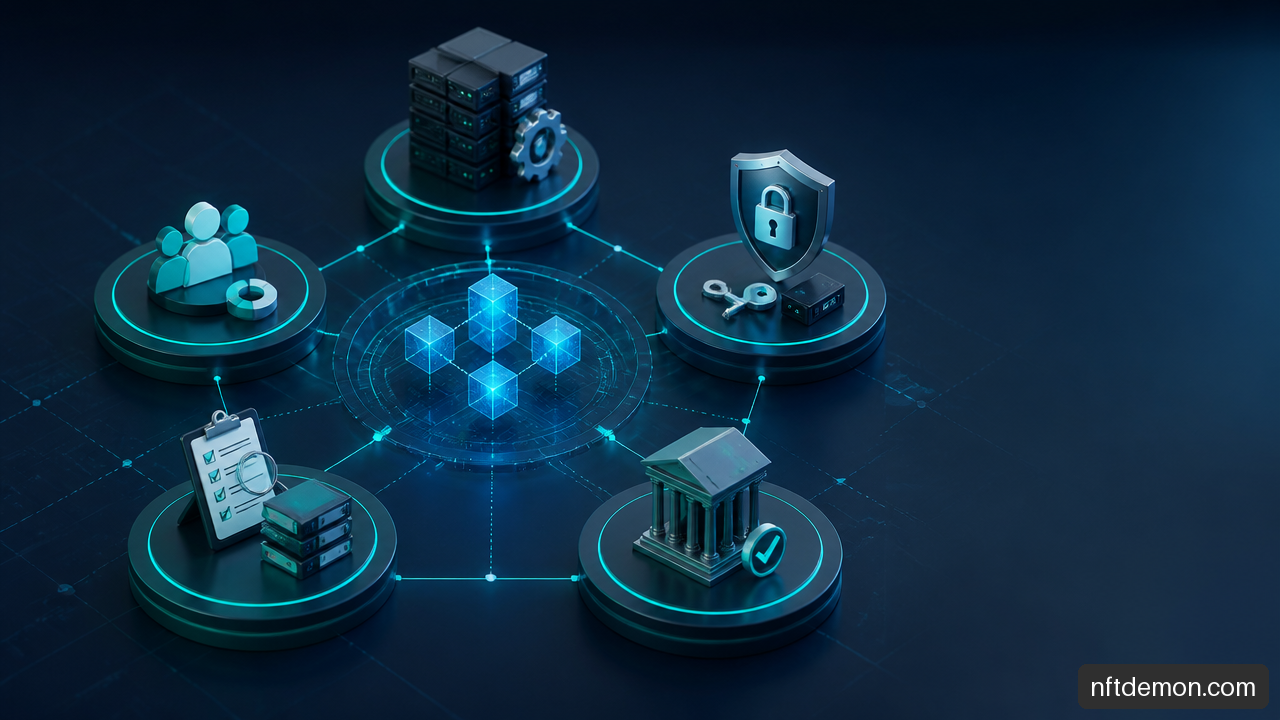
The minimum day two model should include:
-
A named on call owner for node and integration incidents.
-
A severity model that distinguishes availability failures from incorrect ledger state, unauthorized access, and key compromise.
-
A change calendar for validator, protocol, smart contract, and cloud infrastructure updates.
-
A documented emergency authority for disabling access, pausing a smart contract where architecture permits it, or removing a compromised participant.
-
Regular access reviews, recovery exercises, audit evidence collection, and vendor performance reviews.
For a consortium network, this becomes even more important. A single company should not quietly control rules that affect other participants. Private blockchain models may fit a single organization where internal governance dominates, while consortium designs fit shared control among known parties. In practice, consortium governance should define voting rights, quorum, cost allocation, dispute resolution, new member admission, validator obligations, and an exit process before production use expands.
Frequently Asked Questions
Who Should Own Blockchain Infrastructure Inside A Large Organization?
I recommend platform engineering or enterprise IT as the operational owner, with a named business product owner accountable for value and a cross functional governance body accountable for material rule changes. Security, legal, and compliance should own their respective controls rather than serving as passive reviewers.
Should Blockchain Live In IT, Security, Product, Or A Center Of Excellence?
It should live across those functions with distinct decision rights. IT or platform engineering should run the service. Security should own cryptographic and access controls. Product should own outcomes. A CoE should set reusable standards when multiple teams or networks need common capabilities. Avoid placing permanent end to end ownership in any one of these groups.
Who Should Own Node Operation And Validator Management?
Platform engineering should normally operate nodes. Validator admission, removal, and major configuration changes should be approved through governance because those decisions affect trust, availability, and participant rights. Security should control the credentials and privileged identities used to administer validators.
Who Is Responsible For Smart Contract Upgrades?
Application engineering should be responsible for building and testing upgrades. The business product owner should be accountable for whether the change serves the intended workflow. Security, legal, and platform teams should be consulted before release. Material upgrades should pass through a formal change process, especially if contracts govern shared assets, regulated records, or external counterparties.
What Is The Difference Between Owning The Blockchain And Owning The Data On It?
Operating a node or funding the network does not automatically grant ownership of every record. Data ownership depends on the deployment design, contracts, access rules, and applicable obligations. Store only what must be immutable or independently verifiable on chain. Keep sensitive or changeable information off chain where appropriate, with controlled references or proofs on the ledger.
Should Blockchain Infrastructure Be Built In House Or Bought As A Service?
Choose in house operation when control requirements, integration depth, specialized security policies, or strategic differentiation justify the operational burden. Choose managed infrastructure when speed, limited internal capacity, or operational efficiency matter more, provided internal teams retain control over vendor risk, access, evidence, incident escalation, and exit planning.
What Breaks When Ownership Is Not Defined After Launch?
Routine work becomes disputed work. A certificate expires and no team owns renewal. A smart contract needs an urgent fix but nobody has authority to approve deployment. An auditor requests evidence, but logs sit with a vendor and retention requirements were never assigned. These are not blockchain specific technical failures. They are operating model failures expressed through blockchain infrastructure.
Sources
• University of Arkansas — Blockchain Center of Excellence White Paper Series: https://walton.uark.edu/departments/information-systems/files/bccoewhitepaper022019open.pdf
• Blockchain4Europe — Governance of and with blockchains report: https://www.blockchain4europe.eu/wp-content/uploads/2021/05/report_governance_v1.0_0.pdf
• Fordham Law Review — (UN)CORPORATE CRYPTO-GOVERNANCE: https://fordhamlawreview.org/wp-content/uploads/2020/04/Reyes_April_A_13.pdf
• Kaleido — Enterprise Blockchain: Architecture & Production Guide: https://www.kaleido.io/blockchain-blog/enterprise-blockchain
• BitGo — Blockchain Infrastructure as a Service: Build vs. Buy: https://www.bitgo.com/resources/blog/blockchain-infrastructure-as-a-service/
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.