Privacy preserving zkps in institutional CBDCs
By Jeremy Ryan, Founder & CEO · October 2026
Privacy-preserving zero-knowledge proof mechanisms in institutional CBDCs can protect commercially sensitive settlement information without making the system unaccountable. The practical objective is not absolute anonymity. It is controlled confidentiality: institutions prove that a payment satisfies ledger, liquidity, eligibility, and compliance rules while revealing only the data each authorized party needs.
- How Zero-Knowledge Proofs Change Institutional CBDC Privacy
- Designing Selective Disclosure For Settlement
- Engineering, Governance, And Deployment Decisions
- Key Takeaways
- Frequently Asked Questions
- Sources
How Zero-Knowledge Proofs Change Institutional CBDC Privacy
The Institutional Problem Is Commercial Confidentiality, Not Cash-Like Secrecy
A wholesale or institutional CBDC operates among regulated entities: banks, custodians, central counterparties, payment operators, and potentially central-bank accounts. Those participants need accountability. They also have legitimate reasons not to expose every funding position, counterparty relationship, settlement amount, or business purpose to every other network participant.
That distinction matters. Retail CBDC discussions often begin with anonymity. Institutional designs should begin with attributable authority and minimized disclosure. The initiating institution may need to be known to the central bank or validating network, while the amount, receiving institution, underlying client reference, or settlement rationale remains confidential outside a narrowly defined access group.
A zero-knowledge proof, or ZKP, establishes that a statement is true without exposing the private inputs used to establish it. In an institutional CBDC, the statement might be: “This participant controls an unspent settlement note, the note is valid, the transaction conserves value, the sender is authorized, and the transfer satisfies the applicable policy rules.” The verifier receives the proof and public commitments, not necessarily the amount, balance, or business payload.
The useful design question is therefore not, Can the payment be hidden? It is, Which facts must each role verify, and what data does that verification actually require?
The Bank for International Settlements’ Project Tourbillon research on payer anonymity tested payer anonymity while not extending the same anonymity to payees. That asymmetry is especially relevant to institutional systems. Equal privacy for every party is not always necessary, or even desirable, when regulated institutions have different legal duties and operational roles.
What Happens Under The Hood
A private institutional payment generally separates state validation from transaction disclosure. The ledger stores commitments, nullifiers, encrypted records, or other cryptographic representations rather than plain-text settlement details. A ZKP demonstrates that the state transition is legitimate.
A simplified flow looks like this:
- The sending institution identifies one or more valid unspent CBDC notes or account commitments.
- It constructs a private transaction that identifies the inputs, outputs, amount constraints, authorization conditions, and policy conditions.
- It generates a proof that the inputs exist, have not been spent, and create valid outputs without inflating supply.
- The network verifies the proof, records a nullifier or equivalent spent-state marker, and finalizes the transaction under the permissioned ledger’s consensus rules.
- The receiving institution decrypts or otherwise derives the payment information intended for it.
The nullifier is central to double-spend prevention. It is a cryptographic marker derived from a private note or input. The ledger can reject a repeated nullifier without learning the note’s confidential contents. In a permissioned network, participant admission and consensus add further controls, but they do not remove the need for cryptographic replay protection.
ZKPs are not a replacement for encryption, digital signatures, identity controls, or permissions. They are one layer in a broader architecture. Encryption protects data delivered to a recipient. Signatures prove authorization. A permissioned ledger constrains who may submit or validate. ZKPs prove that confidential data satisfies a rule.
| Mechanism | What It Protects | What It Can Prove Or Enable | Institutional Limitation |
|---|---|---|---|
| Encryption | Content visible only to key holders | Confidential delivery and storage | Does not by itself prove policy compliance |
| Pseudonymization | Direct identity labels | Reduced casual identifiability | Transaction graph analysis can often reconnect identities |
| Zero-knowledge proofs | Private transaction inputs and attributes | Validity, thresholds, eligibility, and rule satisfaction | May still expose metadata and requires specialized engineering |
| Secure multiparty computation | Inputs held by multiple parties | Joint computations without pooling raw data | Can be operationally heavier for real-time settlement |
The World Economic Forum’s CBDC privacy and confidentiality analysis notes that ZKPs can verify transaction legitimacy or computational results without exposing private inputs. For institutional payment systems, that is the essential capability: prove compliance with the settlement rulebook without making the rulebook an excuse for routine overcollection of transaction data.
Privacy Is Not Metadata Privacy
A proof may hide the amount and payment reference while still leaving visible signals: transaction time, submitting node, validator observations, message size, frequency, and relationships implied by repeated interactions. A system that claims confidentiality but publishes identifiable institution-to-institution timing patterns can leak meaningful market intelligence.
Consider a securities settlement window. Even if trade values are hidden, a series of payments from one institution immediately after a public market event may reveal funding stress or trading activity. This does not mean ZKPs fail. It means privacy requirements must include network and operational metadata, not just ledger fields.
Possible mitigations include controlled batching, relay infrastructure, standardized transaction formats, delayed publication of certain records, and role-based access to operational telemetry. Each introduces trade-offs. Batching may reduce timing leakage but can conflict with real-time gross settlement expectations. Decision-makers should define the acceptable delay before selecting a mitigation.
Designing Selective Disclosure For Settlement
Start With A Disclosure Matrix
A privacy architecture should be documented as a disclosure matrix before proof circuits are designed. Without one, teams often build technically elegant confidentiality that cannot be operated by compliance, legal, or recovery functions.
The matrix below is a practical starting point. It is a policy model, not a universal requirement. Jurisdiction, payment type, legal authority, and market-infrastructure rules can change the appropriate allocation.
| Field Or Capability | Sending Institution | Receiving Institution | Central Bank Operator | Routine Supervisor | Exceptional Authorized Access |
|---|---|---|---|---|---|
| Sender identity | Yes | Usually yes | Yes, or resolvable | As required by mandate | Yes with documented authority |
| Receiver identity | Usually yes | Yes | Potentially encrypted or resolvable | Not necessarily routine | Yes with documented authority |
| Transaction amount | Yes | Yes | Proof-validatable; plain view depends on policy | Threshold or aggregate view may suffice | Available only through governed disclosure |
| Payment purpose | Yes | Yes | Usually encrypted | Limited attestation or coded category | Available through governed disclosure |
| KYC and sanctions status | Attestation | Attestation where relevant | Verifiable proof | Verifiable proof | Underlying record through lawful process |
| Liquidity and balance sufficiency | Proof only | Not normally needed | Proof only, unless liquidity operations require more | Aggregate or rule-based visibility | Case-dependent |
This model avoids a common mistake: assuming the central bank must either see all underlying data or see none. In practice, a central bank may only need to verify that settlement is valid, supply is conserved, participants are eligible, and prescribed controls have been met. A supervisor may need access to an auditable attestation and the ability to trigger a governed disclosure process, not continuous visibility into every business payment.
Compliance Proofs Should Be Narrow And Testable
ZKPs can support attribute-level attestations. A bank may prove that it completed KYC, that a sanctions-screening requirement was met, or that a transaction falls within a policy threshold, without revealing the entire underlying customer file. Deutsche Bank’s institutional-finance discussion is not included as a linkable source here, but the principle is well established in privacy-preserving finance: compliance checks can be represented as verifiable claims rather than broad data transfers.
That does not mean a proof can honestly certify a vague concept such as “this payment is not suspicious.” Suspicion is contextual. It depends on changing typologies, external intelligence, linked activity, and human judgment. ZKPs work best where the policy is deterministic and can be encoded precisely.
Good candidates include:
• Participant is an approved member of the settlement network.
• Required screening was completed using an approved ruleset version.
• Transfer amount is below a specified threshold.
• Transfer is within a preapproved liquidity limit.
• Asset, currency, and settlement window are eligible.
Poor candidates include broad assertions about intent, future behavior, or risk that has not been formally modeled.
The BIS Innovation Hub’s Tourbillon report on privacy, security, scalability, and policy controls examined whether payer anonymity could coexist with security and controls against illicit transactions. The institutional implication is clear: privacy engineering must be paired with explicit control objectives. A proof is only as meaningful as the policy statement encoded in its circuit and the reliability of the data feeding that statement.
A Concrete Interbank Settlement Pattern
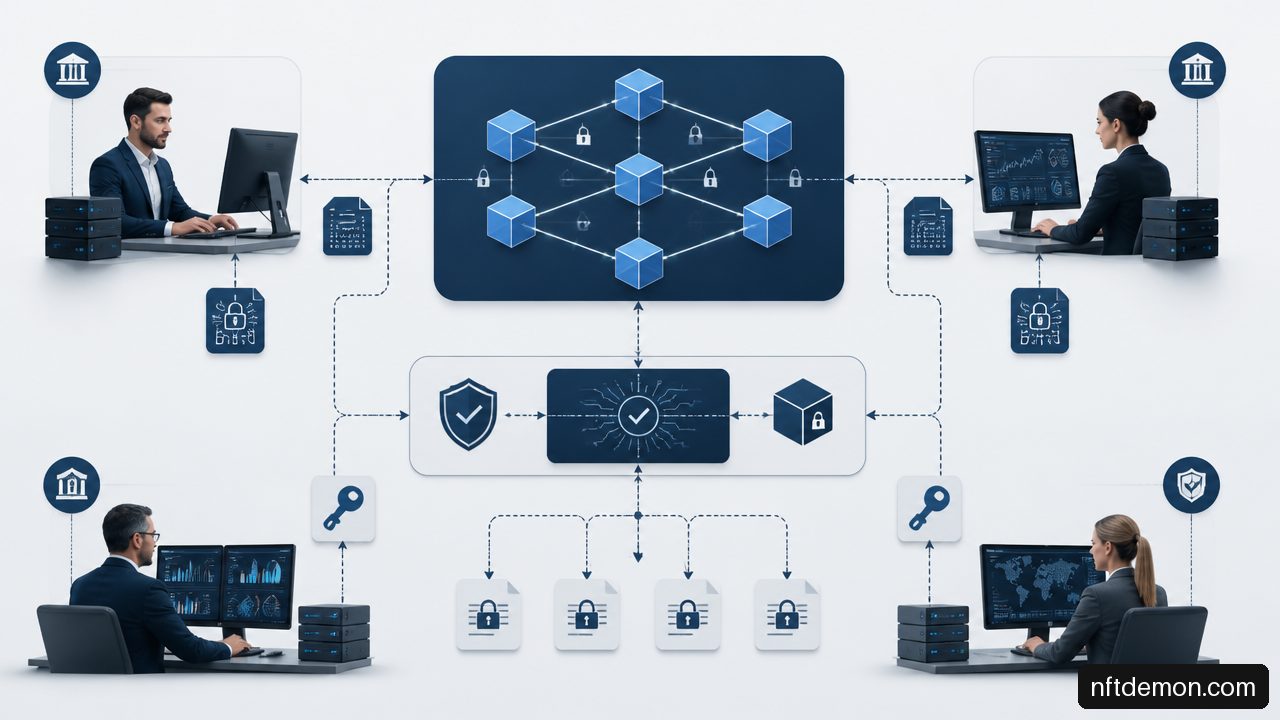
One academic proposal, Relaxed Sender Anonymity for CBDC Interbank Settlement: A Zero-Knowledge Approach, illustrates a more institutionally realistic pattern than fully anonymous payment rails. It identifies the initiating institution while hiding receiving-party information, amount, and business-payload data through ZKPs and encryption.
Its implementation concept combines Groth16 proofs, Poseidon-hashed commitments, an incremental Merkle tree, ECIES encryption, and an on-chain note registry. The exact stack should not be treated as a production recommendation. It is a useful architectural example because it separates several functions that are too often collapsed into one vague promise of “private blockchain payments.”
• Commitments bind values without revealing them.
• Merkle trees prove that a note or commitment is included in an authorized set.
• Nullifiers indicate that a private input has been consumed.
• ZKPs show that the transfer obeys validity constraints.
• Encryption delivers readable payment details to intended recipients.
This model is especially suitable when an institution must remain accountable for initiation, but commercial counterparties and payment details should not be broadly visible. It is less suitable where every participant requires complete real-time visibility for risk management or where the legal framework requires transaction-level centralized disclosure.
For deployment planning, blockchain platform selection for financial institutions should be evaluated alongside privacy requirements. The ledger’s finality model, identity system, smart-contract environment, operational tooling, and integration path all shape whether private proof verification is feasible.
Engineering, Governance, And Deployment Decisions
Proof-System Choices Have Operational Consequences
Proof systems differ in proof size, verifier cost, proving time, cryptographic assumptions, and setup requirements. Groth16 is attractive because proofs are compact and verification can be efficient. Its trade-off is a circuit-specific trusted setup. If setup materials are compromised and the process is not properly managed, soundness risk can arise.
Transparent systems may avoid a traditional trusted setup, but their proofs can be larger or impose different performance costs. There is no published consensus establishing which proof system is best for production institutional CBDCs. The correct choice depends on transaction volume, hardware assumptions, privacy scope, governance tolerance for ceremonies, and upgrade capability.
Decision-makers should require measured evidence rather than generic performance claims. At minimum, a pilot should report:
- Proof-generation latency under realistic institutional signing and encryption workflows.
- Verification throughput at target validator counts and settlement peaks.
- Ledger storage growth from commitments, nullifiers, encrypted payloads, and audit artifacts.
- Finality time from proof submission through irreversible settlement.
- Failure behavior when proofs are malformed, keys are unavailable, or a participant node is offline.
A proof system can verify quickly while still being impractical if proof creation takes too long on the institution’s approved hardware. Conversely, low-latency proofs do not solve a poorly designed recovery process. This is why enterprise blockchain architecture security and scalability should be considered as one integrated system problem rather than a cryptography procurement exercise.
Key Recovery Is A Core Privacy Requirement
Private CBDC architectures rely on keys for signing, decryption, viewing, and sometimes nullifier generation. An institution can lose access through employee turnover, hardware security module failure, mergers, resolution proceedings, or compromised credentials. If there is no recovery path, funds or critical records may become inaccessible. If recovery is too broad, privacy collapses.
A defensible model separates keys and authorities:
| Key Or Authority | Primary Function | Recovery Principle |
|---|---|---|
| Transaction signing key | Authorizes payment submission | Institutional custody, rotation, and revocation controls |
| Recipient viewing key | Reads incoming encrypted payment details | Recoverable through controlled institutional escrow or successor process |
| Compliance viewing authority | Supports legally authorized disclosure | Threshold approval, logging, and narrowly scoped access |
| Proof proving key or prover environment | Generates validity proofs | Secured operational environment with reproducible deployment controls |
A threshold process is often more credible than a single master decryption key. For example, recovery of a defunct institution’s encrypted payment data might require an appointed administrator, central-bank authority, and an independent oversight function to approve a limited disclosure event. Every action should create an immutable audit trail stating who approved it, what was disclosed, under which legal basis, and when access expires.
Fair warning: this governance layer cannot be postponed until after a pilot. A system that proves transactions privately but cannot handle legal succession or operational recovery is incomplete.
Build From Settlement Rules, Not From Cryptography Demos
A disciplined implementation sequence starts with business rules and works down to proof circuits.
- Map settlement states. Define issuance, transfer, redemption, reversal limits, finality, and exception handling.
- Define visibility by role. Use a disclosure matrix for institutions, operators, supervisors, and exceptional-access authorities.
- Translate deterministic rules into proofs. Keep proof statements narrow, versioned, testable, and linked to approved policy rulesets.
- Pilot adversarial scenarios. Test double-spend attempts, replay, malformed proofs, colluding participants, lost keys, and emergency disclosure requests.
- Measure the whole workflow. Include integration with sanctions tooling, treasury systems, identity services, and core payment operations.
- Plan cryptographic agility. Proof systems, curves, hashes, and encryption schemes may need replacement over the CBDC’s life.
The final point deserves attention. A CBDC may operate for decades. Cryptographic components should be versioned and upgradeable without creating ambiguous settlement history or forcing a disruptive migration of all outstanding private notes. Institutions examining proof technology in adjacent applications may also benefit from comparing optimistic vs zk rollup deployment, particularly the different assumptions around proof verification and operational complexity.
Key Takeaways
• Institutional CBDC privacy should prioritize controlled confidentiality with accountable participants, not universal anonymity.
• ZKPs can prove settlement validity, authorization, eligibility, thresholds, and balance constraints without exposing the underlying private values.
• A disclosure matrix is more valuable than a broad privacy promise because it defines exactly who can see sender, receiver, amount, purpose, and compliance information.
• ZKPs do not automatically protect timing, network origin, message size, or transaction-graph metadata.
• Compliance proofs are strongest for deterministic rules such as eligibility, screening completion, and limits; they are weak substitutes for contextual financial-crime analysis.
• Key recovery, institutional succession, and emergency disclosure must be designed as auditable governance processes, not treated as exceptional afterthoughts.
• Production suitability should be established through measured proof latency, verification throughput, finality, storage, recovery, and failure-mode testing.
Frequently Asked Questions
What Is A Privacy-Preserving Zero-Knowledge Proof In An Institutional CBDC?
It is a cryptographic mechanism that lets a regulated participant prove a CBDC transaction satisfies defined rules without revealing all transaction inputs. For example, a bank can prove it has a valid unspent balance commitment and is within its authorized limits without publishing its underlying liquidity position to every validator.
Can A Bank Prove An Interbank CBDC Payment Is Valid Without Revealing The Amount?
Yes, if the proof circuit encodes value conservation, authorization, input ownership, and range constraints. The network verifies that inputs equal outputs plus any permitted fees while the actual amount remains committed or encrypted. The receiving bank still needs a way to read the amount, typically through recipient-directed encryption.
Which Fields Can A ZKP Hide In A Wholesale CBDC?
Potentially the amount, balance, receiving party, business reference, asset attributes, and compliance evidence. The right choice depends on the disclosure matrix. Institutional sender identity is often retained or resolvable because the network needs accountability for initiation and membership.
Can A Central Bank Support AML Controls Without Reading Every Payment?
Potentially, yes. It can verify cryptographic attestations that required controls were completed and require disclosure only under defined authority. However, ZKPs cannot fully replace investigations that depend on external data, behavioral patterns, or evolving risk intelligence. The system should preserve lawful escalation paths.
How Do ZKPs Prevent Double Spending In A Permissioned CBDC?
A transaction proves ownership of a valid unspent note or committed balance and publishes a unique spent-state marker, often called a nullifier. Once the ledger accepts that marker, a repeated use is rejected. Permissioned consensus helps establish a single ordered record, while the cryptographic marker prevents private inputs from being reused.
What Happens If An Institution Loses A Private CBDC Access Key?
The outcome depends on the recovery design. A mature system should distinguish signing keys from viewing or decryption keys and support controlled recovery through institutional custody, threshold approvals, successor processes, and auditable authority. Without that design, private data or funds may become inaccessible.
Are ZKPs Fast Enough For High-Volume Institutional Settlement?
There is not yet sufficient public evidence to make a universal production-scale claim for institutional CBDCs. Verification may be efficient for certain proof systems, but proving time, hardware, integration overhead, storage, and peak-load behavior must be tested against the actual settlement model. A proof benchmark alone is not a payment-system benchmark.
Sources
Bank for International Settlements — Project Tourbillon:
https://www.bis.org/project/tourbillonBank for International Settlements — Exploring privacy, security and scalability for CBDCs:
https://www.bis.org/publications/project-tourbillon-exploring-privacy-security-and-scalability-cbdcs.pdfWorld Economic Forum — Privacy and Confidentiality Options for Central Bank Digital Currencies:
https://www3.weforum.org/docs/WEF_Privacy_and_Confidentiality_Options_for_CBDCs_2021.pdfAcademic proposal — Relaxed Sender Anonymity for CBDC Interbank Settlement: A Zero-Knowledge Approach:
https://arxiv.org/html/2608.28529v1
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.