Permissioned security token smart contract architecture
By Jeremy Ryan, Founder & CEO · October 2026
Smart contract architectural patterns for permissioned security token issuance determine whether a tokenized offering can survive real compliance, operational, and governance demands. The token contract is only one part of the system. A credible design also defines how investor eligibility is proven, how rules change, who can intervene, and what happens when a claim, service, or administrative key fails.
- Separate Trust Boundaries, Not Just Functions
- Transfer Validation Patterns That Hold Up Under Pressure
- Lifecycle, Governance, And Upgrade Architecture
- Choosing The Right Pattern For The Offering
- FAQ: Permissioned Security Token Architecture
- Sources
Separate Trust Boundaries, Not Just Functions
A permissioned security token is a token whose issuance, ownership, and transfer are constrained by predefined legal, investor, and operational rules. Those rules might include investor qualification, jurisdiction, sanctions screening outcomes, lockups, holding limits, or transfer agent approval. The architectural question is not whether to enforce restrictions. It is where each restriction belongs and who is allowed to change it.
I recommend treating the design as a set of explicit trust boundaries rather than placing every rule in one oversized token contract. A monolithic contract can be simpler to deploy, but it combines unrelated risks: an identity administrator, a policy administrator, and an emergency operator may all gain more authority than they should have.
The Core Layered Model
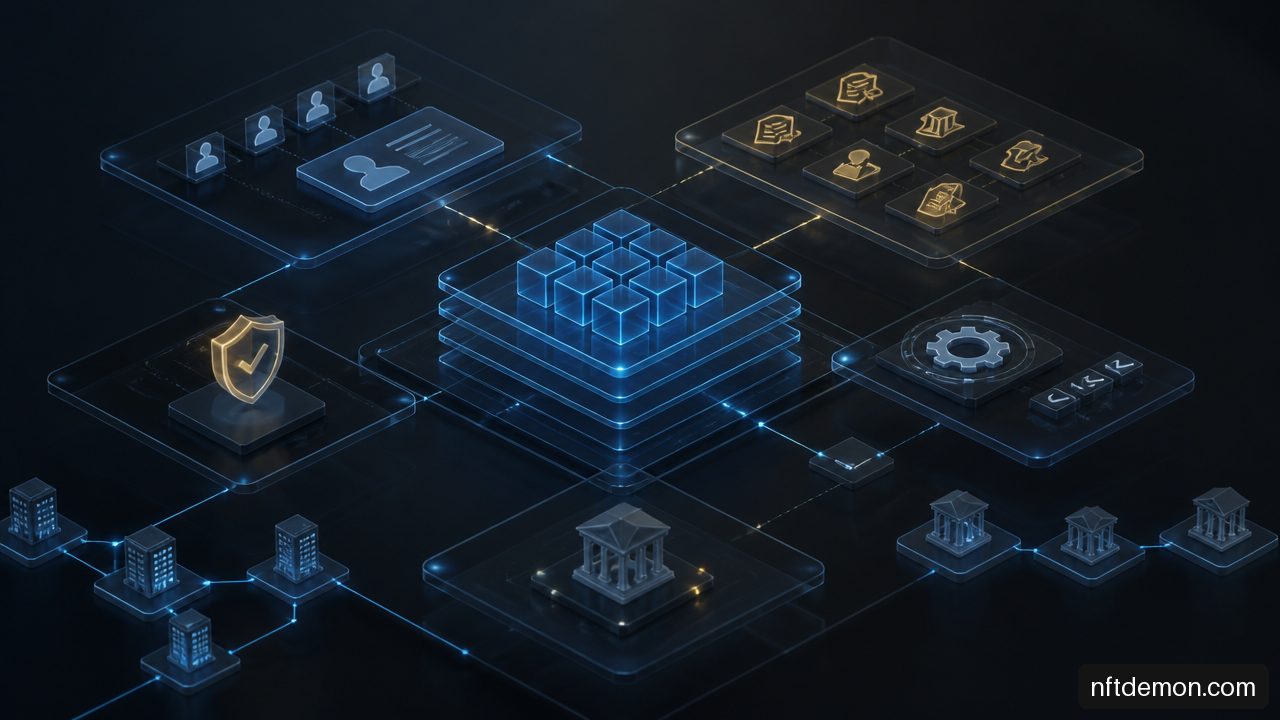
A durable permissioned architecture commonly separates at least five components:
| Layer | Primary Responsibility | State It Should Own | Main Risk If Combined Improperly |
|---|---|---|---|
| Token contract | Balances, supply, transfer execution | Holdings, total supply, partition balances | Compliance logic becomes difficult to audit and upgrade safely |
| Identity registry | Maps wallet addresses to approved identity records | Wallet to identity association | Personal or eligibility data becomes entangled with balances |
| Claims layer | Establishes investor attributes | Claim references, issuer attestations, expiry status | Any single identity vendor becomes a universal gatekeeper |
| Compliance engine | Evaluates transaction rules | Policy parameters, counters, transfer restrictions | Token administrator can silently rewrite eligibility rules |
| Governance layer | Controls privileged actions | Roles, multisig thresholds, delays | One compromised key controls the entire offering |
The ERC 3643 and T REX model illustrates this separation. Its validator architecture can combine a token contract, identity registry, identity storage, trusted claim issuer registry, trusted claim topics registry, and compliance contract. In that structure, the T REX white paper describes validation that checks receiver claims and compliance rules before a transfer is allowed.
That separation has a practical benefit: a trusted issuer can attest that an investor passed a required review without the token contract storing the underlying personal information. The token only needs a reliable answer to a narrow question: Does this wallet currently satisfy the required eligibility conditions?
Identity Should Not Live Inside The Token Contract
Putting KYC, accreditation, or jurisdiction fields directly into the token contract is tempting because the transfer logic can read its own storage. It is usually the wrong abstraction for an institutional offering.
Investor identity is not the same as a wallet. One investor may use multiple approved wallets, change custodians, lose access to a wallet, or transfer legal ownership through a managed process. A separate identity registry lets the system associate several wallets with an identity record while keeping token balances distinct from identity administration.
Claims should be minimal. Rather than recording a full jurisdiction or detailed KYC result, a claim can express only the attribute the policy needs, such as:
• Eligible for Regulation D transfer rules
• Eligible for a specified jurisdictional exemption
• Accredited status valid until a defined date
• Not subject to a particular restriction at the time of validation
This does not eliminate privacy concerns. On chain activity can still reveal that an address passed some type of eligibility gate, particularly when claim topics and transfer patterns are observable. For sensitive offerings, I would minimize public metadata, keep personally identifiable information off chain, and make claim topics no broader than the actual policy requires.
The deployment model also begins with the network choice. The decision affects validator visibility, participant onboarding, consensus controls, and integration boundaries. This guide to choosing between public and permissioned blockchains is useful when the issuer must decide whether restricted token logic should operate on a public network, a private network, or a hybrid arrangement.
Standards Are Building Blocks, Not Complete Architectures
ERC 3643 and ERC 1400 address different architectural priorities. Neither eliminates the need for a defined operating model.
| Design Option | Best Fit | Strength | Limitation |
|---|---|---|---|
| Simple whitelist token | Narrow offering with stable rules and limited holders | Low implementation complexity | Weak claim semantics and limited operational flexibility |
| ERC 3643 style architecture | Identity driven offerings with reusable eligibility claims | Clear separation of identity, issuers, claims, and compliance | More contracts, dependencies, and governance decisions |
| ERC 1400 style architecture | Offerings needing partitions, documents, and controller operations | Strong vocabulary for regulated asset operations | Identity architecture must be selected or built separately |
| Custom modular architecture | Unusual legal structure or existing enterprise integrations | Can match the issuer’s workflow precisely | Higher design, assurance, and maintenance burden |
ERC 1400 is best understood as an umbrella framework. ERC 1594 addresses core issuance and transfer validation, ERC 1410 addresses partitions, ERC 1643 supports document references, and ERC 1644 covers controller operations. A security token may borrow these ideas without implementing every interface.
A standard can make interoperability easier. It cannot decide who should approve a forced transfer, whether an expired claim blocks redemption, or how a migration preserves legal ownership records.
Transfer Validation Patterns That Hold Up Under Pressure
The transfer path is where legal policy becomes executable behavior. A basic permissioned transfer may look straightforward: check the sender, check the recipient, then move balances. In production, the difficult cases are stale claims, policy changes, partial fills, lockups, corporate actions, and external approval requirements.
Synchronous On Chain Validation
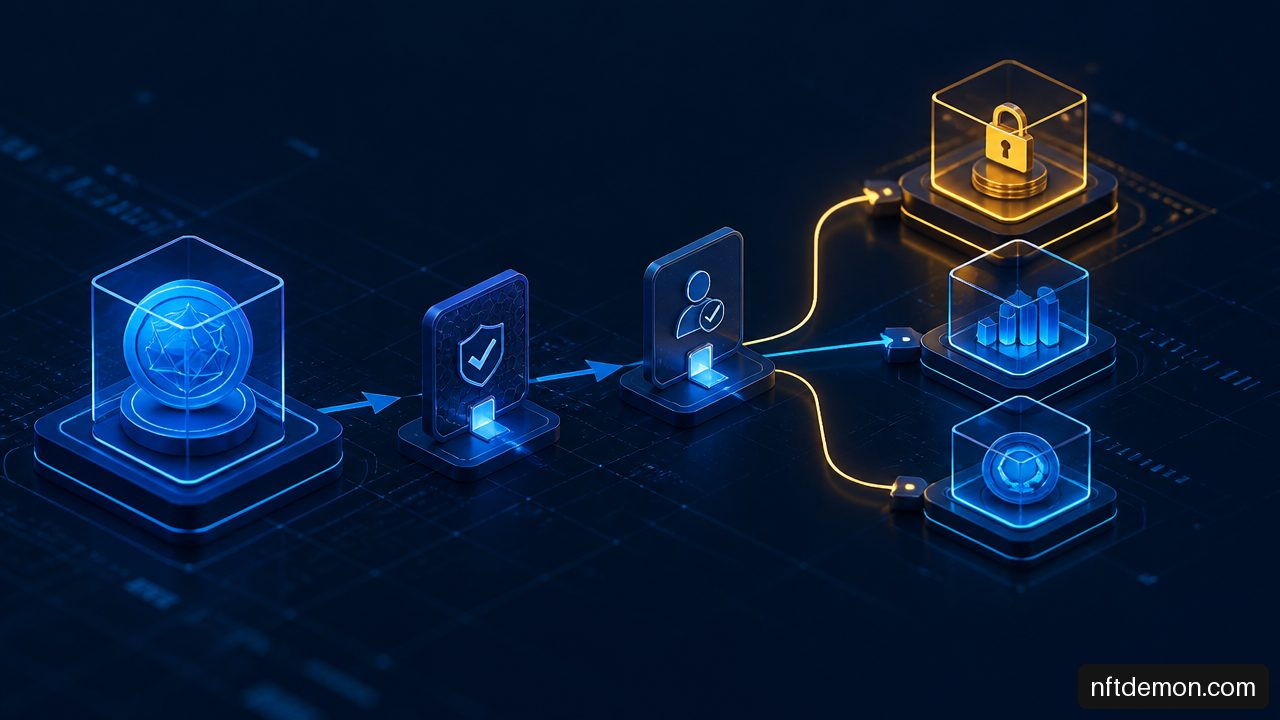
The most direct pattern validates every proposed transfer during contract execution. The token calls a validator or compliance contract, which checks identity eligibility and transaction rules before changing balances.
A typical validation sequence is:
- Confirm that the token is not globally paused and that the transfer method is permitted.
- Resolve the sender and recipient wallets to approved identity records.
- Verify required claim topics, trusted issuers, validity periods, and revocation status.
- Evaluate transaction rules such as lockups, investor concentration, jurisdiction, or holder count.
- Return approval or a machine readable reason code before the token state changes.
This pattern is a strong fit for frequent secondary transfers where rules can be evaluated entirely from on chain state. It also supports predictable settlement: either the transaction succeeds atomically or it fails.
The weakness is availability dependence. If a validator relies on an external oracle or a state update that has not reached the chain, an otherwise legitimate transfer can fail. Where uncertainty exists, a fail closed posture is generally more defensible for regulated transfers: reject the transaction until eligibility can be established. Fair warning: this can also create an operational bottleneck during a service outage.
A useful policy is to distinguish ineligible, temporarily unverifiable, and administratively pending states. They should not all return the same opaque revert. ERC 1594 style transfer validation supports machine readable restriction reasons, which can help wallets, custodians, and transfer agents explain the failure without exposing confidential investor data.
Asynchronous Transfer Agent Approval
Some offerings require a transfer agent, administrator, or custodian to review transactions before settlement. In that case, a synchronous validator may be insufficient. The architecture can create a pending transfer request, reserve the proposed amount, and require an authorized approval before final execution.
Consider an investor selling a restricted private fund interest. The buyer may be eligible in general, yet the transfer agent may still need to verify subscription documentation, beneficial ownership, or a cap table condition that is not represented on chain. The contract should not simply trust an off chain email approval.
A sound asynchronous workflow usually needs:
• A unique request identifier and immutable request payload
• An expiry time that prevents approval of an old request
• A nonce or version number that prevents replay after a wallet changes status
• Explicit cancellation rights for the sender and administrator
• A reserved balance model, or an approval rule that rechecks available balance at execution
• A final eligibility recheck immediately before settlement
That last step matters. If a claim is revoked between initial review and settlement, the token should not execute based solely on a stale approval. Evidence comparing latency and reliability of synchronous versus asynchronous models is limited, so the choice should follow the legal process and expected transfer volume, not assumed performance claims.
Partitions Versus Separate Token Contracts
Partitions are useful when one legal instrument has balances subject to different conditions. A single token may need separate tracked portions for a locked tranche, unrestricted tranche, employee allocation, or share class. ERC 1410 provides a framework for partitioned balances and different transfer conditions.
Choose partitions when the asset remains economically related and administrators need a unified holder view, unified document set, or controlled movement between states. For example, a tokenized fund interest could use a restricted partition during a lockup, then allow an authorized conversion to a transferable partition after the holding period ends.
Use separate token contracts when the instruments have genuinely independent economics, governance rights, accounting, or legal documentation. A preferred share class and a debt note may belong in separate contracts even if both are issued by the same entity.
The tradeoff is operational. Partitions reduce contract sprawl but increase state machine complexity. The system must define whether cross partition movement is a transfer, a conversion, or an administrative reclassification. That distinction affects audit records, policy checks, and investor reporting.
Lifecycle, Governance, And Upgrade Architecture
Permissioned issuance does not end when tokens are minted. The contract must safely handle issuance, redemption, wallet recovery, freeze actions, forced transfers, claim revocation, document updates, and possibly migration to a successor contract.
Model The Full State Machine
Testing only transfer is not enough. Compliance rules
must be evaluated across every state transition that can change
beneficial ownership, control, or transferability.
| Event | Required Policy Question | Example Failure Mode |
|---|---|---|
| Issuance | May this investor receive this class and amount? | Tokens issued before required claims are active |
| Standard transfer | Are both parties eligible at settlement? | Recipient claim expired after order creation |
| Redemption | Can the issuer reduce this position under the governing terms? | Redemption bypasses required notices or approvals |
| Wallet recovery | Is the replacement wallet controlled by the same verified identity? | Attacker redirects holdings using a weak recovery process |
| Forced transfer | Is the action legally authorized and properly approved? | Controller key is used for an unauthorized seizure |
| Claim revocation | Which future actions must now be blocked? | Revoked investor can move tokens through an old approval |
I would require scenario tests for every transition, including sequences. For instance, test a holder whose accreditation claim expires after a partial transfer, whose wallet is then frozen, and whose balance is later submitted for redemption. Is each operation permitted? Does the system preserve a complete event trail? Can administrators act without bypassing required dual approval? Those are architecture questions, not merely unit test questions.
Use Narrow Administrative Roles
Controller operations are sometimes necessary. ERC 1644 contemplates authorized actions such as forced transfers and redemptions, while ERC 1643 provides document management interfaces for token linked legal materials. But broad controller power can turn a technical convenience into a governance liability.
Instead of one universal owner, use a role graph with distinct authorities:
• Policy administrator updates approved rule parameters within predefined limits.
• Identity administrator manages wallet to identity associations but cannot mint tokens.
• Claims administrator configures trusted issuers and permitted claim topics.
• Emergency operator may pause transfers for a short, auditable period but cannot seize balances.
• Controller committee or multisig authorizes forced transfers, redemptions, and exceptional recovery actions.
• Upgrade authority proposes implementation changes subject to delay, review, and acceptance controls.
This pattern limits blast radius. A compromised identity administrator should not be able to mint new securities. A pause operator should not be able to alter policy or move investor assets. The same principle applies to permissioning frameworks for crypto wallets: authority should be specific, bounded, and observable rather than assumed to be safe because it belongs to an administrator.
Upgradeability Must Be A Legal And Technical Decision
Smart contracts are difficult to patch after deployment. As Open Security Architecture notes in its tokenized asset security pattern, a production vulnerability in an immutable contract cannot be patched like an ordinary application defect. That makes upgrade strategy a pre issuance requirement.
A proxy based upgrade pattern can fix defects and accommodate approved policy changes, but it creates a powerful upgrade authority. An immutable token minimizes that authority, but known bugs or unforeseen operating requirements may require a migration instead.
For regulated assets, I would document four questions before deployment:
- Which contract components are immutable, and which may be upgraded?
- Who can authorize an upgrade, under what threshold, and after what notice period?
- How are balances, partitions, identity bindings, and historical events preserved during migration?
- Can a new rule apply to existing holders retroactively, or only to future transfers?
A practical compromise is to keep the core balance ledger stable while making narrowly scoped policy modules replaceable under a delayed multisig process. That still requires careful storage compatibility testing, an event based migration record, and a legal process for notifying holders. For a broader governance view, review enterprise blockchain architecture in regulated industries, especially where off chain systems remain systems of record for parts of the compliance process.
Choosing The Right Pattern For The Offering
The right architecture depends on the offering’s legal structure, investor base, expected transfer frequency, and operating model. There is no universal best standard.
A Practical Selection Framework
Choose a simple whitelist architecture when the holder population is small, transfers are rare, rules are stable, and a transfer agent already handles most exceptions manually. Avoid it when claims need expiration, issuer provenance, reusable identity, or several independent eligibility regimes.
Choose an ERC 3643 style identity and claims architecture when multiple offerings may rely on the same verified investor identity, when trusted claim issuers are part of the operating model, or when eligibility must be evaluated dynamically. Avoid overengineering it for a one time, tightly controlled issuance with no expected secondary market.
Choose ERC 1400 inspired partitions and controller functions when the instrument needs multiple tranches, transfer states, linked documents, or legally authorized interventions. Avoid partitions when separate instruments have separate economics and governance; forcing them into one contract can make reporting and auditing harder.
Build a custom modular system when the issuer must integrate with a transfer agent, custodian, cap table platform, or jurisdiction specific workflow that standards do not cover cleanly. The tradeoff is clear: customization expands flexibility but also expands the assurance burden.
Design Review Before Issuance
Before minting the first token, I would require a review that answers the following questions in writing:
• Which claims are mandatory for issuance, transfer, redemption, and recovery?
• What does the contract do when a claim expires, is revoked, conflicts with another claim, or cannot be verified?
• Which actions are synchronous, and which require a pending approval workflow?
• Which roles can pause, freeze, recover, mint, redeem, force transfer, upgrade, or change policy?
• How are legal documents versioned and associated with the instrument?
• What event data must an auditor, transfer agent, custodian, or regulator reconstruct later?
Key Takeaways
• Treat identity, claims, compliance, token balances, and governance as separate trust boundaries.
• Validate rules across the entire token lifecycle, not only the ordinary transfer function.
• Use fail closed behavior for uncertain eligibility, while returning useful restricted transfer reasons where appropriate.
• Prefer narrow roles, multisignature approvals, and delays over a single all powerful controller key.
• Select partitions only when a shared instrument truly needs separately governed balance states.
• Decide upgrade and migration behavior before issuance, because post deployment remediation is constrained by immutability and legal continuity.
FAQ: Permissioned Security Token Architecture
What Is A Permissioned Security Token Smart Contract?
It is a token contract that enforces conditions on issuance, ownership, transfer, redemption, and administrative actions. Unlike an unrestricted token, it evaluates eligibility and policy rules before allowing specified state changes.
How Does ERC 3643 Differ Architecturally From ERC 1400?
ERC 3643 centers on identity linked claims, trusted issuers, registries, and compliance modules. ERC 1400 is a broader security token framework that includes transfer validation, partitions, document references, and controller operations. Many institutional designs can use concepts from both.
Should Identity Verification Live Inside The Token Contract?
Usually no. Keep wallet balances in the token contract and wallet to identity relationships in a separate registry. This supports wallet changes, shared identity reuse, and cleaner separation between personal data handling and asset accounting.
What Happens When An Investor Claim Expires Or Is Revoked?
The policy should state this explicitly. A conservative design blocks new transfers or issuances when a required claim is expired or revoked, while allowing only narrowly defined actions such as redemption or an authorized recovery process. The exact treatment depends on the governing documents.
Should Every Transfer Be Validated Synchronously On Chain?
No. Synchronous validation is appropriate when rules can be evaluated from current on chain data and fast settlement matters. Use an asynchronous workflow when an external transfer agent must review documents or cap table conditions, but revalidate eligibility at final settlement.
When Should An Issuer Use Partitions Instead Of Separate Contracts?
Use partitions when a single legal instrument has balance segments with different restrictions, such as lockup states or tranches that may later convert. Use separate contracts when classes have independent economics, governance, disclosures, or accounting treatment.
How Should Forced Transfers, Freezes, And Wallet Recovery Be Authorized?
Use narrowly scoped roles with auditable events and, for high impact actions, multisignature approval and time delays. The authority for each action should map to the legal documentation and should not be concentrated in one operational key.
Sources
• ERC-3643 / T-REX White Paper — ERC-3643
• Tokenised Asset Security Architecture — Open Security Architecture
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.