How to design governance for a multi party enterprise blockchain network
By Jeremy Ryan, Founder & CEO · September 2026
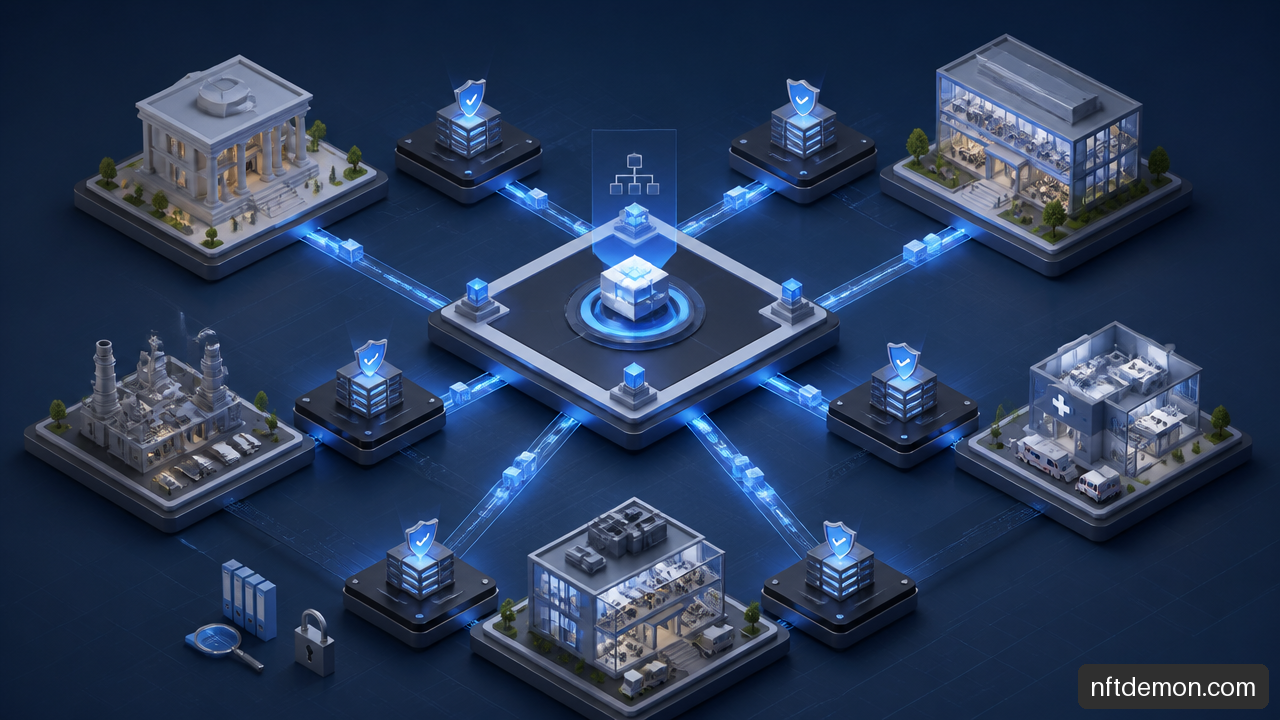
How to design governance for a multi-party enterprise blockchain network starts with a practical premise: a shared ledger cannot solve disagreements about authority. If several organizations operate Nodes, contribute data, rely on Smart Contracts, and carry regulatory risk, the network needs a Governance Model that is as deliberate as its technical architecture.
I recommend treating governance as a control system, not a voting policy. The goal is to define who may decide, who must be consulted, what evidence is required, how exceptions work, and what happens when a participant leaves or a critical incident occurs. Code can enforce some rules. Contracts and operating procedures must handle the rest.
Key Takeaways
• Define decision rights before selecting technology. A Permissioned Network needs explicit authority for membership, validator operations, Smart Contract changes, data access, spending, and incident response.
• Separate protocol, legal, and operational governance. A rule embedded in code is not a substitute for a contract clause, and neither is a substitute for an incident runbook.
• Avoid defaulting to one member, one vote. Voting weight should reflect a defensible combination of business exposure, liability, contribution, and the need to prevent domination.
• Make membership reversible. Admission criteria, notice periods, credential revocation, data retention, and asset migration obligations should be agreed before any participant joins.
• Treat emergency authority as limited and auditable. It should stop immediate harm, not become a shortcut around ordinary consensus.
• Review the model when the network changes. New members, transaction growth, concentration of voting power, material incidents, and shifting incentives are measurable reasons to revisit governance.
Choose The Right Governance Shape
A multi-party enterprise blockchain network needs a structure that fits the commercial relationship behind it. The Distributed Ledger Technology may be shared, but the organizations using it may still be competitors, suppliers, regulators, service providers, or counterparties with very different risk profiles.
Start With The Network Relationship, Not The Blockchain
Before drafting a charter, identify what the network actually coordinates. Is it tracking product provenance? Settling invoices? Sharing compliance evidence? Maintaining a common record of asset ownership? The answer determines what can reasonably be governed together.
A useful first exercise is to map each Stakeholder against three questions:
| Stakeholder Category | What It Contributes | What It Risks | Governance Rights It May Need |
|---|---|---|---|
| Founding member | Capital, transaction volume, operating capacity | Financial liability, service continuity | Strategic vote, committee seat, input rights |
| Transaction participant | Data, assets, business events | Confidentiality, operational dependency | Access rights, issue escalation, limited voting |
| Node operator | Infrastructure and availability | Security and uptime obligations | Technical input, operational accountability |
| Independent service provider | Hosting, identity, audit, or development services | Contractual performance risk | Advisory rights, no automatic control rights |
| Regulator or observer | Oversight expectations | Compliance and evidentiary concerns | Read access or reporting rights, where appropriate |
The distinction between decision rights and input rights matters. Decision rights authorize an outcome. Input rights ensure affected organizations can provide evidence, raise objections, or assess consequences before someone else decides. A logistics provider, for example, may not need to vote on consortium budgeting, but it may need input rights before a data retention rule changes the records it must preserve.
A governance model is credible when authority follows exposure and accountability, not simply organizational size or founding status.
Select A Governance Model Deliberately
A consortium model is often appropriate when multiple organizations need joint control across organizational boundaries. It is not automatically the best choice. Shared control creates legitimacy, but it also creates coordination cost.
| Governance Approach | Best Fit | Primary Advantage | Main Risk |
|---|---|---|---|
| Chief governance | One enterprise bears most liability and controls the commercial process | Fast decisions | Other members may become dependent on one party |
| Custodian governance | A neutral operator can administer the network | Operational simplicity | The custodian may become a concentration point for trust and failure |
| Clan governance | Participants have aligned norms and low formal conflict | Flexible collaboration | Informal expectations can fail under commercial pressure |
| Consortium governance | Several members have meaningful exposure and need shared control | Legitimacy across organizations | Deadlock, coalition behavior, and slow upgrades |
I would choose consortium governance when members have substantial, continuing exposure and no single organization can reasonably dictate the rules without undermining adoption. A consortium can also work well in a low openness environment, where admission is restricted, and a low dominance environment, where no member should control the network alone.
Avoid a full consortium structure when one organization is plainly accountable to customers, regulators, or counterparties for the outcome. In that case, a chief or custodian model may be more honest and more efficient, provided the controlling party accepts the liability that comes with control.
Allocate Voting Power By Exposure, Not Habit
One member, one vote is easy to explain. It is not always fair or stable. A participant processing a small fraction of transactions may have different exposure from a member funding infrastructure, underwriting losses, or carrying regulated obligations.
A practical voting design often combines several elements:
-
Base representation: Every eligible member receives a minimum vote or seat, protecting smaller participants from complete exclusion.
-
Exposure weighting: Additional votes reflect measurable factors such as transaction value, contractual liability, operating cost, or committed capital.
-
Caps: No member may exceed a defined share of voting power, even if it is the largest contributor.
-
Decision classes: Routine matters can use a simple majority, while protocol upgrades, new liability commitments, and dissolution require a supermajority.
-
Conflict rules: A member with a direct commercial interest in a disputed decision must disclose it and may need to abstain.
For example, a network of manufacturers, distributors, and insurers could assign equal seats on the governing council while using exposure-weighted voting for reserve funding. That keeps strategic control broad while recognizing that financial commitments are not evenly distributed.
The formula should be written in the governance charter, reviewed on a predictable schedule, and recalculated from auditable data. If voting weights change only through private negotiation, the network will eventually face a legitimacy problem.
Build Three Connected Control Layers
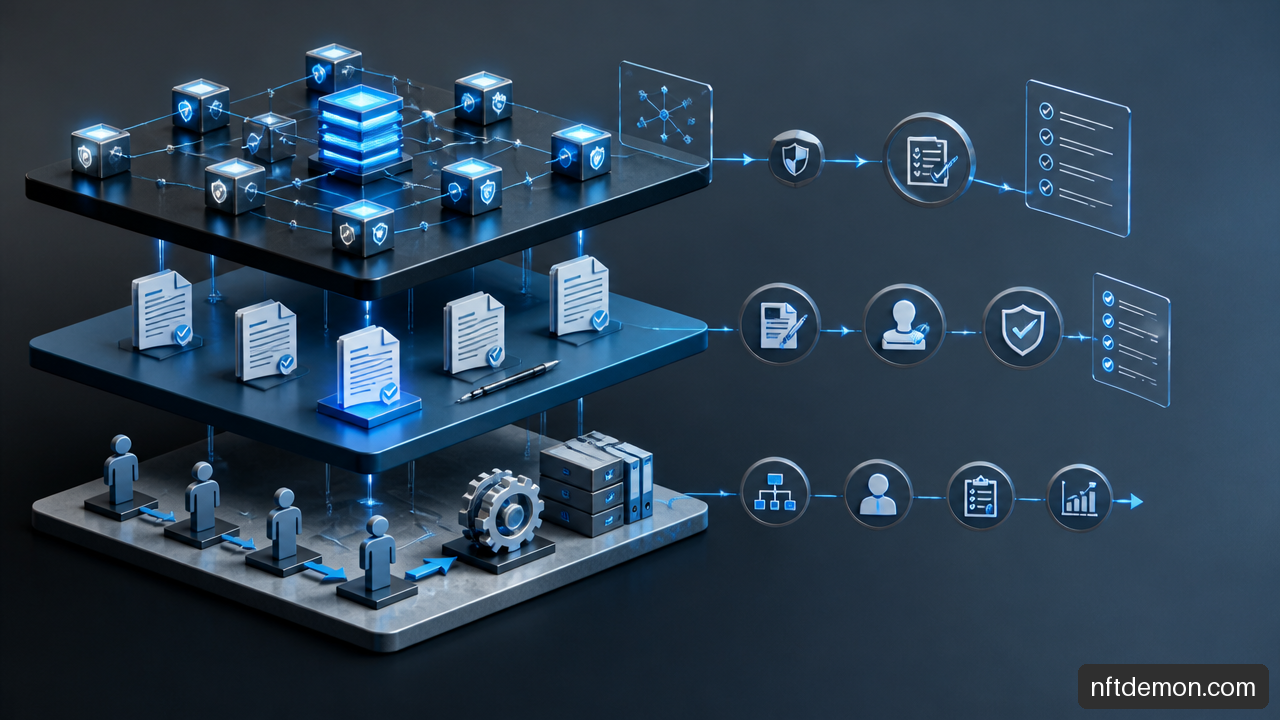
The strongest governance designs distinguish decisions that belong in code, contracts, and operating procedures. These are connected layers, but they should not be collapsed into one document or one committee.
Protocol Governance: What The Network Enforces
Protocol governance covers the endogenous rules inside the platform: the rules the technology can enforce directly. In a Permissioned Network, this includes the Consensus Mechanism, validator or Node membership, identity permissions, transaction endorsement policies, network parameters, and Smart Contract deployment permissions.
The protocol layer should answer questions such as:
• Which organizations may operate validating Nodes?
• What quorum is required for a transaction to be considered final?
• Who can submit a new Smart Contract version?
• Which identities can read, write, approve, or administer specific ledger records?
• What technical logs must be retained to prove administrative actions?
A key design choice is whether a rule needs automatic enforcement. If an unauthorized participant must never access a ledger channel, the rule belongs in protocol access control. If a participant must provide annual insurance evidence, the obligation belongs primarily in the legal and operational layers because the network cannot reliably verify the real world condition on its own.
Legal Governance: What Members Owe Each Other
Legal governance is the exogenous layer: the agreements outside the platform that allocate rights, obligations, liability, intellectual property, confidentiality, and remedies. It should include a founding charter or consortium agreement, participation agreement, service agreements, data terms, and any required policy schedules.
A charter should state, at minimum:
• The network purpose and permitted use cases
• Membership classes and eligibility requirements
• Decision rights, input rights, quorum, and voting thresholds
• Ownership or licensing of shared software, configurations, and data schemas
• Fee, funding, and cost allocation rules
• Confidentiality, data ownership, and permitted disclosure requirements
• Audit rights, record retention expectations, and cooperation duties
• Liability allocation, indemnity, and insurance requirements where appropriate
• Dispute resolution, deadlock, suspension, and termination procedures
The difficult question is often data ownership. A shared ledger record may contain data submitted by one company, validated by others, and relied upon by a third party. “The consortium owns all data” is usually too blunt. Define the rights separately: who owns source data, who may use ledger evidence, who can correct an error, who receives a copy after exit, and how long evidence must be retained.
Fair warning: legal requirements vary by transaction type, sector, jurisdiction, and contractual relationship. A governance charter should be reviewed by qualified legal and compliance functions rather than treated as a generic blockchain template.
Operational Governance: What Happens On A Normal Tuesday
Operational governance turns policy into recurring behavior. It assigns accountable owners for monitoring, approvals, audits, service performance, user support, and incident coordination.
| Control Function | Typical Accountable Owner | Evidence To Preserve |
|---|---|---|
| Identity and access review | Security lead or access committee | Approval records, access logs, recertification results |
| Node availability and patching | Technical operations lead | Uptime reports, maintenance records, incident tickets |
| Smart Contract release | Change advisory group | Test results, signoffs, version history, rollback plan |
| Data quality exceptions | Business data steward | Correction request, validation evidence, resolution record |
| Financial and policy compliance | Compliance or risk lead | Control attestations, audit trail, exception register |
| Charter compliance | Governing council or secretariat | Meeting minutes, votes, disclosures, enforcement actions |
This mapping matters because “the consortium” cannot perform a control. A named role, person, or member organization must be accountable. The governing council can set policy, but a security function should operate access reviews. Legal can interpret contractual duties, but it should not silently control production deployments.
Establish Formal Change Control
Every enterprise network changes. Smart Contracts may need a bug fix. A validator may need replacement. A privacy configuration may become unsuitable. Governance should define the path before the first urgent request arrives.
A reliable change-control process has five stages:
-
Proposal: A member submits a standardized request stating the business reason, affected records, technical scope, security impact, cost, and rollback approach.
-
Assessment: Technical, security, legal, compliance, and business owners evaluate the request. Their role is not identical; each signs off on the risk they own.
-
Decision: The designated authority applies the correct threshold. A Smart Contract that alters payment obligations should require a higher threshold than a dashboard enhancement.
-
Controlled deployment: The change moves through defined environments, receives documented approvals, and is deployed during an approved release window.
-
Verification and recordkeeping: The network confirms expected behavior, preserves the decision record, and triggers remediation if the outcome differs from the approved design.
Emergency override powers deserve special care. They may be necessary to isolate a compromised Node, suspend a vulnerable Smart Contract, or halt a harmful transaction path. But emergency authority should be narrow, time-limited, and independently reviewable. The override should create an immutable event record, require prompt notice to members, and expire unless the ordinary governance process ratifies or replaces it.
Run Membership Change And Dispute Processes
Membership and conflict are where governance becomes real. A network can survive a slow committee meeting. It may not survive an unclear exit, a blocked upgrade, or a dispute over whose records remain available after termination.
Make Admission And Exit Mechanisms Enforceable
Admission should be more than an invitation and technical onboarding. Establish objective eligibility criteria, including legal identity verification, financial standing if relevant, security capability, agreement acceptance, technical interoperability testing, and confirmation that the participant can meet data-handling obligations.
Exit needs equal attention. The exit protocol should specify:
• Required notice periods and the circumstances permitting immediate suspension
• The process for revoking credentials, certificates, API access, and Node permissions
• Whether an exiting member must continue serving open transactions or disputes
• The treatment of outstanding fees, collateral, assets, and contractual obligations
• Data export rights, evidence retention duties, and restrictions on deleting shared records
• Node decommissioning, key rotation, and validation of backup handling
• The point at which the member loses voting rights and committee access
Consider a distributor leaving a product traceability network after an acquisition. The company may need historical ledger evidence for recalls, audits, and litigation, but it should not retain live access to future competitor data. That is not a technical detail. It is a governance decision requiring coordinated legal terms, access controls, and an operational offboarding checklist.
Design Deadlock And Dispute Resolution Before Launch
A dispute process should identify both the trigger and the authority. “Members will negotiate in good faith” may belong in a contract, but it is insufficient as a mechanism for restoring operations.
A practical escalation model can work as follows:
-
Operational resolution: Designated representatives attempt to resolve a documented issue within a defined period.
-
Committee review: If unresolved, the matter moves to the responsible technical, commercial, or compliance committee with evidence and recommended options.
-
Executive escalation: A governing council addresses issues involving material cost, liability, membership rights, or platform direction.
-
Independent determination: If deadlock persists, a predefined neutral expert, mediator, or arbitration process addresses the limited question at issue.
-
Continuity protection: The charter specifies what continues while the dispute is pending. For example, the existing Smart Contract version remains active unless an emergency threshold is met.
Tie-break authority should be limited by subject. A neutral technical steward may resolve whether a release meets an agreed test criterion, but should not decide how members allocate commercial liability. A council chair may manage procedure, but should not receive an undisclosed casting vote on matters that advantage its employer.
Review Governance When Conditions Change
Governance should not be revised only after a crisis. Establish review triggers that force a structured discussion when the network changes materially.
| Review Trigger | Why It Matters | Typical Response |
|---|---|---|
| New member category joins | New interests or regulatory duties may enter the network | Reassess voting, access classes, and committee representation |
| Transaction volume or value rises materially | Operational and liability exposure increases | Review funding, controls, audit scope, and thresholds |
| One member gains concentrated influence | Shared control may become nominal | Apply vote caps or rebalance representation |
| Significant security or data incident | Existing safeguards may be inadequate | Conduct root-cause review and amend runbooks or protocol controls |
| Repeated deadlock or missed votes | Decision design is not functioning | Adjust quorum, delegation, escalation, or tie-break procedures |
The right cadence depends on the network. Annual review may be adequate for a stable consortium with low transaction volume. Quarterly reviews may be justified during launch, rapid membership growth, or a period of regulatory change. The important point is to define measurable triggers instead of relying on vague promises to revisit governance “as needed.”
Frequently Asked Questions
What Is Governance In A Multi-Party Enterprise Blockchain Network?
Governance is the system of decision rights, input rights, accountability, and enforcement used to operate a shared blockchain network. It covers more than voting. It includes membership, access, Smart Contract changes, funding, data rights, audit evidence, incident response, and dispute resolution.
Who Should Have Decision Rights In An Enterprise Blockchain Network?
Decision rights should go to parties with meaningful accountability, risk exposure, and operational responsibility. Not every user needs a governing vote. Participants with limited exposure may instead receive input rights, access rights, or escalation rights. The charter should distinguish each category clearly.
How Should A Consortium Decide Voting Power?
Use a documented formula based on the decision type. Equal representation may suit strategic questions, while exposure-weighted voting may better fit financial commitments. Add caps so a large participant cannot take control merely through volume or funding. Supermajority thresholds are appropriate for constitutional changes, major protocol changes, and dissolution.
How Do You Govern Smart Contract Upgrades Across Organizations?
Use formal Smart Contract change control: documented proposal, multi-function impact assessment, appropriate voting threshold, tested deployment, rollback plan, and retained evidence. The governance model should specify who can propose, approve, deploy, pause, and verify a change. Emergency action should be restricted to defined safety events.
How Do You Onboard And Offboard Members Safely?
Onboarding should verify eligibility, agreement acceptance, identity, security capability, and technical interoperability. Offboarding should revoke credentials, address Nodes and keys, settle obligations, preserve required evidence, and define access to historical records. The process must coordinate protocol permissions, contractual rights, and operating procedures.
What Is The Difference Between Protocol Governance And Legal Governance?
Protocol governance consists of enforceable platform rules, such as access permissions, validation rules, and Smart Contract deployment controls. Legal governance consists of agreements allocating ownership, liability, confidentiality, remedies, and member duties. A sound network requires both because code cannot resolve every commercial or regulatory obligation.
How Do You Prevent One Member From Controlling The Network?
Set voting caps, require diverse committee representation, separate technical administration from strategic control, publish decision records, and use higher thresholds for material changes. Also review concentration periodically. A network can appear collaborative at launch yet become controlled by one participant after acquisition, growth, or member exits.
How Often Should Blockchain Governance Be Reviewed?
Review it at least on a defined recurring cadence and whenever objective triggers occur, such as material membership changes, sharp transaction growth, a security incident, repeated disputes, or concentrated voting power. Governance that is never tested against changing incentives becomes an assumption rather than a control.
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.