How enterprises manage permissions, upgrades, and blockchain disputes
By Jeremy Ryan, Founder & CEO · September 2026
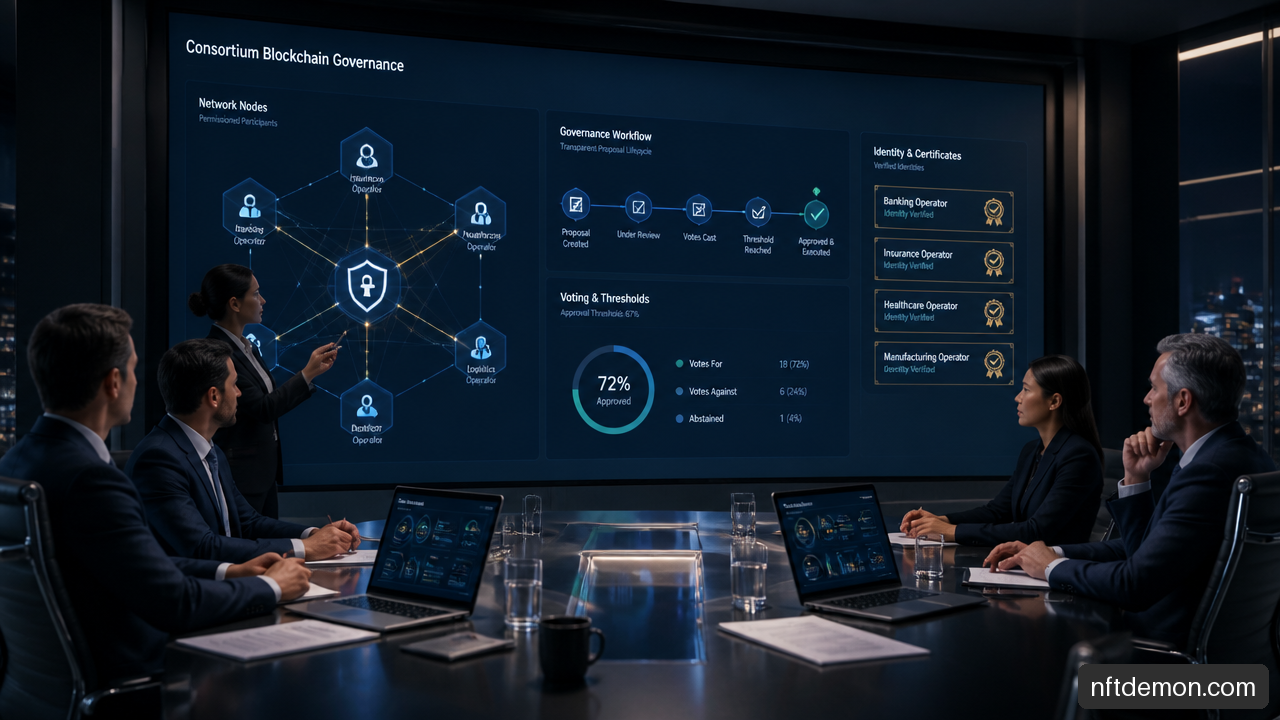
How enterprises manage permissions upgrades and disputes on a blockchain network comes down to one discipline: translating a consortium’s commercial agreement into enforceable technical controls. A permissioned blockchain does not remove governance. It makes governance executable, visible, and difficult to ignore after a disagreement begins.
For decision makers, the practical question is not simply who can access the network. It is who may join, operate infrastructure, submit transactions, approve a smart contract change, invoke an emergency pause, inspect evidence, and make the final call when participants cannot agree. I recommend treating each of those as a separate governed decision rather than relying on an informal steering committee.
Build A Permission Model That Separates Technical Layers
The most durable enterprise governance models begin by separating network membership, node permissioning, and account authorization. These controls are connected, but they answer different questions. Combining them into one broad label such as “access” creates ambiguity precisely when a member is suspended, a validator fails, or a user’s role changes.
Distinguish Membership, Nodes, And Accounts
A consortium member is an organization with contractual rights and obligations. A node is infrastructure operated by that organization or a delegated service provider. An account is an identity, human or machine, that invokes an application function. One organization may operate several nodes and issue many accounts. Conversely, an external auditor may need read only access without membership rights or validator authority.
The distinction matters because remedies must fit the layer where the problem exists. If a former employee retains an application credential, revoking the account may be enough. If a member organization has breached a security obligation, the consortium may need to suspend its node connections, revoke certificates, and limit data access while a dispute proceeds.
The enterprise blockchain architecture guide’s treatment of node and account controls makes this separation explicit: node permissioning governs peer connectivity, while account authorization and application contracts determine who can submit or perform particular actions.
| Control Layer | Decision It Governs | Typical Technical Control | Primary Failure If Unclear |
|---|---|---|---|
| Consortium membership | Whether an organization belongs to the network | Membership agreement, identity onboarding | An unvetted entity gains rights by implication |
| Node permissioning | Which infrastructure may connect or validate | Allowlists, certificates, validator configuration | A removed party continues operating a peer or validator |
| Account authorization | Which identity can read, submit, approve, or administer | IAM integration, roles, smart contract checks | A valid employee credential receives excessive power |
| Data access | Which records or private collections a party may view | Channels, private data rules, encryption policies | Commercially sensitive records become visible to the wrong party |
Turn Roles Into A Governed Decision Matrix
A role chart is useful. A decision matrix is better because it states who can propose, review, approve, implement, challenge, and audit a change. It should cover routine decisions as well as moments that invite conflict.
| Governed Decision | Proposal Right | Approval Model | Execution Authority | Evidence Required |
|---|---|---|---|---|
| Admit a new organization | Sponsor member or governance office | Supermajority vote | Network administrator after approval | Due diligence record, membership resolution |
| Suspend an account | Security lead or designated manager | Delegated authority within policy | Identity administrator | Incident ticket, reason, timestamp |
| Remove or suspend a member node | Security committee or governing body | Enhanced quorum | Designated infrastructure operator | Technical finding, vote, certificate revocation record |
| Change validator set or ordering configuration | Technical committee | Supermajority or affected member consent | Authorized network operators | Impact assessment, configuration artifact |
| Upgrade chaincode or smart contracts | Product owner or member sponsor | Endorsement and governance approval | Release manager | Test results, approvals, deployment record |
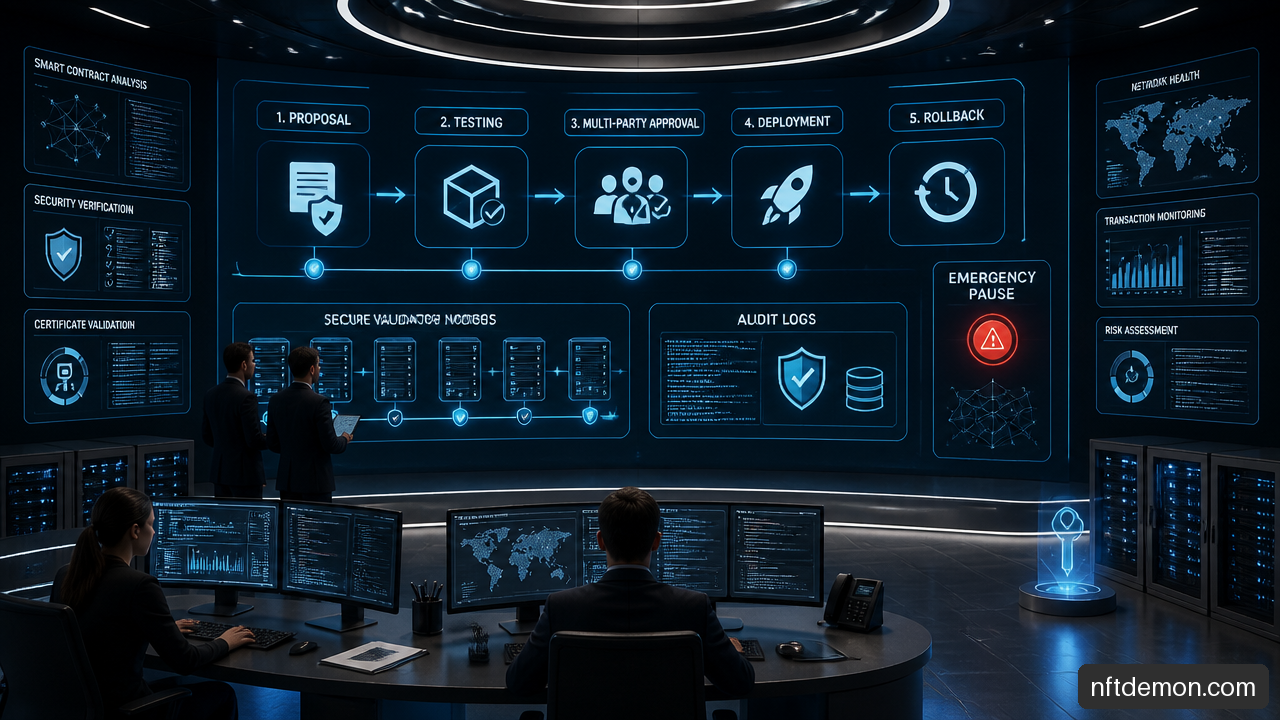
| Invoke emergency pause | Named emergency authority | Narrow delegated authority | Incident commander | Trigger, scope, expiration, review record |
| Escalate a dispute | Any affected member | No vote needed to initiate | Secretariat or neutral administrator | Notice, factual record, requested remedy |
A matrix prevents a common governance failure: everyone assumes someone else has authority, while the person who acts cannot prove that authority afterward. The governing agreement should mirror this matrix in plain language, and the network configuration should enforce the portions that can be technically enforced.
Define What “Least Privilege” Means In Operations
Least privilege cannot stop at user accounts. It should apply to administrative keys, certificate authority operations, ordering service access, deployment rights, and emergency controls. A developer who can install code should not automatically be able to commit it. A network operator who can restart a node should not be able to add a new member independently.
The governance analysis in The Boon and Bane of Blockchain: Getting the Governance Right supports this broader view: governance among participating organizations must define permissioning, decision authority, and dispute handling, including questions of privacy, ownership, funding, and liability.
Practical principle: A permission should be traceable to a role, a role should be traceable to a governance decision, and that decision should be traceable to retained evidence.
Control Upgrades With Evidence And Thresholds
A blockchain upgrade is not one event. It can involve a smart contract release, chaincode lifecycle action, configuration update, certificate rotation, validator change, data schema revision, or a modification to an endorsement policy. Each affects a different trust boundary. Treating every change as a standard IT release is too loose; requiring a full consortium vote for every minor patch is too slow.
Classify Changes Before Setting Approval Thresholds
I recommend using a risk based classification that matches voting thresholds to reversibility, security impact, commercial impact, and the number of members affected. The threshold should be known before a proposal is filed, not negotiated after stakeholders take positions.
| Change Class | Example | Suitable Approval Approach | When To Avoid It |
|---|---|---|---|
| Routine operational change | Monitoring adjustment or nonfunctional node maintenance | Delegated technical approval with notice | Avoid if the change alters transaction validation or data visibility |
| Material application release | New chaincode function or pricing rule | Multi organization endorsement plus governance approval | Avoid simple majority where one member bears disproportionate commercial risk |
| Trust anchor change | Certificate authority rotation, ordering service reconfiguration, validator addition | Supermajority with documented security review | Avoid rushed approval unless emergency criteria are met |
| Constitutional change | Voting thresholds, member rights, data ownership rules | Supermajority, potentially unanimous consent for affected rights | Avoid treating this as an ordinary software release |
| Emergency action | Pause a vulnerable function or isolate a compromised node | Preauthorized, time limited authority followed by review | Avoid using emergency authority for a strategic disagreement |
A short voting threshold may feel efficient at launch, but it can become a governance liability as the consortium grows. On the other hand, unanimity protects minority participants while giving every member a veto over routine modernization. The workable middle ground is usually differentiated thresholds with clear categories.
Require A Complete Upgrade Record
Every upgrade should create an evidence package that survives personnel changes and later disputes. This is not paperwork for its own sake. If an update causes invalid transactions, data access concerns, or an outage, the consortium needs to reconstruct exactly what was proposed and what each party approved.
A defensible upgrade record includes:
-
Proposal: purpose, owner, scope, affected organizations, and expected business effect.
-
Technical assessment: code version, architecture impact, dependency changes, security review, test environment results, and rollback feasibility.
-
Commercial and compliance assessment: data handling impact, allocation of costs, contractual changes, regulatory implications, and affected service levels.
-
Approval record: eligible voters, quorum, votes cast, abstentions, conditions, endorsement policy evidence, and timestamps.
-
Deployment record: exact artifacts deployed, configuration hashes where relevant, execution personnel or systems, and production validation.
-
Rollback and post implementation record: predefined triggers, decision authority, rollback result, incident references, and lessons captured.
The chaincode lifecycle in Hyperledger Fabric is a useful example of making shared approval technical rather than informal. Enterprise guidance on Hyperledger Fabric describes multi organization approval for chaincode upgrades and related network governance choices, reducing the prospect of unilateral code changes by one participant.
Use Emergency Powers Carefully
Emergency powers exist because a consensus mechanism cannot substitute for incident response. A compromised administrative credential, critical smart contract defect, or faulty validator configuration may require action before a normal committee can convene.
The design challenge is preventing the emergency pathway from becoming a back door for ordinary political disagreement. Limit emergency powers by scope, duration, and trigger. For example, a designated incident authority might isolate a node for 24 hours where there is credible evidence of compromise, but not permanently remove a member or change commercial rules.
Mandatory Review Is The Safeguard
Every emergency action should expire automatically unless the normal governance process ratifies it. A post use review should assess four points:
• Whether the stated trigger existed
• Whether the action stayed within delegated authority
• Whether any party suffered avoidable harm
• Whether the policy, controls, or recovery plan need revision
This creates accountability without forcing decision makers to hesitate during a genuine security event.
Design Disputes Into The Network Constitution
Disputes are not a side issue for legal counsel to address after deployment. They are an operating condition in multi party systems. Members can disagree over transaction validity, release costs, data ownership, missed obligations, conflicts of interest, or whether an emergency action was justified. Each category needs a different path because the evidence, remedy, and decision maker differ.
Match The Remedy To The Dispute Layer
| Dispute Type | Typical Question | First Response | Possible Resolution |
|---|---|---|---|
| Code or configuration defect | Did approved code behave contrary to specification? | Freeze affected function, preserve logs and artifacts | Patch, rollback, corrective release, cost allocation |
| Transaction validity dispute | Was a transaction properly endorsed, authorized, and ordered? | Review signatures, endorsement evidence, timestamps | Confirm record, create compensating transaction, escalate factual dispute |
| Data access conflict | Did a participant access or retain data beyond its rights? | Revoke access where justified, preserve evidence | Access correction, remediation, contractual claim |
| Governance deadlock | Did voting rules prevent a required decision? | Use escalation timetable and mediation path | Tie break, independent expert determination, amended proposal |
| Commercial breach | Did a member fail to fund, operate, or perform an agreed obligation? | Issue formal notice and calculate impacts | Cure period, damages process, suspension, exit procedure |
There is no universal answer to whether a dispute should be resolved on chain. A code defect may be evaluated through on chain records and off chain testing. A funding dispute may depend largely on invoices, contracts, and legal obligations outside the ledger. The better model is usually hybrid: use blockchain records as authenticated evidence, route operational questions through defined governance, and retain an enforceable off chain legal route for issues the protocol cannot decide.
The World Economic Forum’s work on blockchain transaction dispute resolution explains that dispute resolution can be built into governance, including choices around jurisdiction and opt out provisions. That framing is useful because it treats dispute design as a configurable element of network governance rather than a static legal appendix.
Prevent Deadlock Before It Reaches Production
Deadlock usually arises from a poorly specified threshold, not from a lack of goodwill. Consider a five member consortium that requires four votes for a major release. If two members are commercially affected in opposite ways, a three to two vote can stall the upgrade indefinitely even when the network’s technical risk is mounting.
A mature agreement defines a sequence rather than merely stating “members will negotiate in good faith.” A practical escalation path may include:
-
A short technical fact finding period with preserved evidence and no change to the disputed production state unless emergency criteria apply.
-
A governance meeting where the proposal sponsor must present alternatives, including the cost of deferral.
-
A neutral technical expert determination for factual questions such as compatibility, security exposure, or transaction reconstruction.
-
Mediation for commercial allocation issues.
-
A named final authority, arbitration mechanism, or jurisdictional route if the matter remains unresolved.
The final authority should be limited. A neutral expert can decide whether a configuration violates agreed technical requirements, but should not rewrite commercial rights. A governing board may settle funding disputes but should not override cryptographic evidence of transaction validation.
Make Exit, Evidence, And Data Retention Explicit
Member exits are especially sensitive because a departing organization may have active transactions, copies of shared data, issued credentials, and outstanding financial obligations. The network should specify what happens to each asset and record category.
At minimum, an exit procedure should address certificate and key revocation, node disconnection, treatment of private data copies, continuing audit access, in flight transaction settlement, archival obligations, and the circumstances under which records remain visible after departure. “Delete everything” is rarely realistic where legal retention obligations apply. “Retain everything forever” may conflict with privacy commitments. The agreement needs a defined retention basis and a documented process for exceptions.
Key Takeaways
• Enterprises should separate consortium membership, node permissioning, account authorization, and data access instead of calling all of them “permissions.”
• Smart contract upgrades, validator changes, certificate rotations, and ordering service changes should use different approval thresholds because they create different risks.
• A complete proposal, review, approval, deployment, and rollback record is essential for auditability and later dispute reconstruction.
• Emergency powers should be narrow, time limited, technically constrained, and subject to mandatory post use review.
• Dispute resolution works best as part of the network constitution, connected to on chain evidence and enforceable off chain obligations.
• Exit rules should address data, keys, certificates, evidence access, and in flight obligations before the first production transaction.
Frequently Asked Questions
How Do Enterprises Decide Who Can Join A Permissioned Blockchain Network?
They usually require an organizational sponsor, due diligence, legal acceptance of consortium obligations, identity issuance, and a formal admission vote or delegated approval. The admission decision should distinguish membership rights from technical access. A new member may be admitted commercially before it is authorized to operate a validator or access all historical data.
Who Approves Smart Contract Or Chaincode Upgrades In A Consortium?
Approval should be defined by the upgrade category and encoded, where possible, in endorsement and lifecycle controls. Material changes commonly require approvals from multiple organizations, not merely the operator that prepared the release. The appropriate threshold depends on affected rights, reversibility, and security impact.
What Happens If One Enterprise Blocks A Network Upgrade?
The answer depends on the agreed threshold. If that enterprise has a contractual veto, the consortium must use its escalation process rather than bypass it. If the member is withholding approval outside agreed criteria, mediation, expert review, or a final decision authority may be available. The agreement should also define the operational cost of delay and when emergency action is justified.
How Are Emergency Pauses Or Rollbacks Governed?
A designated authority may act only when predefined security or operational triggers are met. The action should be narrowly scoped, recorded immediately, and expire unless ratified through normal governance. A rollback is not automatically safer than a patch; it can create data consistency issues, so the recovery plan must be tested before an incident occurs.
How Are Validator Changes And Certificate Rotations Approved?
These should be governed as trust anchor changes, not treated as ordinary maintenance. The proposal should identify affected consensus participants, certificate chains, operational dependencies, transition timing, and rollback steps. A higher quorum is often appropriate because a faulty validator or certificate authority change can affect the integrity of transaction validation.
How Do Enterprises Handle Disputes Over Transaction Validity?
They preserve the relevant transaction identifiers, signatures, endorsement evidence, ordering records, smart contract version, and applicable authorization rules. If the ledger record is technically valid but commercially incorrect, the usual remedy may be a compensating transaction rather than deletion. The legal agreement should clarify whether and how parties can seek remedies outside the network.
What Should Happen To Private Data When A Member Exits?
The exit process should revoke credentials, disconnect infrastructure, identify retained records, and apply the agreed retention and deletion rules. It should also preserve evidence necessary for audits and unresolved disputes. The key is specificity: each data category needs an owner, retention basis, access rule, and documented action when membership ends.
What Is The Best Way To Design Governance Before Production Launch?
Start with the decision matrix, then test it against difficult scenarios: a member refuses an upgrade, a validator is compromised, an emergency pause is misused, a participant exits during a live transaction, or a data access dispute arises. If the governance model cannot answer who acts, what evidence is required, and who decides a tie, it is not ready for production.
Sources And References
• World Economic Forum — Dispute resolution for blockchain-based transactions
• Journal article — The Boon and Bane of Blockchain: Getting the Governance Right
• Enterprise Blockchain Architecture Guide
• Enterprise Blockchain with Hyperledger Fabric
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.