Enterprise consortium blockchain architecture trade offs for supply chain validation
By Jeremy Ryan, Founder & CEO · September 2026
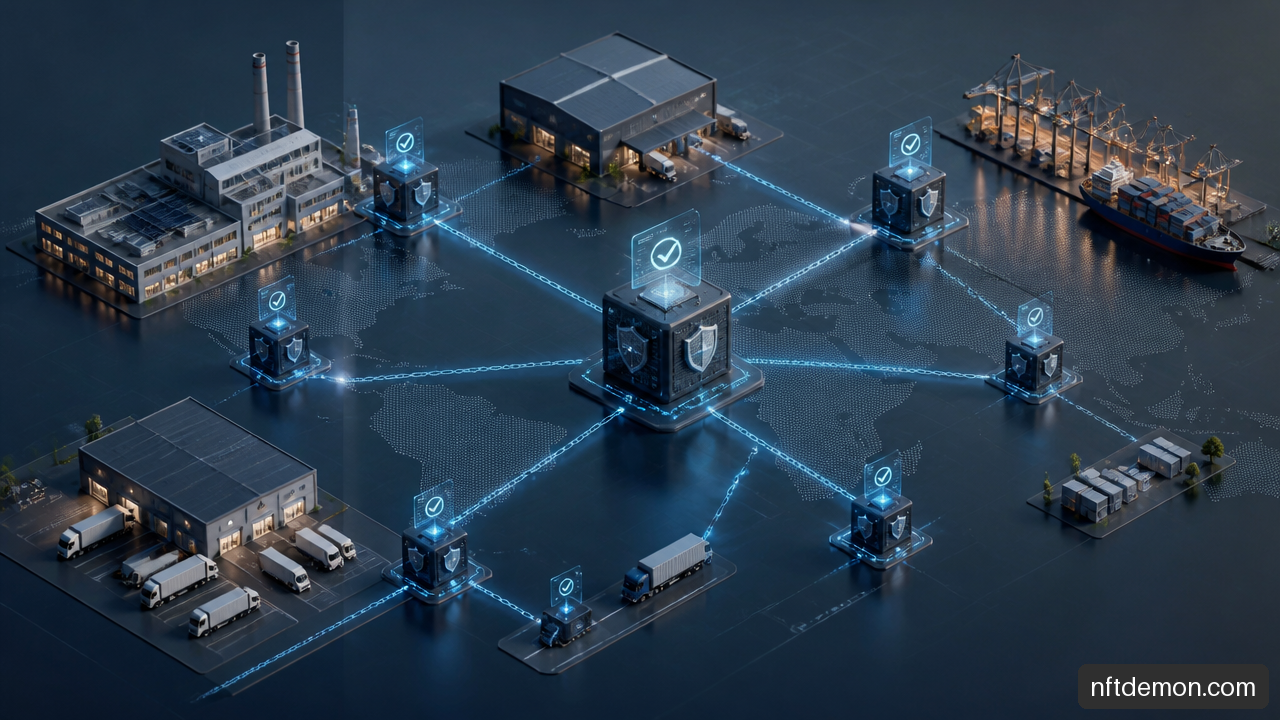
Enterprise consortium blockchain architecture trade-offs for supply chain validation are rarely about whether a distributed ledger can record events. It can. The harder question is whether multiple organizations can govern, fund, integrate, and trust that ledger well enough for it to improve a real validation process.
A consortium chain is most useful when suppliers, manufacturers, logistics providers, distributors, auditors, or regulators need a shared evidence trail but no single participant should own the system of record. It is not a universal replacement for ERP, WMS, EDI, or a conventional database. I would treat it as a coordination layer for high-value events: custody transfers, origin attestations, quality releases, recall triggers, compliance certificates, and exceptions that regularly cross organizational boundaries.
Architecture Trade-Offs and Validation Fit
What The Consortium Model Actually Changes
A consortium blockchain is a permissioned ledger governed by several known organizations. Members are admitted through agreed identity and membership rules, while a limited validator set confirms transactions and produces blocks. This differs from a private blockchain, where one enterprise retains effective control, and from a public blockchain, where anyone can generally inspect or participate according to protocol rules.
For supply chain validation, the material difference is shared control over evidence. A supplier can attest that a serialized component passed inspection. A carrier can confirm pickup and delivery. A manufacturer can record transformation of the component into a finished product. The chain creates a common ordering and history of those claims.
That does not prove that each claim is true in the physical world. It proves who submitted it, when it was accepted under the network rules, and whether the record was changed afterward. If a warehouse worker scans the wrong pallet, or a compromised sensor reports a false temperature, the blockchain preserves bad data with excellent integrity. That is why identity controls, device attestation, exception workflows, and source-system reconciliation matter at least as much as ledger design.
The NYU Stern analysis of supply chain finance blockchain models describes consortium validation as being performed by a prespecified group using mechanisms such as Proof of Authority and Practical Byzantine Fault Tolerance variants. That arrangement is attractive because the network can reach finality quickly without the energy and participation model of an open public chain.
| Architecture | Best Fit | Primary Advantage | Primary Constraint |
|---|---|---|---|
| Centralized database | One accountable enterprise and limited partner disputes | Lowest integration and operating complexity | Partners must trust the owner and its audit process |
| Private blockchain | One operator needs controlled tamper evidence across internal divisions | Strong control and predictable operations | It does not materially distribute governance |
| Consortium blockchain | Multiple firms need shared validation and no single neutral operator is accepted | Joint control, auditable workflows, restricted participation | Governance and onboarding are operationally difficult |
| Public blockchain | Open verification or broad external composability is central | Maximum transparency and broad independent verification | Confidentiality, cost predictability, and data exposure require careful design |
A supply chain consortium should therefore be judged against a plain alternative: a shared database operated by a neutral service provider, with signed APIs, strong logs, and independent audit rights. If that alternative meets the trust requirement, a consortium chain may add cost without changing the outcome.
The Stop Or Go Decision
I recommend a consortium design only when all of the following conditions are substantially true:
• At least three legally or commercially independent organizations must validate the same event stream.
• A single operator would face credible objections over control, evidence ownership, or dispute resolution.
• The workflow has recurring high-cost disputes, compliance exposure, recalls, counterfeiting risk, or financing consequences.
• Participants can commit to common identifiers, event definitions, integration responsibilities, and service levels.
• The anticipated savings, risk reduction, or revenue opportunity exceeds the cost of operating a joint network.
A network with only two parties can still use a ledger, but bilateral APIs, digitally signed records, and an escrowed audit log may be simpler. Likewise, a network with dozens of firms is not automatically stronger. Every additional member expands geographic coverage and reduces control concentration, yet it also adds identity administration, contractual negotiation, support requirements, and change-control delay.
The Frontiers enterprise consortium evaluation framework emphasizes business value, participant roles, IT security requirements, connected systems, interoperability, and cost-benefit assessment. That is the right order of operations. Starting with a preferred blockchain framework reverses the decision.
A useful pilot measures more than transaction count. It should establish a baseline for dispute resolution time, recall investigation time, manual document handling, duplicate reconciliation, rejected deliveries, and partner onboarding effort. If the pilot produces immutable records but does not improve one of those business outcomes, it has not yet justified production architecture.
Consensus, Finality, And Performance Limits
Permissioned supply chain networks commonly choose Proof of Authority when validators are known and governance is tightly controlled. BFT-style mechanisms are more appropriate when the network needs resilience against a defined number of malicious or failed validators. Both can provide deterministic finality: once the transaction is finalized, it is not expected to be reorganized later.
A fixed-validator model commonly requires a quorum of designated nodes to sign blocks. The Cardiff University supply chain blockchain white paper explains this quorum-based approach for consortium designs. The architectural benefit is clear: a single offline member does not necessarily halt the chain. The trade-off is that quorum rules become a business decision as much as a technical one.
For example, a seven-validator network might tolerate some unavailable nodes while still finalizing events. But if four validators belong to one corporate group, the apparent distribution is misleading. The fault model must account for ownership, cloud-provider concentration, geographic region, and shared administrative access, not merely node count.
Throughput claims also deserve skepticism. Permissioned chains can process events quickly under controlled conditions, but end-to-end supply chain latency is often dominated by data capture, endorsement policies, API retries, document retrieval, and human exception handling. A transaction that needs endorsements from a manufacturer, laboratory, carrier, and customs broker will move no faster than its slowest approval path.
Privacy Is A Data-Placement Problem
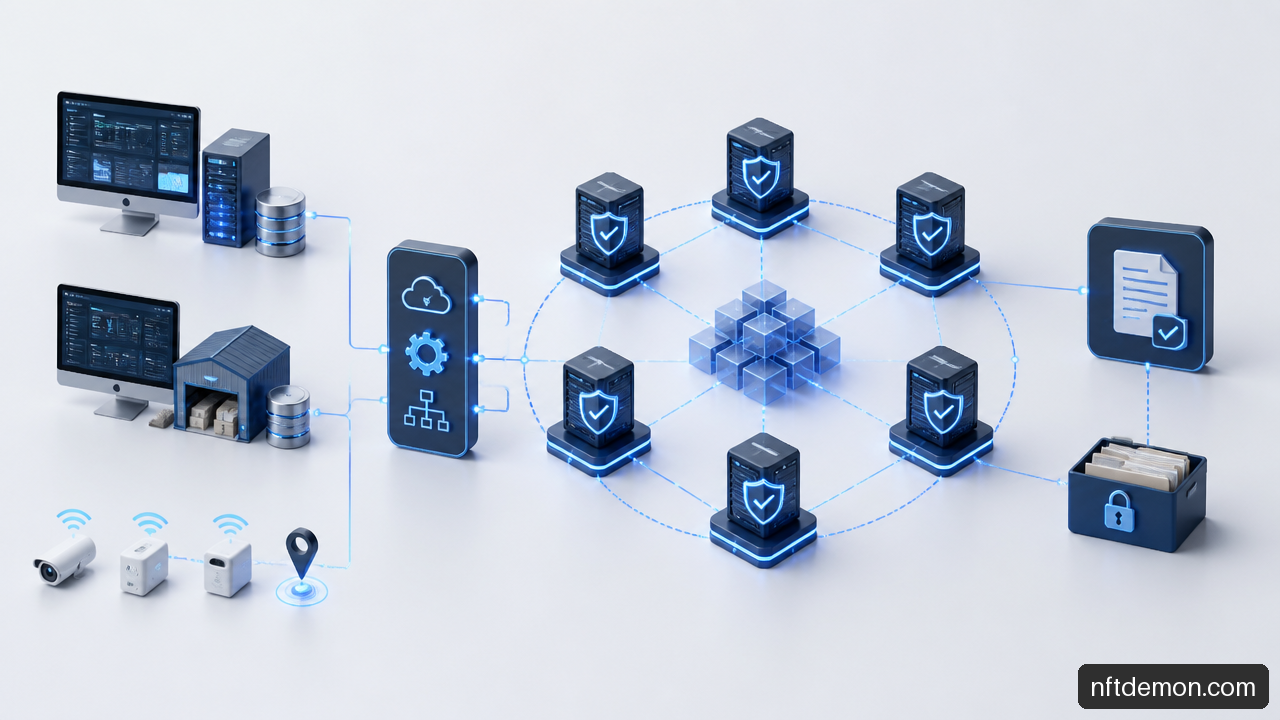
Competitors can share validation evidence without sharing every commercial detail. The practical pattern is to place minimal proofs, event references, authorization states, and document hashes on-chain while storing large files and sensitive fields in controlled off-chain repositories.
Consider a pharmaceutical distributor validating a shipment handoff. The ledger may store the product identifier, shipment event, timestamp, custody parties, document hash, and compliance status. The temperature file, customer price, purchase order, and personally identifiable information remain in an approved repository. Authorized parties retrieve those records through policy-controlled access.
This pattern avoids turning the ledger into a permanent repository of sensitive data. It also creates a challenge: the off-chain data must remain available, access-controlled, retained according to policy, and cryptographically linked to the on-chain proof. A hash proves that a specific document version existed. It does not guarantee the document remains retrievable ten years later.
Data residency requires another layer of discipline. A global ledger replica can create problems if regulated data is replicated into prohibited jurisdictions. Separate application layers, regional storage, field-level minimization, and region-specific nodes can reduce exposure. In strict cases, the global chain may record only non-sensitive proofs, while the underlying documents stay within the applicable legal region.
The enterprise blockchain supply chain identity assessment is a useful companion consideration here: validation is only as credible as the identity binding between a person, organization, device, and submitted event.
Governance, Security, And Operating Reality
Governance Is The Product, Not Administration
The ledger software is usually the easier part. Governance determines who may join, run validators, submit data, view records, propose smart-contract changes, pay operating costs, and resolve disputes. If those rights are vague, the technical architecture will eventually reflect the ambiguity as blocked upgrades, inconsistent data, or competing versions of the truth.
The Chainlink overview of consortium blockchain architecture identifies setup coordination, shared governance, and collusion risk as core constraints. These are not theoretical drawbacks. A small validator set can be efficient, but it can also allow a dominant buyer, carrier group, or manufacturer coalition to influence membership decisions, validation rules, or access to evidence.
A workable charter should define at least the following:
-
Membership and exit rules: eligibility, due diligence, suspension rights, and what happens to records and access when a member leaves.
-
Voting and veto boundaries: which matters require simple majority, supermajority, independent review, or unanimous approval.
-
Technical change control: emergency patches, smart-contract upgrades, schema versioning, and backward compatibility.
-
Commercial operations: shared costs, cloud responsibilities, support coverage, insurance, and liability allocation.
-
Dispute handling: evidence standards, response periods, arbitration paths, and remediation for incorrect submissions.
Designing governance for multi-party blockchain networks should begin before node deployment, because governance cannot be retrofitted cleanly once members depend on a production evidence trail.
Failure Modes Have Visible Symptoms
Governance failure is often recognizable before it becomes a crisis. A consortium should monitor operational symptoms rather than assuming a signed charter guarantees cooperation.
| Failure Mode | Early Operational Symptom | Practical Recovery Action |
|---|---|---|
| Veto abuse | Routine schema changes wait months for approval | Limit vetoes to defined legal, security, and competition concerns |
| Member churn | Partners delay onboarding or refuse node obligations | Offer participant tiers while preserving clear validation rights |
| Dominant-member control | One organization owns most validators or chairs key committees | Cap related-party validator influence and use independent oversight |
| Data-quality disputes | Exception queues grow despite high transaction finality | Reconcile with ERP, WMS, scans, and trusted inspection sources |
| Upgrade paralysis | Smart contracts diverge or integrations remain on old versions | Publish version windows, migration tests, and deprecation dates |
A fair warning: no universal threshold defines “too many” members. A consortium with 15 highly aligned firms and a common data model can operate more smoothly than one with five organizations that disagree on identifiers, liability, and costs. The relevant threshold is governance capacity. If approvals routinely exceed the business cycle they support, the consortium is already too slow.
Interoperability Must Respect Trust Boundaries
Supply chain validation rarely begins on the blockchain. It begins in ERP purchase orders, WMS receipt events, transportation platforms, laboratory systems, IoT gateways, EDI messages, and external compliance portals. The ledger should not duplicate all of those systems. It should normalize the events that require shared validation.
A sound pattern separates four layers:
• Source layer: ERP, WMS, TMS, IoT devices, and laboratory systems generate operational events.
• Integration layer: APIs, EDI translators, message queues, and adapters validate format, identity, and business rules.
• Consortium layer: smart contracts apply shared acceptance rules, endorsements, finality, and event ordering.
• Evidence layer: off-chain repositories hold documents, sensor data, certificates, and confidential commercial records linked by hashes or references.
The point is not to force every partner into one ERP or one blockchain application. Each member can retain its operating stack while exchanging a shared canonical event. For instance, “custody transferred” must have the same meaning across systems even if one party uses SAP, another uses Oracle, and a carrier uses an industry platform.
Interoperability also changes liability. If an API submits an event automatically after a scanner read, the consortium needs to know whether responsibility lies with the scanner operator, device owner, integration provider, or business entity whose credential authorized the transaction. Smart contracts can enforce workflow conditions; they cannot resolve undefined accountability.
The enterprise blockchain architecture security and scalability discussion is relevant because integration endpoints, key management, and endorsement policies often create more exposure than the core ledger protocol.
A Practical Production Architecture
For multinational supply chains, a common production pattern is regional application and data services with a limited set of validator nodes distributed across independent member organizations. Validators should not all run in the same cloud account, availability zone, or outsourced operations provider. That would create a single operational failure domain despite nominal decentralization.
I would separate node classes deliberately:
• Validator nodes finalize transactions under the consortium consensus rules.
• Application nodes serve member workflows and should expose only authorized data views.
• Integration gateways connect ERP, WMS, EDI, IoT, and external attestation sources.
• Off-chain evidence stores retain sensitive documents under retention, residency, and access policies.
• Monitoring services track validator health, transaction backlog, endorsement failures, identity anomalies, and data-quality exceptions.
The Springer review of blockchain in supply chain management characterizes consortium designs as suitable for inter-organizational collaboration while also identifying persistent tension among scalability, decentralization, security, and technical complexity. That tension should shape architecture choices, not be treated as a flaw that a vendor can simply remove.
Key Takeaways
• Choose a consortium blockchain when independent organizations need shared validation and cannot reasonably assign ledger control to one party.
• Avoid it when a neutral database, signed APIs, and audit rights solve the actual trust problem at lower operating cost.
• Treat source data integrity as a first-class design problem. Immutable false data remains false.
• Use off-chain storage for sensitive records and place proofs, statuses, and minimal shared evidence on-chain.
• Select consensus based on the required fault model, deterministic finality, validator independence, and recovery process, not on throughput claims alone.
• Put governance into enforceable operating rules before production: membership, voting, change control, cost allocation, and disputes.
• Measure success through business outcomes such as reduced reconciliation, faster recalls, fewer disputes, and reliable partner onboarding.
The central trade-off is straightforward: consortium architecture can produce stronger shared assurance than a single-company system, but it replaces unilateral control with continuing coordination work. That work is the price of credible multi-party validation.
FAQ
What Is A Consortium Blockchain In Supply Chain Validation?
It is a permissioned ledger operated by several approved organizations. It records and validates shared supply chain events, such as custody changes, inspections, certifications, and transformations, using rules that no single member can alter alone.
When Should A Supply Chain Use A Consortium Chain Instead Of A Database?
Use it when multiple independent parties need a shared, tamper-evident evidence trail and would dispute one participant’s ownership of the database. Use a conventional database when one enterprise is clearly accountable and partners accept its audit controls.
Which Consensus Mechanism Works Best For Supply Chain Validation?
There is no universal winner. Proof of Authority can suit tightly governed networks that prioritize efficiency. BFT-style consensus may fit cases requiring stronger resilience to malicious or faulty validators. The choice depends on validator independence, outage tolerance, finality needs, and governance maturity.
How Do Competitors Protect Confidential Data On A Shared Ledger?
They minimize on-chain data, use permissioned access, and keep detailed documents in controlled off-chain storage. The chain records proofs and shared status, while commercial terms, personal data, and large files remain available only to authorized parties.
How Do You Prevent One Member From Dominating Governance?
Distribute validator ownership across genuinely independent entities, cap related-party voting influence, define narrow veto rights, publish transparent change procedures, and use independent review for high-impact membership or protocol decisions.
What Happens If A Validator Goes Offline Or Acts Maliciously?
The answer depends on quorum and consensus design. A properly sized validator set can continue finalizing transactions if enough honest nodes remain available. Recovery should include node isolation, key revocation, forensic review, replacement approval, and clear communication to members.
Why Do Consortium Blockchain Pilots Commonly Stall?
The usual causes are unresolved governance, weak source data, inconsistent identifiers, underestimated ERP and WMS integration work, unclear funding, and no measurable business case. The ledger is rarely the only blocker.
Sources
• NYU Stern — RISKS AND OPPORTUNITIES FOR SUPPLY CHAIN FINANCE USING BLOCKCHAIN https://www.stern.nyu.edu/sites/default/files/assets/documents/RisksandOpportunitiesforSCFusingBlockchain_V1.0SF.pdf
• Cardiff University — White Paper on Blockchain for Supply Chains https://orca.cardiff.ac.uk/id/eprint/122146/1/white%20paper%20on%20blockchain%20for%20supply%20chains.pdf
• Frontiers in Blockchain — Enterprise Blockchain Consortium Evaluation Paper https://www.frontiersin.org/journals/blockchain/articles/10.3389/fbloc.2022.935346/pdf
• Springer — Blockchain in supply chain management: a comprehensive review https://link.springer.com/article/10.1007/s11301-025-00546-0?error=cookies_not_supported&code=3b7eefdd-b60d-4f81-8956-4422d9a3aed3
• Chainlink — Understanding the Consortium Blockchain Architecture https://chain.link/article/consortium-blockchain
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.