Enterprise Blockchain Strategy Consulting for Complex Compliance
By Jeremy Ryan, Founder & CEO · September 2026
Enterprise blockchain strategy consulting for organizations with complex compliance requirements should begin with a hard question: does a shared ledger solve a real control problem that existing systems cannot solve more simply? I recommend treating blockchain as regulated infrastructure, not an innovation experiment. The strongest business cases involve multiple parties that need a common, tamper-evident record while retaining controlled access, clear accountability, and defensible evidence for auditors or examiners.
Table of Contents
- Establishing Whether Blockchain Is Justified
- Selecting Architecture Around Compliance Constraints
- Designing Evidence, Identity, And Risk Ownership
- Moving From Discovery To Controlled Production
- Key Takeaways
- Frequently Asked Questions
Establishing Whether Blockchain Is Justified
The practical purpose of enterprise blockchain strategy consulting is to determine whether decentralized ledger technology can improve a regulated business process without creating a larger privacy, operational, or governance burden. The deliverable should be a decision record, not merely a platform recommendation.
Start With The Shared-Control Problem
Blockchain is a reasonable candidate when three conditions exist at once:
• Multiple legally distinct organizations write or rely on the same business record.
• Reconciliation delays, disputes, duplicate submissions, or unverifiable document histories create material cost or compliance risk.
• Participants need controlled visibility into the same event history without surrendering all operational data to a single party.
Consider a trade-finance workflow involving a bank, exporter, carrier, insurer, and customs broker. Each party may maintain its own records of shipment status, document approval, and release conditions. A permissioned ledger can establish a shared chronology of approvals. It does not replace trade law, sanctions screening, document retention, or liability allocation. It gives those controls a consistent evidentiary spine.
A useful consulting engagement therefore tests the business process before discussing code. NMS Consulting’s enterprise blockchain approach describes a progression from fit assessment and use-case selection through architecture, consortium design, and phased adoption. That sequence matters because an unsuitable use case remains unsuitable even when the chosen ledger is technically sophisticated.
Know When A Conventional System Is Better
Not every audit problem needs a blockchain. I would avoid it when one trusted organization already has legal authority to operate the system of record, external parties do not need independent write rights, or the primary need is internal workflow automation. A database with strong logging, immutable storage, role-based access, and conventional integration may deliver the required control at lower cost.
Blockchain can also be a poor fit where records must be routinely altered or deleted, where transaction volume and latency requirements exceed the feasible design, or where consortium members have no incentive to operate shared infrastructure. An immutable event log is valuable only when the organization can explain why the event must be jointly witnessed.
Decision rule: Use blockchain to coordinate trust across organizations, not to make an ordinary internal database sound more advanced.
Map Requirements Before Choosing Technology
Regulatory discovery should translate obligations into system behaviors. Legal, compliance, privacy, information security, records management, and business owners need to agree on the questions before an architecture team proposes a network.
| Compliance Area | Discovery Question | Design Implication |
|---|---|---|
| Recordkeeping | Which events and documents must be retained, in what form, and for how long? | Preserve signed event records, document versions, timestamps, and retrieval evidence. |
| Privacy | Does the workflow involve personal data, health data, financial data, or confidential commercial information? | Minimize on-chain data and define off-chain storage, deletion, and access processes. |
| AML, KYC, And Sanctions | Which participant checks must occur before a transaction or transfer is accepted? | Integrate screening decisions, exception approvals, and review timestamps into workflow controls. |
| Sector Rules | Are there licensing, reporting, validation, or supervisory requirements? | Define accountable entities, approval gates, reporting extracts, and jurisdiction-specific controls. |
| Cross-Border Operations | Will records or participant data be accessed from multiple jurisdictions? | Determine data locations, controller and processor roles, transfer mechanisms, and local restrictions. |
Legal considerations for business blockchain deployments emphasizes defining participants, jurisdictions, potential licensing requirements, privacy engineering, liability, and legal documentation before implementation. That is the right order. Platform selection should follow the compliance map, not precede it.
Selecting Architecture Around Compliance Constraints
For compliance-heavy programs, architecture is a policy decision expressed in technology. Choices about permissions, validator roles, data location, and key custody determine what the organization can later prove.
Compare Network Models By Control Needs
A public blockchain offers broad transparency and independent validation, but it generally creates difficult confidentiality and operational-control questions for regulated business records. A private blockchain is operated by one organization and can simplify accountability, although external participants may see it as another vendor-controlled system. A consortium blockchain distributes governance among approved members and is often better suited to multi-party regulated workflows.
| Model | Best Fit | Primary Compliance Advantage | Main Trade-Off |
|---|---|---|---|
| Private Network | One organization controls the process and needs limited external access. | Centralized administration and clearer operational ownership. | Limited shared governance and weaker independence for counterparties. |
| Permissioned Consortium | Multiple regulated firms need a common record and shared decision rights. | Controlled participation, auditable governance, and selective data access. | Governance negotiations can be slower than technical delivery. |
| Hybrid Design | A process needs private records but selective public verification. | Can provide external proof without publishing underlying data. | Requires careful design to prevent metadata leakage or false assurance. |
A permissioned network should not mean broad internal access. It should mean that every participant, service account, validator, and integration endpoint has a defined identity, purpose, entitlement, and revocation process.
Keep Sensitive Data Off-Chain
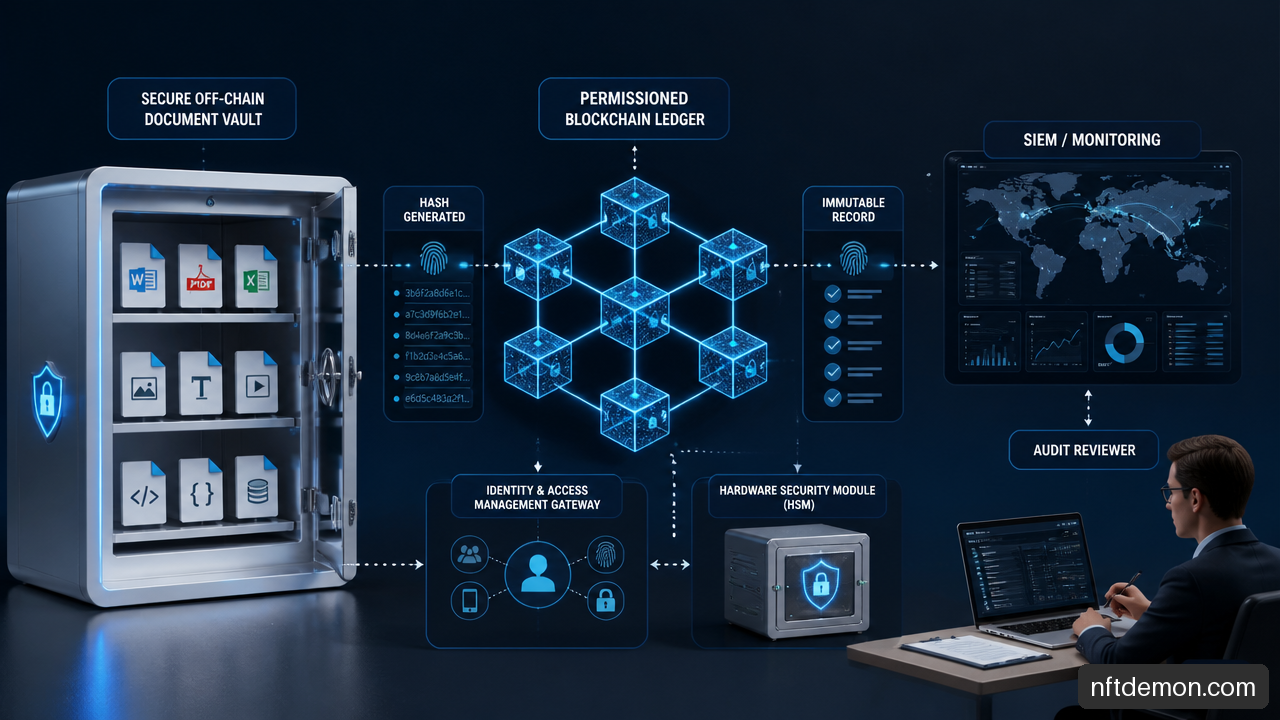
Immutability is not a license to store sensitive information permanently. The usual privacy-conscious pattern is to retain the sensitive document or data set in a controlled off-chain repository and record a cryptographic hash, identifier, timestamp, status, and authorized references on-chain. The hash lets a reviewer verify whether the retrieved document matches the version associated with a transaction without putting the document itself on the ledger.
Enterprise blockchain governance guidance supports mapping technical controls to legal and internal-audit expectations, using privacy-by-design, and keeping sensitive content off-chain with hashes or references where appropriate.
This pattern has limits. A hash can still be sensitive if it can be linked to a person or a narrowly identifiable event. Transaction timing, participant identifiers, and metadata can reveal business relationships. Privacy review must assess the entire information flow, not just the data field stored in a block.
Treat Smart Contracts As Controlled Business Logic
A smart contract can automate conditions such as approval thresholds, document completeness, payment release, or asset transfer. In a regulated setting, it should not become an undocumented substitute for a legal agreement or policy.
The stronger pattern is a legal wrapper: a natural-language agreement identifies the parties, governing law, rights and obligations, the authoritative version of the code, and how exceptions are handled. It should also state who can pause the contract, approve an emergency change, correct an erroneous state through a compensating transaction, and authorize an upgrade.
For example, a smart contract may prevent release of a shipment record until sanctions screening is marked complete. If the screening integration fails, the system needs an approved exception path. Otherwise, a technical outage becomes either an unauthorized bypass or an operational dead end.
Designing Evidence, Identity, And Risk Ownership
Auditability is not created by immutability alone. It is created when the organization can explain what happened, who did it, under which authority, with what source data, and how the evidence remained reliable over time.
Build An Evidence-Preservation Model
For every material transaction, define a minimum evidence package. The ledger event should be only one component.
- Business context: transaction identifier, process stage, involved entities, and applicable policy or contractual rule.
- Authorization evidence: authenticated identity, role, approval authority, consent or delegation record, and timestamp.
- Source evidence: document hashes, source-system references, data lineage, and relevant validation results.
- Control evidence: sanctions or KYC status where applicable, exception approvals, smart-contract version, and change-ticket reference.
- Operational evidence: node logs, integration logs, security alerts, recovery actions, and records of failed or rejected transactions.
The organization should test whether an internal auditor can reconstruct an event without relying on one employee’s memory. That means exporting ledger data in readable form, linking it to enterprise records systems, and retaining documentation that explains the schema and control model. A ledger that is technically immutable but operationally unreadable years later is not an audit-ready record.
Make Identity And Key Recovery Approval Gates
Identity and access management must operate at both the application and ledger layers. A user may be entitled to view a case in an enterprise application but not entitled to endorse a ledger transaction. Similarly, a system integration may submit updates but should not gain unrestricted access to historical data.
Key management is often the hidden approval blocker. Lost keys, compromised administrator credentials, or an untested recovery mechanism can prevent access to regulated records or permit unauthorized actions. I recommend defining these controls before pilot approval:
• Identity proofing and onboarding for organizations, users, service accounts, and validators.
• Role-based permissions tied to job functions and least-privilege rules.
• Hardware security modules or multi-party computation where risk warrants stronger key custody separation.
• Dual approval for privileged actions, including validator changes and smart-contract upgrades.
• Tested recovery for employee departure, lost credentials, suspected compromise, and organizational exit.
• Logging sent to enterprise SIEM tooling so ledger events can be correlated with identity and security events.
The test is straightforward: if a critical signer leaves unexpectedly, can the organization revoke access, restore authorized control, preserve evidence, and avoid halting the business process? If the answer is uncertain, production readiness is premature.
Assign Governance And Liability Explicitly
The most difficult part of a consortium is frequently governance, not distributed systems engineering. A regulated network needs a written operating model that covers membership, voting, audit rights, funding, technical standards, incident response, and exit.
| Decision Area | Accountable Owner | Required Control |
|---|---|---|
| Member Admission | Governance committee | Due diligence, legal approval, identity issuance, and onboarding evidence. |
| Network Rule Changes | Voting members and change authority | Voting threshold, impact assessment, test environment, and rollback plan. |
| Security Incidents | Named incident lead and member security teams | Notification timeline, evidence preservation, containment, and regulator escalation path. |
| Data Errors | Business process owner | Defined correction method, linked evidence, and no silent deletion of history. |
| Member Exit | Governance committee and departing member | Credential revocation, records access terms, key transition, and continuing retention obligations. |
Federated governance can work well because decision authority is shared among participants rather than concentrated in one operator. But “shared” cannot mean vague. Decision rights, emergency powers, voting thresholds, dispute resolution, and accountability need to be documented before the first production transaction.
Moving From Discovery To Controlled Production
A disciplined program moves through decision gates. The aim is not to produce a pilot quickly; it is to reach a defensible production decision quickly, including a decision not to proceed.
Require Concrete Discovery Deliverables
A consulting team should leave leadership with artifacts that can be reviewed by compliance, security, legal, architecture, and procurement. At minimum, I would expect:
• A use-case qualification memo that compares blockchain with conventional alternatives.
• A regulatory and policy control map connecting each requirement to a process, system, owner, and evidence item.
• A target architecture showing on-chain and off-chain data, integration points, identity boundaries, key custody, and monitoring.
• A consortium or operating-model charter covering decision rights, SLAs, liability, disputes, and member exit.
• A pilot test plan with measurable control objectives, exception scenarios, recovery tests, and production acceptance criteria.
HCLTech describes enterprise blockchain advisory as including assessments, workshops, roadmaps, governance, compliance, automated controls, and transparent audit trails in its blockchain services for enterprises. The useful standard is whether those activities produce decisions and evidence that internal control functions can actually approve.
Pilot The Failure Paths, Not Only The Happy Path
A compliance pilot should simulate events that create pressure: an incorrect source document, a sanctions-screening timeout, a revoked user credential, a validator outage, a disputed transaction, and a required record export. A demonstration that only shows successful transactions says little about operational resilience.
For a pilot to advance, teams should be able to answer four questions. Can they prevent an unauthorized action? Can they detect and investigate an anomalous action? Can they correct a business error without rewriting history? Can they recover from a key or infrastructure failure within an agreed service window?
Use A Compliance-Weighted Evaluation Scorecard
Technology features should be scored after control fit. A vendor with polished demonstrations but weak evidence handling can create more risk than a less flashy platform with mature integration and governance capabilities.
| Evaluation Criterion | Suggested Weight | What Good Looks Like |
|---|---|---|
| Regulatory And Control Mapping | 25% | Clear mapping from obligations to technical and operational controls. |
| Security, Identity, And Key Management | 20% | Documented custody model, recovery testing, logging, and privileged-access controls. |
| Data Privacy And Retention Design | 20% | Data minimization, off-chain architecture, jurisdiction analysis, and evidence retrieval. |
| Enterprise Integration | 15% | Practical connectivity to IAM, ERP, GRC, document systems, and SIEM tools. |
| Governance And Operating Model | 10% | Decision rights, liabilities, SLAs, change control, and exit mechanics. |
| Delivery And Support Readiness | 10% | Pilot methodology, production support model, testing, and knowledge transfer. |
Regulatory obligations change, so the operating model must accommodate controlled updates. EY’s blockchain consulting framing identifies compliance with changing regulations as a central concern. In practice, that means treating policy updates, contract changes, and code upgrades as governed events with documented impact assessments rather than ad hoc technical releases.
Key Takeaways
Make Compliance The Architecture Driver
The right enterprise blockchain design starts with recordkeeping, privacy, identity, jurisdiction, and risk ownership. A platform decision made before those requirements are mapped is usually a decision made with incomplete information.
Optimize For Defensible Operations
A viable production network is one that can demonstrate control under stress. It preserves evidence, limits access, protects and recovers keys, handles exceptions, and assigns accountability when members disagree or systems fail.
Frequently Asked Questions
Strategy And Use-Case Decisions
What Is Enterprise Blockchain Strategy Consulting For Regulated Organizations?
It is a structured assessment and design process that determines whether a permissioned, private, consortium, or hybrid ledger is appropriate for a regulated workflow. It should connect business objectives to compliance controls, architecture, governance, security, integrations, pilot criteria, and production operating responsibilities.
Which Processes Are The Best Candidates For Permissioned Blockchain?
Processes work best when several organizations need a shared, reliable event history and no single party is accepted as the unquestioned owner of the record. Examples can include document provenance, regulated supply-chain handoffs, multi-party approvals, and settlement workflows. Avoid blockchain when the process is internal to one organization or a conventional system of record can meet the need with less complexity.
How Do Private, Permissioned, And Consortium Blockchains Differ?
A private blockchain is usually controlled by one organization. A permissioned blockchain restricts participation to approved entities and can be private or consortium-operated. A consortium blockchain is a permissioned network jointly governed by multiple organizations. For regulated cross-company processes, consortium governance may provide better shared legitimacy, but it also requires more detailed agreements.
Controls And Production Readiness
How Should Sensitive Data Be Kept Off-Chain?
Store sensitive documents and detailed personal or commercial data in controlled repositories. Put only the minimum necessary reference, hash, status, and timestamp on-chain. Then assess whether metadata can still identify people, transactions, or commercial relationships. This design supports traceability while preserving options for retention changes, access restrictions, and data deletion in the off-chain system.
What Evidence Should Be Retained For An Audit Or Examination?
Retain the ledger event, associated source documents, document hashes, user and system identities, permission records, approval history, smart-contract version, exception records, security logs, integration logs, and change-control documentation. Evidence should be retrievable in human-readable form and connected to the applicable business rule or policy.
How Do Smart Contracts Fit With Legal Agreements?
Smart contracts should execute defined operational rules, while natural-language agreements establish legal intent, governing law, liability, dispute handling, and remediation. The agreement should identify the applicable code version and specify how bugs, upgrades, emergency pauses, and incorrect records will be handled.
What Is The Biggest Compliance Risk In A Consortium Network?
Unclear accountability is often the central risk. A network can have strong cryptography and still fail operationally if no party owns member admission, data-error correction, incident response, regulatory reporting, or the cost of maintaining the platform. Governance must make those decisions explicit before production.
Sources / References
- Blockchain Council — Enterprise Blockchain Governance for Strategy Professionals: https://www.blockchain-council.org/blockchain/enterprise-blockchain-governance-policies-risk-management-compliance/
- Blockchain Council — Legal Considerations for Business Blockchain Deployments: https://www.blockchain-council.org/blockchain/regulatory-legal-considerations-business-blockchain-deployments/
- NMS Consulting — Blockchain for Enterprise: How Consultants Drive Adoption ...: https://nmsconsulting.com/blockchain-for-enterprise/
- HCLTech — Blockchain Services & Solutions for Enterprises: https://www.hcltech.com/en-us/blockchain-services
- EY — Blockchain consulting services: https://www.ey.com/en_pl/services/consulting/blockchain-consulting-services
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.