What Enterprise Blockchain Consulting Includes for Fortune 500 Teams
By Jeremy Ryan, Founder & CEO · September 2026
What does enterprise blockchain consulting include for Fortune 500 technology teams? At its best, it is not a presentation about distributed ledger technology. It is a structured decision and delivery process that determines whether blockchain solves a real coordination problem, how it fits existing systems, who governs it, and what must be true before it reaches production.
For large technology organizations, the blockchain protocol is rarely the hardest decision. The harder questions involve data ownership, ERP integration, identity and access management, key custody, legal obligations, operating costs, node responsibilities, and measurable business outcomes. We recommend treating consulting as a way to reduce those uncertainties before they become expensive technical debt.
The Scope Of Enterprise Blockchain Consulting
Enterprise blockchain consulting helps a Fortune 500 team make, build, and operate a defensible technology decision. The work typically spans executive advisory, technical architecture, implementation planning, controls, and post-launch governance. A credible engagement separates these workstreams rather than treating them as one generic “blockchain solution.”
Executive Advisory Deliverables
Executive advisory work translates a business problem into an investment decision. It is owned jointly by business leadership, enterprise architecture, security, finance, legal, procurement, and the team accountable for the affected process.
Typical advisory deliverables include:
• A problem statement that identifies the shared process, participants, trust gaps, and current reconciliation burden.
• A use-case scorecard comparing blockchain with a conventional database, workflow platform, API hub, or managed data exchange.
• A decision memo that recommends proceeding, pausing, narrowing the scope, or choosing a non-blockchain alternative.
• A business case with baseline metrics, expected operating costs, dependency risks, and pilot exit criteria.
• A governance charter covering decision rights, participation rules, change approval, dispute handling, and funding responsibility.
• A vendor and platform evaluation model that focuses on fit, operational maturity, interoperability, and security requirements rather than brand recognition.
The distinction matters. A proof of concept can demonstrate that nodes exchange transactions. It does not prove that the organization can reconcile ledger events into finance systems, satisfy retention rules, or sustain the network after consultants leave.
Engineering Deliverables
Engineering deliverables turn an approved decision into a system that can be tested and operated. They are more concrete than a roadmap and should be usable by internal engineering, platform, and security teams.
A delivery package commonly includes a target reference architecture, integration specifications, data model, smart contract design, environment plan, infrastructure-as-code approach, test strategy, and production-readiness checklist. The architecture work should account for functions, roles, interfaces, and governance across the network lifecycle, which is central to the scope described by ISO/IEC 23257 reference architecture guidance.
The practical question is not “Can we put this record on a blockchain?” It is “Can every participant rely on the record, integrate it into their workflow, and govern change without creating a parallel manual process?”
What Consulting Should Exclude
A trustworthy consulting scope also states what it will not do. It should not assume that every multi-party workflow needs decentralized consensus. It should not promise production benefits from a pilot that has not been integrated with source systems. And it should not blur legal advice, audit attestation, or managed node operations into vague language.
Fair warning: if one company controls all data, all workflow decisions, and all participants, a conventional database with strong access controls may be simpler and less costly. Blockchain becomes more plausible when multiple parties need a shared, tamper-evident record but do not want one participant to own the system of record unilaterally.
Strategy, Use-Case Discovery, And Business-Case Gates
Start With The Coordination Problem
The strongest consulting engagements begin with a narrowly defined operational problem. Supply chain management, trade documentation, warranty history, identity credentials, rights management, settlement workflows, and intercompany reconciliation can be plausible candidates. The use case still needs a fit test.
We recommend asking five questions before selecting a protocol:
-
Do multiple organizations need to write to or verify the same record?
-
Is there a material trust, reconciliation, audit, or dispute-resolution problem today?
-
Would a shared ledger reduce manual exceptions or duplicated recordkeeping?
-
Can participants agree on data standards, validation rules, and governance?
-
Is there a measurable benefit that exceeds the added complexity of nodes, cryptographic keys, and controls?
Consider a manufacturer that disputes component provenance with suppliers and repair partners. A blockchain pilot may be worthwhile if every party needs to validate custody events and no party is accepted as the sole authority. But if the real issue is incomplete scanning at warehouses, the better investment may be process instrumentation and master-data cleanup. A ledger cannot repair inaccurate source events.
Define Pilot Exit Criteria Before Building
A pilot without exit criteria often becomes a technology demonstration with no owner for the next decision. Consulting should establish measurable gates before engineering starts.
Decision Area | Example Baseline | Pilot Exit Criterion |
|---|---|---|
Reconciliation | Manual reconciliation requires several business days | Reduce the defined reconciliation cycle by an agreed percentage |
Traceability | Records require multiple systems and email requests | Retrieve verified chain-of-custody evidence within a defined service window |
Exceptions | Teams manually investigate frequent data mismatches | Lower exception rates for the scoped workflow |
Performance | Existing workflow has known volume peaks | Meet transaction latency and throughput targets under load testing |
Auditability | Evidence collection is labor intensive | Produce role-based audit records for each critical state change |
The point is not to manufacture an attractive return-on-investment figure. It is to establish whether the ledger changes an operational metric that leadership already cares about. If no baseline exists, consulting should first measure the current state. That step is mundane, but it prevents a team from claiming value without a comparison point.
Strategy Consulting Versus Implementation Consulting
Strategy consulting answers whether the organization should pursue the use case and under what constraints. Implementation consulting answers how to build, integrate, secure, test, and operate the approved solution. Fortune 500 teams often need both, but they should be contracted as separate decision stages.
Workstream | Primary Question | Typical Output | When To Stop |
|---|---|---|---|
Strategy | Is blockchain justified for this business problem? | Decision memo, business case, roadmap, governance concept | Stop if a conventional solution meets requirements better |
Architecture | What network, trust model, and integration pattern fit? | Reference architecture, data model, control matrix | Stop if required controls cannot be designed practically |
Pilot Delivery | Can the scoped process work under realistic conditions? | Tested pilot, integrations, performance evidence | Stop if pilot metrics fail or adoption dependencies remain unresolved |
Production Support | Can internal teams run it safely and sustainably? | Runbooks, operating model, incident procedures | Reassess when ownership, funding, or governance is unclear |
For terminology and documentation, teams benefit from a common vocabulary for distributed ledgers, consensus mechanisms, and smart contracts. ISO/IEC 22739 blockchain vocabulary supports that standardization work before architecture discussions become muddled by inconsistent definitions.
Architecture And Enterprise Integration
Choosing Permissioned, Public, Or Hybrid Networks
Network selection should follow trust boundaries and business requirements, not protocol fashion. Permissioned blockchain networks generally fit controlled business consortia where participants require known identities, contractual accountability, selective data access, and predictable governance. Public networks may be appropriate when broad verification, open ecosystem participation, or externally transferable digital assets are essential.
A hybrid blockchain model can be useful when an enterprise needs private operational records but wants selected proofs, attestations, or asset references verifiable on a public network. This is not automatically more secure. It introduces additional bridging, privacy, monitoring, and incident-response considerations.
Network Model | Best Fit | Core Trade-Off |
|---|---|---|
Permissioned | Known business partners, regulated workflows, controlled access | Requires governance agreements and participant onboarding |
Public | Open ecosystems, public verification, certain digital asset models | Less direct control over network conditions and data exposure risks |
Hybrid | Selective public verification with private business data | More integration complexity and clearer boundary design required |
NIST frames blockchain systems around cryptographically linked ledger records, which makes consensus, identity, and governance central design concerns; this framing is also summarized by enterprise blockchain advisory material from Dragonfly Advisers.
Integration Is Usually The Real Program
Most enterprise blockchain initiatives do not fail because a ledger cannot record a transaction. They stall because the ledger is isolated from the systems that make the transaction operational.
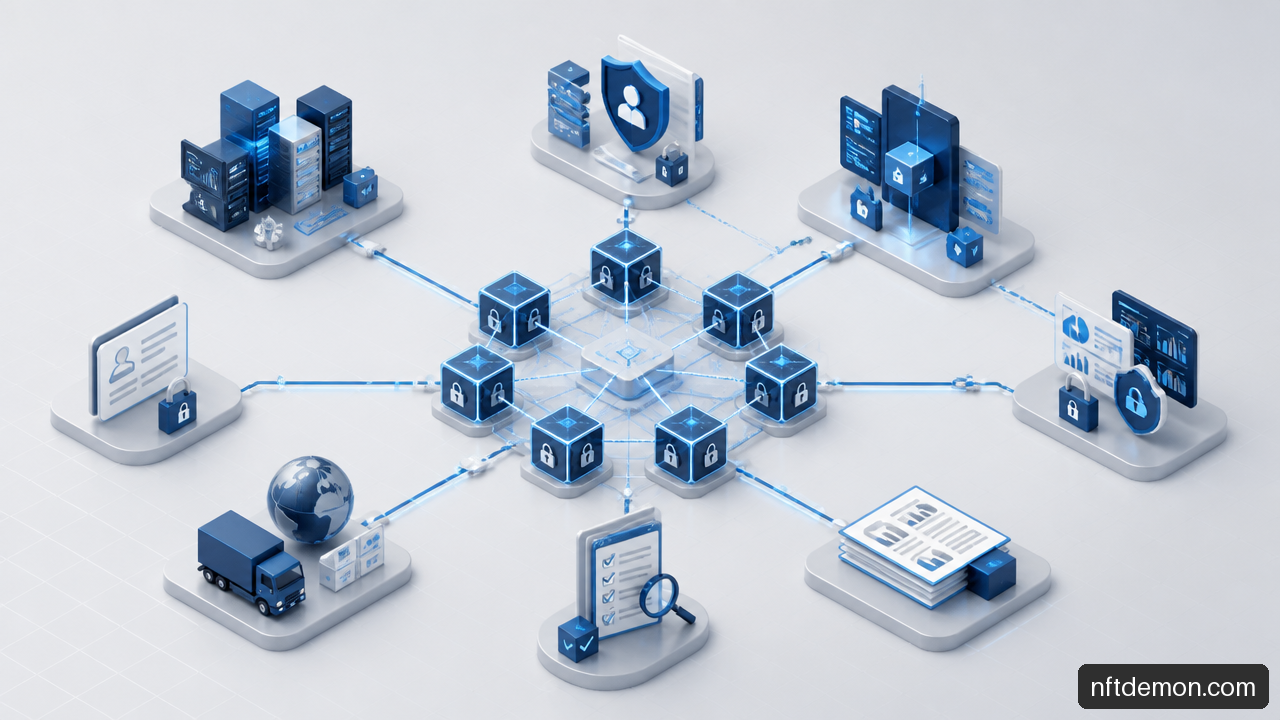
A consultant should map how blockchain events connect to:
• ERP systems for orders, invoices, payments, inventory, and financial postings.
• Customer, supplier, and product master-data systems.
• Identity and access management platforms for authentication, authorization, and role changes.
• API gateways, event streams, data warehouses, and reporting tools.
• Case management, workflow, and document repositories.
• Security information and event management platforms for monitoring and audit correlation.
For example, a supplier may record a custody transfer on a ledger, but the manufacturer’s ERP system still needs a verified event before it releases payment or updates inventory. Consulting should define the API contract, failure behavior, retry logic, data ownership, and reconciliation process. If the blockchain is temporarily unavailable, does the ERP hold the transaction, create a pending state, or use a controlled fallback? That decision belongs in architecture, not a post-pilot patch.
Smart Contracts And Data Boundaries
Smart contracts should contain rules that benefit from shared execution and independent verification. They should not become a dumping ground for every enterprise rule. Complex pricing logic, regulated personal data, or rapidly changing business policies may be better managed off-chain, with on-chain references or approved state transitions.
The consulting scope should specify contract ownership, upgrade authority, testing requirements, external dependency risks, and audit intake criteria. Unclear ownership between engineering, security, and legal can delay review late in the project. A defined intake package helps: intended business effect, privileged functions, role model, assets affected, upgrade pattern, data classification, and test evidence.
Security, Compliance, And Operating Model Design
Security Review Is A Defined Workstream
“Security review” is too vague for an enterprise blockchain program. A useful package includes threat modeling, key-management design, node hardening, identity assurance, smart contract review, logging requirements, configuration control, resilience testing, and incident response.
Relevant baseline control families include access control, audit logging, configuration management, and incident response, as outlined in NIST SP 800-53 security and privacy controls. The ledger does not replace these controls. It adds cryptographic assets, distributed infrastructure, and multi-party operational dependencies that must be integrated into them.
A practical security checklist should address:
• Who generates, stores, rotates, recovers, and revokes cryptographic keys.
• Whether hardware security modules, multi-party approval, or delegated custody are needed for privileged actions.
• Which identities can submit transactions, operate nodes, view data, approve upgrades, and access audit logs.
• How node environments are patched, monitored, backed up, and isolated from unauthorized configuration changes.
• How smart contract vulnerabilities, compromised credentials, malicious participants, and data-feed failures are handled.
• How load testing and disaster recovery validate behavior under high volume, network partition, or participant outage.
U.S. Compliance And Data Governance
Compliance requirements depend on sector, data type, and business model. Consulting should map enterprise obligations to actual ledger behavior rather than assuming immutability resolves audit needs.
For U.S. teams, the assessment may cover privacy obligations, records retention, legal holds, data residency, sanctions screening, procurement controls, audit evidence, and sector-specific rules. Tokenization deserves separate legal and compliance review because digital asset programs may raise securities-law questions. The U.S. Securities and Exchange Commission digital asset guidance resources are relevant when tokens represent investment interests, rights, or transferable value.
One recurring design choice is whether to place data on-chain at all. Personal information, confidential commercial terms, and mutable records are often poor candidates for direct storage on an immutable ledger. A more controlled pattern may store sensitive data in an enterprise repository and record a hash, timestamp, permissioned reference, or status proof on-chain. That approach still requires careful analysis: a hash can remain sensitive if it can be connected to identifiable information or predictable source data.
Governance After Go-Live
A blockchain program is not finished at deployment. The operating model must identify who owns node operations, approves participant onboarding, authorizes smart contract upgrades, pays infrastructure costs, handles disputes, and leads incidents.
A production governance package should include a network council charter, service-level expectations, change-control process, participant agreement template, incident playbook, upgrade policy, and decommissioning plan. Without these artifacts, a pilot can work technically while remaining unfit for production.
This is especially important for consortium models. A single enterprise may operate a permissioned network initially, but the value proposition can change when suppliers, distributors, insurers, or regulators join. Consulting should anticipate that evolution and define which rules can change by majority vote, unanimous consent, or operator authority.
Key Takeaways
The Decision-Maker View
• Enterprise blockchain consulting should begin with a business and trust problem, not a protocol choice.
• Executive advisory deliverables should be separate from engineering deliverables so leadership can make informed go, pause, or stop decisions.
• Integration with ERP, IAM, APIs, data pipelines, and reporting systems often determines whether a pilot can scale.
• Security requires a concrete control package covering identities, keys, nodes, smart contracts, monitoring, recovery, and incident response.
• A permissioned, public, or hybrid architecture should be chosen based on participants, control requirements, data boundaries, and governance needs.
• Production readiness depends on operating-model ownership, not just successful transaction demos.
Sources And References
• ISO - ISO/IEC 23257:2022 Blockchain and distributed ledger technologies — Reference architecture: https://www.iso.org/standard/75025.html
• ISO - ISO/IEC 22739:2020 Blockchain and distributed ledger technologies — Vocabulary: https://www.iso.org/standard/73771.html
• NIST - Security and Privacy Controls for Information Systems and Organizations: https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final
• U.S. Securities and Exchange Commission - Investor Bulletin / digital asset guidance landing pages: https://www.sec.gov/
• dragonflyadvisers.com: https://www.dragonflyadvisers.com/
Frequently Asked Questions
What Does Enterprise Blockchain Consulting Include For Fortune 500 Technology Teams?
It commonly includes use-case discovery, feasibility assessment, strategy, network selection, architecture, enterprise integration, smart contract design, security review, compliance mapping, pilot support, governance design, and post-launch operating procedures. The exact scope should be tied to a defined business process and measurable outcomes.
What Is The Difference Between Blockchain Strategy Consulting And Implementation Consulting?
Strategy consulting evaluates whether blockchain is appropriate and defines the business case, governance approach, and roadmap. Implementation consulting designs and builds the system, integrates it with enterprise platforms, tests controls, and prepares internal teams for production operations.
Which Use Cases Are Realistic For A Fortune 500 Technology Team?
Realistic use cases usually involve multiple parties that need a shared, verifiable record and face costly reconciliation or audit friction. Examples can include supply chain provenance, trade documents, shared warranty records, intercompany workflows, and controlled digital credential systems. A use case is weak when one organization can solve the issue with its existing database and workflow tooling.
How Do Consultants Choose Between Permissioned And Public Blockchain Networks?
The decision depends on participant identity, data confidentiality, governance control, regulatory expectations, transaction economics, and whether public verification is essential. Permissioned networks tend to fit known business participants. Public networks can fit open ecosystem requirements. Hybrid models can support selective verification but add design and operational complexity.
What Systems Usually Need Integration With An Enterprise Blockchain Pilot?
Most pilots need connections to ERP platforms, IAM systems, API gateways, master-data services, data warehouses, reporting tools, workflow systems, and security monitoring platforms. The consulting team should define both the normal transaction path and what happens when source systems, APIs, or ledger nodes are unavailable.
How Do Teams Measure ROI For A Blockchain Initiative?
Measure the operational problem the initiative is supposed to improve. Useful metrics include reconciliation time, exception rates, audit-evidence collection time, dispute-resolution duration, traceability coverage, transaction latency, and manual processing effort. Compare pilot results with a documented baseline rather than relying on broad claims about innovation.
When Is Blockchain Not The Right Solution?
Blockchain is usually not the right choice when a single trusted party controls the process, participants do not need shared write access, data is highly sensitive and difficult to partition, or a conventional database can meet audit and workflow requirements at lower complexity. Stopping early can be the most valuable consulting outcome.
What Should Post-Launch Blockchain Support Include?
Post-launch support should include node operations, monitoring, patching, participant onboarding, key-management procedures, change control, smart contract upgrade governance, incident response, performance review, and periodic reassessment of the business case. A production system needs accountable owners for each of those functions.
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.