What Technical Evidence Should a Blockchain PoC Deliver?
By Jeremy Ryan, Founder & CEO · September 2026
A blockchain proof of concept should not end with a polished dashboard, a few successful transactions, and a claim that the technology works. It should produce a reviewable body of technical evidence that shows whether the proposed system can execute the intended workflow correctly, safely, repeatedly, and in connection with the systems that matter. When decision makers ask what technical evidence should a blockchain proof of concept deliver, the practical answer is: enough evidence to make a defensible proceed, revise, or stop decision.
A credible blockchain PoC proves more than ledger activity. It proves that specified participants can submit valid transactions, that the network reaches the correct ledger state, that controls work under failure conditions, and that the result can be traced into operational systems.
The Minimum Evidence Package
Demonstrate The Complete Business Transaction
The first deliverable should be an end to end transaction record, not a conceptual architecture diagram. A reviewer should be able to see what initiated the transaction, which identity submitted it, what rules were evaluated, which nodes validated it, how consensus was reached, and what ledger state changed afterward.
For example, a supply chain PoC might test a custody transfer of a serialized product. The evidence should show the original asset record, the authorized sender, the authorized receiver, the transaction payload, the smart contract result, the resulting ownership state, and the transaction receipt. If the stated value is traceability, the reviewer should be able to reconstruct the asset history without relying on a presenter’s explanation.
The Federal Reserve Bank of Boston’s Ethereum PoC materials illustrate this standard of proof: a PoC can show balances, wallet creation, transfers, transaction validation, consensus, and resulting smart contract ledger entries in one end to end flow. The Boston Fed’s example of blockchain transaction evidence is useful because it connects visible user actions to verifiable state changes.
A minimum transaction evidence set normally includes:
• A unique transaction identifier and submission timestamp
• The initiating identity, role, and authorization result
• Input data or a hash of input data where the underlying content is sensitive
• Smart contract version and execution result, if automation is in scope
• Validation and consensus status across the participating nodes
• Before and after ledger state, such as ownership, balance, status, or entitlement
• A transaction receipt, event log, and error message when the transaction fails
• Evidence of any downstream record created in an ERP, reporting, custody, or accounting system
This is not paperwork for its own sake. It allows another technical reviewer to replay the logic and verify whether the application did what the PoC claims.
Separate Functional Proof From Operational Proof
A common PoC mistake is treating a successful transaction as complete technical validation. It is not. A functional proof answers whether the workflow behaves correctly. A nonfunctional proof answers whether it behaves adequately under the conditions expected after the demo.
| Evidence Category | Question It Answers | Example Artifact |
|---|---|---|
| Functional evidence | Did the defined business rule execute correctly? | Smart contract test results and state transition records |
| Performance evidence | Did it complete within an acceptable time and volume? | Latency distribution, throughput results, queue depth |
| Security evidence | Did the system reject unauthorized or altered activity? | Permission denial logs, access tests, vulnerability findings |
| Resilience evidence | Did the network preserve correct behavior during disruption? | Node outage test, recovery log, reconciliation report |
| Integration evidence | Did external systems receive and reconcile the result? | API logs, event messages, matched accounting records |
| Governance evidence | Can operators control participation and policy changes? | Role matrix, onboarding record, approval workflow |
The distinction matters because a PoC may prove that a smart contract can transfer an asset once, while failing to show whether the system can process many transfers, deny an unauthorized request, recover from a node outage, or reconcile an event into the system of record.
Produce Reproducible Audit Evidence
I would treat reproducibility as a hard requirement. A technically credible PoC allows an independent reviewer to take a sample transaction and confirm the same facts: the request, the relevant rules, the state transition, the network confirmation, and the resulting external record.
That evidence should be retained in a defined package rather than scattered across a user interface, a node console, and developer notes. Include transaction receipts, event logs, node logs, configuration versions, smart contract addresses or identifiers, test data sets, and a short procedure for replaying the test. If a test cannot be repeated because a configuration changed without record, the PoC has limited value as a decision artifact.
Audit reconstruction is especially important for traceability claims. The implementation review published by PMC identifies provenance, timestamping, records of who acted and when, and reconstruction capability as useful evidence for moving beyond early stage experiments. PMC’s analysis of provenance and audit reconstruction evidence supports evaluating whether the PoC creates a usable history, rather than simply accepting data entry as proof of value.
Set Acceptance Criteria Before Testing
Convert Objectives Into Pass Or Fail Thresholds
A PoC should begin with measurable technical acceptance criteria. “Validate blockchain feasibility” is too vague to guide a build or an investment decision. Define the expected behavior, the measurement method, the threshold, and the owner who accepts the result.
The actual thresholds depend on the workflow. There is no universal transaction per second requirement because a batch settlement application, a certificate registry, and a real time entitlement system have different tolerances. Still, the criteria must be explicit before results are available. Otherwise, teams can redefine success after the demonstration.
| Test Area | Example Acceptance Criterion | Decision Meaning |
|---|---|---|
| State integrity | 100% of valid test transactions produce the expected ledger state | Confirms the business rule is correctly represented |
| Authorization | 100% of unauthorized actions are denied and logged | Confirms permissioning is enforced |
| Finality time | 95% of transactions reach final status within the agreed service target | Indicates whether the workflow can meet operating needs |
| Reconciliation | 100% of selected on chain events match downstream records | Confirms external system alignment |
| Resilience | Network retains correct state after a planned node loss | Tests whether the architecture has meaningful fault tolerance |
| Privacy | No direct personal data is written on chain in defined scenarios | Tests data minimization design |
Fair warning: criteria should not be designed to make the PoC easy to pass. If the production use case requires ten participating organizations and the PoC uses only one node with one administrator, the result may show application logic but not multi party network behavior.
Define The Test Boundary Honestly
A small scope is appropriate, but it must still represent the hardest assumptions that could invalidate the project. Use mock data when production records are unavailable or too sensitive. That is often the safer choice during early technical testing. The key is to preserve realistic data shapes, authorization patterns, exception conditions, and integration events.
Consider an asset tokenization PoC. Using three mock assets is enough to test issuance and transfer logic. It is not enough to substantiate claims about bulk issuance, fractional ownership calculations, reporting, identity verification, custody controls, or legal transfer restrictions. The evidence package should state what was tested and, equally important, what was not tested.
A blockchain PoC is generally intended to assess technical feasibility, functional performance, and business value, rather than serving as a production deployment. CEUR WS framing of blockchain PoCs as socio technical evaluation is a useful reminder that a narrow technical success does not automatically establish a case for full implementation.
Make The Result Decision Ready
The final PoC report should contain more than a list of completed tasks. I recommend a short decision memo that maps every acceptance criterion to one of three outcomes:
-
Passed: The recorded evidence met the threshold with no material qualification.
-
Conditionally passed: The core mechanism worked, but a known limitation requires redesign, further testing, or operational control.
-
Failed or unproven: The test did not meet the threshold, was not executed, or generated insufficient evidence to support a decision.
For each conditional pass or failure, identify the recovery path. A slow transaction finality result may call for a revised consensus configuration, a simpler data model, or asynchronous workflow design. A failed reconciliation result may indicate mismatched identifiers or event schemas rather than a blockchain defect. The memo should make those distinctions visible.
Prove Functional And Nonfunctional Behavior
Test Consensus And Ledger State Together
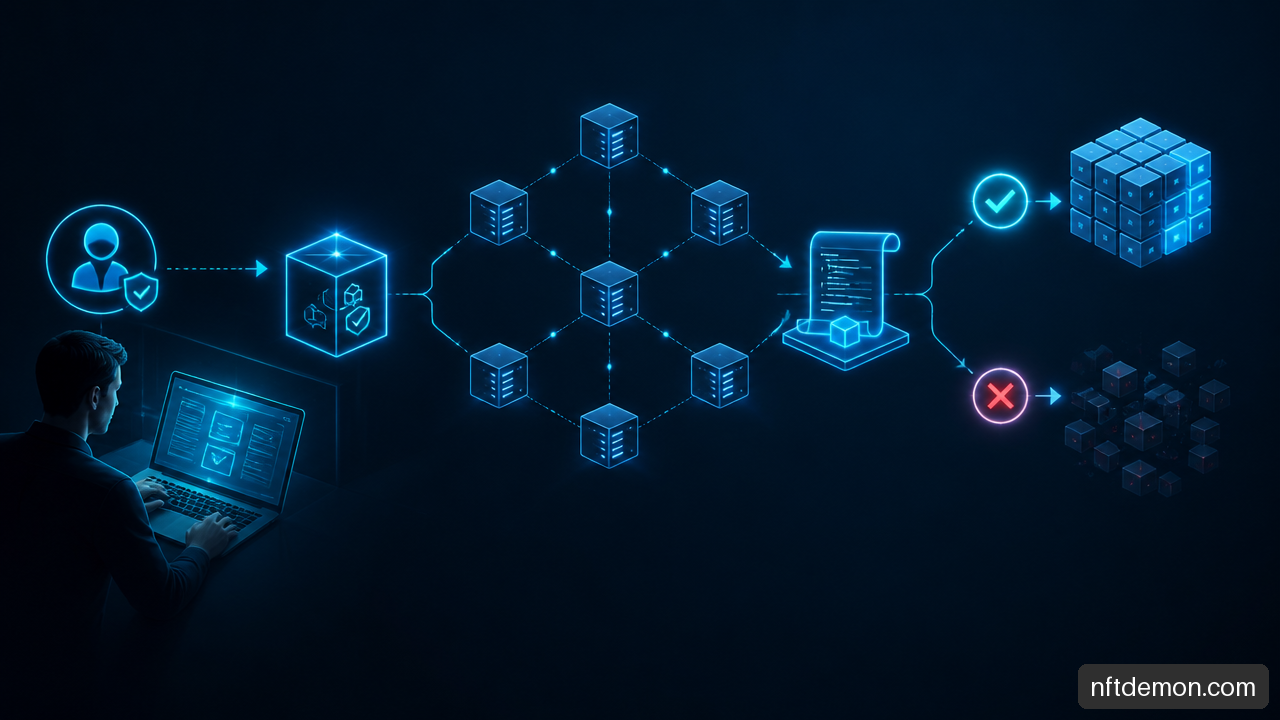
Consensus evidence should show more than nodes communicating with one another. It should demonstrate that authorized nodes agree on the same valid ledger state after a sequence of transactions, including competing or invalid requests.
Under the hood, a transaction is proposed, authenticated, checked against applicable rules, ordered or validated under the network’s consensus mechanism, committed to the ledger, and exposed through a receipt or event. The PoC should capture evidence at each stage that matters to the use case.
A practical consensus test can include:
• Submitting a valid transaction from an authorized participant
• Attempting a duplicate submission or conflicting state update
• Submitting an invalid signature, malformed payload, or expired authorization
• Comparing ledger state across participating nodes after each test
• Removing one noncritical node in a controlled test and verifying recovery behavior
• Confirming that rejected transactions do not create unauthorized state changes
The most meaningful result is not merely “consensus succeeded.” It is “consensus succeeded while every participating node retained the same correct state, and invalid actions were rejected without corrupting that state.”
Validate Smart Contracts Like Business Critical Code
Where smart contracts automate business rules, the PoC should show the contract is correct, constrained, and observable. A contract that can issue a token, register a record, or release a payment condition should be tested for both authorized paths and prohibited paths.
At minimum, retain the contract source version, deployment record, test cases, execution receipts, emitted events, administrator privileges, and any upgrade mechanism. If the contract can be upgraded, document who can authorize the change and what happens to previously issued assets or records.
A useful test set includes boundary values and sequence errors. For instance, a certificate cannot be revoked twice, an asset cannot be transferred by a former owner, and a payment cannot be released after the related entitlement has expired. These are ordinary workflow conditions, but they often reveal whether a contract models the real process or only a happy path.
Measure Performance Without Pretending It Is Production Scale
Performance evidence should report the test environment, not just a favorable number. State the number of nodes, their configuration, transaction mix, payload size, network conditions, test duration, and whether the workload was generated sequentially or concurrently.
Report distributions where possible. An average confirmation time can hide a small number of transactions that take far too long. Showing median, 95th percentile, maximum latency, error rate, and successful completed transactions is usually more useful than a single average.
Avoid translating a short benchmark directly into a production capacity promise. A four node PoC with synthetic records may establish that the architecture is viable. It does not prove performance across geographically distributed organizations, production identity infrastructure, real monitoring, or a larger data volume. The honest outcome may be: technically feasible, but scale assumptions remain unproven.
Test Integration, Privacy, And Governance
Show The Connection To Systems Of Record
Blockchain activity rarely stands alone in enterprise operations. A PoC should prove its ability to exchange information with identity services, ERP platforms, CRM applications, reporting tools, custody systems, document stores, or other operational platforms relevant to the use case.
The evidence should trace a transaction across the boundary. For example, an approved blockchain transfer may generate an event consumed by an accounting service, which creates a corresponding general ledger entry. The PoC should retain the blockchain transaction identifier, the integration message identifier, the receiving system response, and the reconciliation result. That allows reviewers to prove that one business event did not become two inconsistent records.
Choose synchronous integration only when the downstream system needs an immediate answer to continue the workflow. Event driven integration may be more appropriate when ledger finality can occur independently and downstream systems can process a durable event later. The PoC should test the selected pattern’s failure handling, including duplicate messages, delayed delivery, and a receiving system outage.
Evidence Privacy By Design, Not By Assertion
Immutability creates a particular privacy challenge: sensitive or personal data should not be written on chain merely because it is technically possible. A stronger PoC demonstrates data minimization through its data model.
A typical pattern stores sensitive content off chain in a controlled repository while placing a cryptographic hash, reference, or proof on the ledger. The evidence should demonstrate that a reviewer can verify integrity by recalculating the hash, while the underlying sensitive record can be corrected, restricted, or deleted in the off chain system when legally required.
The Spanish Data Protection Agency notes that blockchain compliance analysis must consider how affected records are identified across nodes, including transaction records, smart contract storage, and receipts or logs, as well as the consensus and governance strategy used to manage those concerns. AEPD guidance on locating affected blockchain records across nodes highlights why checking only the visible application database is insufficient.
For GDPR oriented use cases, the PoC should also document how smart contract receipts and logs are handled when erasure questions arise. AEPD’s technical annex on erasure related receipts and logs supports testing this issue before sensitive records enter a broader network.
Prove Operator Control And Failure Handling
Permissioned networks require governance evidence, not just a diagram labeled “admin.” Show who can join a node, issue an identity, submit a transaction type, deploy or upgrade a smart contract, change policy, and remove access. Then test at least one approval and one denial.
Failure evidence deserves equal attention. A production decision should not rest entirely on successful transactions. Test what happens when a node goes offline, a signer loses authorization, an API sends the same message twice, a smart contract rejects an invalid state transition, or an integration endpoint is unavailable.
For each case, capture the expected behavior, actual behavior, logs, alerting, and recovery action. There is no single mandatory failure test list for every PoC. A certificate registry may prioritize unauthorized revocation attempts; a multi party settlement workflow may prioritize inconsistent instructions and participant outages. The test design should follow the consequence of being wrong.
Key Takeaways
• A blockchain PoC should produce a reproducible evidence package, not just a working demonstration.
• Functional evidence proves correct workflow execution; nonfunctional evidence proves performance, security, resilience, and operability.
• Acceptance criteria must be measurable and defined before testing so stakeholders can distinguish passing results from favorable interpretation.
• Transaction receipts, event logs, timestamps, state comparisons, and configuration records make independent review possible.
• Integration evidence should connect on chain events to real systems of record and demonstrate reconciliation.
• Privacy evidence should show data minimization, off chain storage design, integrity verification, and treatment of logs and receipts.
• Permissioning, operator authority, invalid transactions, and node failures should be tested rather than assumed.
• A PoC is ready to advance when it provides enough measured evidence to support a clear proceed, revise, or stop decision.
FAQ
What Should Be Included In A Blockchain PoC Report?
Include the use case, scope boundaries, architecture, participant roles, test data approach, acceptance criteria, transaction evidence, smart contract evidence, performance results, security and failure tests, integration results, privacy design, governance controls, limitations, and a decision memo. The report should link each conclusion to a test artifact.
How Do You Prove A Blockchain PoC Actually Works?
Prove it with repeatable end to end tests. A reviewer should be able to submit or replay a representative transaction, inspect its authorization and validation result, verify the ledger state across nodes, inspect its receipt or log, and reconcile the outcome with any connected business system.
What Metrics Matter Most In A Blockchain PoC?
The most relevant metrics depend on the workflow, but commonly include transaction success rate, finality time, throughput, error rate, authorization denial rate, node state consistency, recovery time, reconciliation accuracy, and data exposure findings. Metrics should be tied to a predefined business or technical threshold.
How Do You Test Consensus In A Blockchain PoC?
Submit valid, duplicate, conflicting, malformed, and unauthorized transactions to the participating network. Compare the resulting ledger state across nodes, verify that valid transactions finalize correctly, confirm invalid transactions are rejected, and test recovery after a controlled node interruption where the chosen architecture is intended to tolerate one.
What Evidence Should A Blockchain PoC Provide For Security?
It should show identity authentication, permission enforcement, key handling assumptions, privileged role controls, smart contract authorization tests, tamper or invalid transaction handling, logging, and incident recovery behavior. A PoC need not complete a full production security certification, but it should expose assumptions that would create material implementation risk.
What Evidence Should A Blockchain PoC Provide For Privacy Or Erasure?
Show exactly what data is written on chain, what remains off chain, how integrity is verified, where copies and logs may exist, and how qualifying correction or deletion requests would be handled. If sensitive data appears in transaction payloads, receipts, smart contract storage, or node logs, document that explicitly rather than assuming application level deletion resolves the issue.
How Do You Know When A Blockchain PoC Is Good Enough To Proceed?
Proceed when the core workflow meets its acceptance criteria, material failure modes have understandable outcomes and recovery paths, integration behavior is proven, privacy and governance constraints are addressed, and remaining uncertainties are limited enough to test in a pilot. Do not proceed solely because a token was created or a transaction appeared in a block explorer.
Sources And References
-
Federal Reserve Bank of Boston — Building an Ethereum Blockchain Proof of Concept. https://www.bostonfed.org/publications/fintech/beyond-theory-getting-practical-with-blockchain/building-an-ethereum-blockchain-proof-of-concept.aspx
-
Agencia Española de Protección de Datos — Proof of concept Blockchain and the right to erasure. https://www.aepd.es/guias/Tech-note-blockchain.pdf
-
Agencia Española de Protección de Datos — Annex Technical description Proof of Concept Blockchain. https://www.aepd.es/guias/Annex-blockchain.pdf
-
PMC — Moving Beyond Proof of Concept and Pilots to Mainstream: Discovery and Lessons from a Reference Framework and Implementation. https://pmc.ncbi.nlm.nih.gov/articles/PMC10770802/
-
CEUR WS — A socio-technical vision of a blockchain proof of concept. https://ceur-ws.org/Vol-4134/paper24.pdf
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.