Issuing regulated digital securities, a practical guide
By Jeremy Ryan, Founder & CEO · October 2026
Issuing regulated digital securities is not primarily a token-development exercise. It is a securities issuance, ownership-record, distribution, and servicing program that uses blockchain technology in a controlled role. The most durable structures begin with the legal instrument, investor rights, offering pathway, and authoritative ownership record. The token comes after those decisions.
For decision-makers, the central question is straightforward: when a wallet balance changes, what legally changes, who confirms it, and which records control if systems disagree? A credible issuance architecture answers that question before the first investor is onboarded.
• Key Takeaways
• Start
With The Legal Instrument And Ownership Record
• Select
The Offering Structure Before Designing Distribution
• Build
The Issuance Stack Around Controls, Not Token Creation
• Operate The Security
After Closing
• Frequently Asked
Questions
Key Takeaways
• A digital security is a security first. Blockchain delivery does not replace registration requirements, exemption analysis, disclosure, investor eligibility, or market-participant rules.
• The master securityholder file is a control point. A token ledger can support legally meaningful transfers only when the issuance design specifies how it integrates with the authoritative ownership record.
• Distribution strategy determines technology requirements. Investor type, geography, resale limits, and intended trading venue should shape onboarding, wallet permissioning, and transfer logic.
• On-chain transferability is not unrestricted liquidity. A token may move technically while a transfer remains prohibited by securities-law restrictions, investor qualification rules, contractual limits, or venue rules.
• Post-issuance servicing must be designed before the offering opens. Dividends, interest, voting, redemptions, reporting, reconciliations, and incident response are part of the product, not afterthoughts.
Start With The Legal Instrument And Ownership Record
Define The Security Before Defining The Token
A regulated digital security is a blockchain-based representation of a security or security interest. It may represent common equity, preferred equity, debt, fund interests, revenue participation rights, or an interest in an underlying asset structure. The relevant legal and economic rights arise from governing documents, not from a token symbol or smart-contract label.
I would begin by identifying exactly what the investor receives:
• Equity ownership, voting rights, dividend rights, and liquidation preference
• Debt principal, interest rate, maturity date, collateral terms, and redemption mechanics
• Fund or special-purpose vehicle interests, including transfer and admission requirements
• Contractual economic rights that may require securities-law analysis because of how they are offered and managed
This discipline matters because a token can be technically polished yet legally incomplete. Consider a token that represents preferred shares. If the certificate of incorporation, subscription agreement, cap table, and transfer rules do not state how the token relates to those shares, the issuer may have created a confusing parallel record rather than a reliable digital security.
A SIFMA paper on security tokens notes that these instruments must satisfy the applicable legal definition of a security and comply with relevant distribution regulations. That is the correct starting point: classify the offering and establish the rights before selecting a chain, wallet model, or token standard.
Make The Master Securityholder File Authoritative
The master securityholder file is the legally controlling record of who owns the security. In a conventional issuance, this may be maintained by the issuer, a transfer agent, or another authorized recordkeeper. In a tokenized model, the ledger can be integrated into that process, but it should not be treated casually as a replacement merely because it is immutable or publicly auditable.
The key design choice is whether an approved blockchain transfer itself updates the master securityholder file, whether an administrator updates the file after review, or whether the token is only a digital representation of a separately recorded ownership interest. Each model has different operational consequences.
| Record Model | How Ownership Changes | Useful When | Main Risk To Address |
|---|---|---|---|
| Ledger-integrated register | Qualified transfer updates the ownership record under defined rules | Transfers are permissioned and automated | Smart-contract and identity-control failures |
| Agent-updated register | Administrator validates transfers and updates the legal register | Complex restrictions or manual review are expected | Processing delays and reconciliation gaps |
| Token as reference record | Token reflects, but does not itself transfer, the legal security | Early-stage pilots or limited-use representations | Investor misunderstanding about legal finality |
The SEC has explained that an issuer may integrate distributed-ledger technology with systems used to record security ownership, allowing a qualifying crypto-asset transfer to correspond to a transfer on the master securityholder file. The practical implication is not “put the cap table on chain.” It is to document the precise legal and operational bridge between identity, wallet address, token balance, and the authoritative register.
Treat Reconciliation As A Core Control
Every digital-security program should define a reconciliation process. At minimum, it should compare the token ledger, master securityholder file, investor identity records, wallet-authorization list, and corporate-action records. The process should name an owner, cadence, exception threshold, and remediation authority.
A mismatch can arise in several ways. An investor may change custodians. A wallet may be compromised. A token may be sent to an unauthorized address because of an implementation flaw. An administrator may process a redemption in the legal register before the token is burned. None of these scenarios is solved by calling blockchain records immutable.
The relevant question is not whether a transaction can be reversed on a blockchain. It is whether the issuer has documented authority and tested procedures to restore legally correct ownership records when systems diverge.
For architecture decisions involving identity, permissions, audit trails, and integration boundaries, enterprise blockchain architecture in regulated industries provides a useful companion framework.
Select The Offering Structure Before Designing Distribution
Registration Or Exemption Is A Business Decision
In the United States, an offer or sale of securities generally must be registered unless an exemption applies. The issuance route affects capital-raising scope, eligible investors, disclosure obligations, resale conditions, state-law treatment, marketing approach, and operational controls.
A Practical Law guide to U.S. asset tokenization states that a U.S. security-token issuance generally must be registered or conducted under an applicable exemption, including Regulation D, Regulation S, Regulation A, or Section 4(a)(6). No exemption is automatically “best.” The appropriate choice follows the intended distribution model.
| Offering Path | Typical Distribution Objective | Investor Access | Design Implication |
|---|---|---|---|
| Registered offering | Broad public capital raising | Potentially retail and institutional | Extensive disclosure and reporting architecture |
| Regulation D | Private capital raise | Often accredited investors | Eligibility controls and restricted-resale logic |
| Regulation S | Offshore distribution | Non-U.S. transactions meeting safe-harbor conditions | Geographic controls and separation from U.S. offers |
| Regulation A | Qualified offering with broader access | Can support wider participation, subject to qualification | Offering circular, qualification process, and ongoing obligations |
| Regulation Crowdfunding | Smaller eligible public offering | Retail participation within applicable limits | Registered intermediary and platform-specific workflow |
A decision-maker should work backward from the investor and liquidity objective. If the goal is a private raise from a defined group of accredited investors, a permissioned issuance with tight transfer rules may be coherent. If the goal is broader investor access, the disclosure, qualification, and servicing burden can be materially different. A token does not compress those differences away.
Design For Resale At The Same Time As The Primary Sale
The primary offering and secondary market cannot be designed independently. Resale rules, holding periods, investor status, jurisdiction, and venue eligibility may determine whether a buyer can receive the token at all.
For example, an issuer relying on a private-offering framework may whitelist only approved wallets associated with eligible investors. A transfer request could require the buyer to complete identity verification, provide required representations, pass jurisdictional screening, and use an approved custody arrangement. The smart contract can reject transfers that fail those checks. That is not simply a technical feature; it is an enforcement mechanism for the distribution design.
I would avoid promising liquidity merely because the instrument is on-chain. A digital security may be technically transferable at any hour, but lawful resale can still depend on contractual restrictions, securities-law conditions, and admission to a regulated venue. An alternative trading system may be relevant for eligible secondary activity, while an ordinary crypto exchange may not support the required participant, compliance, or security-trading framework.
Map Jurisdictions And Intermediaries Separately
Cross-border offerings require more than a U.S. exemption analysis. Different jurisdictions can impose distinct prospectus, licensing, solicitation, custody, and trading requirements. An offshore sale is not automatically compliant simply because a purchaser uses a non-U.S. wallet or foreign entity.
The same separation applies to intermediaries. Map each role explicitly:
• Issuer: Creates the security, defines rights, makes required disclosures, and authorizes corporate actions.
• Broker-dealer or placement agent: May solicit investors, facilitate transactions, or participate in distribution where registration or an exemption is required.
• Transfer agent or recordkeeper: Maintains ownership records and processes transfers under the defined record model.
• Custodian: Safeguards assets or private keys under the selected custody arrangement.
• Tokenization agent or technology provider: Deploys and operates technical components but should not be assumed to perform regulated functions merely by operating software.
• Trading venue: Facilitates eligible secondary transactions under its applicable regulatory permissions and rules.
The operating model should assign responsibilities in contracts and procedures, not just in an architecture diagram. Enterprise blockchain strategy consulting for compliance examines how to connect regulatory obligations to practical governance decisions.
Build The Issuance Stack Around Controls, Not Token Creation
Create A Requirements Matrix Before Deployment
The best technical design begins with a requirements matrix that ties every legal obligation to a system control, responsible party, evidence artifact, and exception process. This prevents a common failure mode: legal teams define restrictions in prose while developers deploy a token contract that cannot enforce or evidence them.
| Requirement | Example System Control | Evidence To Retain | Recovery Question |
|---|---|---|---|
| Investor eligibility | Wallet whitelist linked to verified identity | Onboarding record and approval decision | Who can revoke authorization? |
| Transfer restriction | Smart-contract validation before transfer | Transfer logs and restriction rules | How are errors corrected? |
| Ownership record | Scheduled reconciliation to legal register | Signed reconciliation report | Which record controls a discrepancy? |
| Corporate action | Approved distribution or voting workflow | Board authorization and payment record | How are unresponsive wallets handled? |
| Security incident | Key, wallet, and contract incident procedure | Incident log and authority record | Can tokens be frozen or reissued lawfully? |
A smart contract may encode ownership rights, transfer restrictions, and distribution mechanisms. Still, code is only one layer. It needs governance around upgrades, privileged keys, access rights, audits, change approval, monitoring, and incident response. If a contract includes an administrative freeze function, the governing documents and investor disclosures should explain the circumstances and authority for using it.
Select The Chain Based On Operating Constraints
Public, private, and permissioned networks each create different trade-offs around visibility, validator model, transaction cost, interoperability, uptime assumptions, privacy, and control. There is no universally superior blockchain for regulated digital securities.
A public chain may offer broad ecosystem compatibility and transparent transaction history, while requiring careful treatment of investor privacy, wallet control, and policy enforcement. A permissioned network can make participant governance more direct, but may reduce interoperability and introduce dependence on a narrower set of operators. Hybrid designs can keep sensitive investor information off-chain while recording permissions or settlement events on-chain.
The right selection depends on what must be public, what must remain confidential, who may operate infrastructure, and how transfers are expected to occur. For a structured evaluation of those trade-offs, see blockchain platform selection for financial institutions.
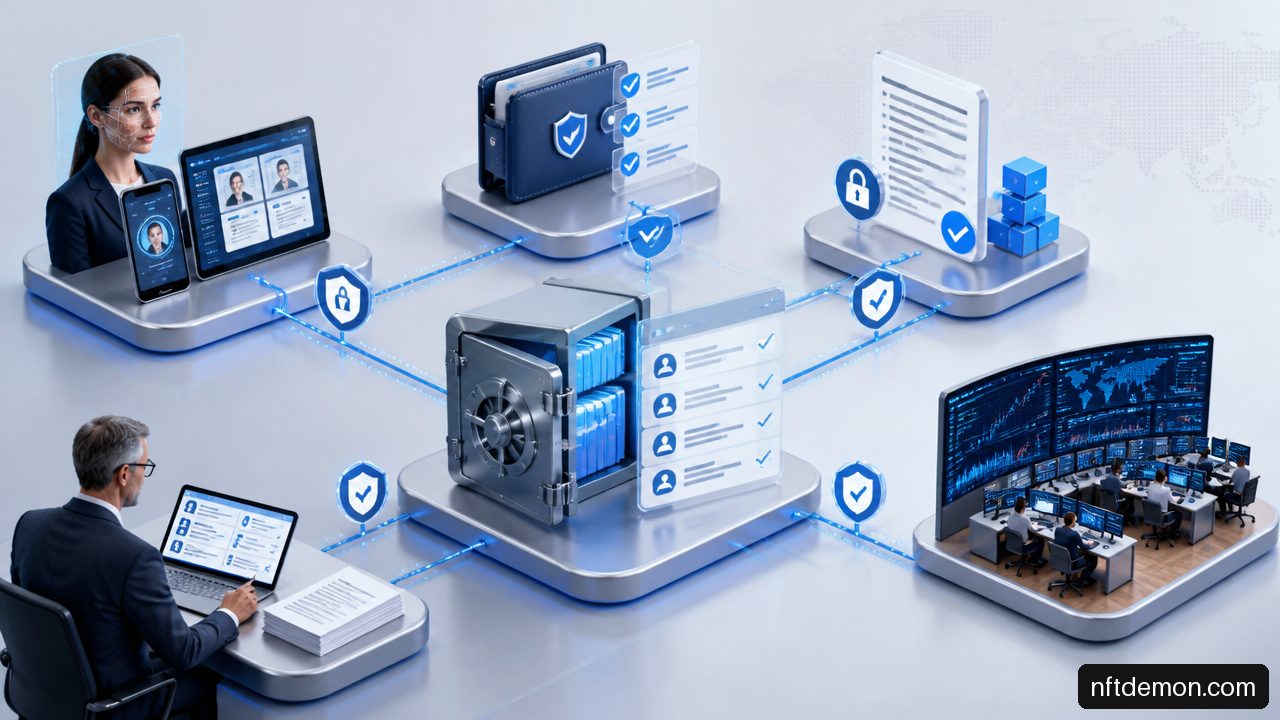
Test Failure Modes Before Investors Arrive
A production launch should include scenario testing, not merely successful token minting. The test plan should cover unauthorized transfer attempts, identity changes, lost wallet access, custody migrations, paused transfers, failed distributions, contract upgrades, investor death or incapacity, sanctions screening changes, and disagreement between the token ledger and legal register.
Fair warning: published industry data does not establish a reliable average rate of reconciliation failures, smart-contract defects, or issuance costs for regulated digital securities. That uncertainty is a reason to test the issuer’s own process with controlled cases.
Consider a simple scenario. An approved investor loses access to a self-custodied wallet containing tokenized notes. If the governing terms permit replacement, the issuer may need to verify identity, freeze the original address, update the master securityholder file, burn or invalidate the old token position, and issue a replacement to a newly approved address. Each action must be sequenced so the legal record and token supply do not temporarily show double ownership.
Operate The Security After Closing
Treat Corporate Actions As Product Features
After issuance, the security must still function. Equity may require voting, dividend declarations, stock splits, conversions, and communications. Debt may require interest payments, maturity notices, redemption calculations, covenant reporting, and default procedures. Fund interests may require capital-account updates, transfer approvals, and investor reporting.
Tokenization can automate parts of these processes, but automation should follow the legal event rather than invent it. A board declaration, payment instruction, or trustee determination may be the controlling action. The system then identifies entitled holders based on an approved record date, calculates allocations, executes payments or notices, and retains evidence.
Maintain Disclosure And Governance Discipline
The disclosure package should match the offering structure and continue to reflect material changes where applicable. Depending on the issuer and offering path, relevant materials may include offering documents, subscription agreements, risk disclosures, transfer restrictions, investor communications, financial information, and platform disclosures.
Decision-makers should also establish a governance calendar. At a minimum, it should address recurring reconciliations, compliance reviews, permission-list updates, key-access reviews, corporate-action preparation, investor reporting, and vendor oversight. A quarterly process can be reasonable for some programs, while high-volume transfer activity may call for more frequent checks. The correct cadence depends on the security and operating model.
Measure Whether Tokenization Earns Its Complexity
Tokenization is not justified solely because fractional units, programmable transfers, or continuous ledger visibility are possible. Those capabilities must solve a defined operational or commercial problem.
Ask four questions:
- Does the instrument need controlled fractional ownership or smaller investment denominations?
- Will programmable restrictions reduce manual processing without creating unacceptable administrative control?
- Is there a realistic distribution or secondary-market path for the intended investors?
- Do the expected benefits outweigh the cost of legal structuring, technical controls, servicing, reconciliation, and vendor governance?
If the answer to the third question is no, a tokenized issuance may still be useful for recordkeeping or private distribution, but it should not be framed as a liquidity strategy. If the answer to the second is no, conventional digital administration may be simpler. The disciplined choice is the one that matches the operating need.
Frequently Asked Questions
What Is A Regulated Digital Security?
A regulated digital security is a digital representation of a security or security interest that is issued, recorded, transferred, or serviced using blockchain or distributed-ledger technology while remaining subject to applicable securities laws and contractual terms.
How Do I Determine Whether My Token Is A Security?
Start with the economic rights, transaction structure, investor expectations, and applicable legal tests. Do not rely on a token’s name, technical design, or marketing label. Securities counsel should assess the proposed instrument before public promotion, token minting, or investor onboarding.
Do I Need To Register A Digital-Security Offering With The SEC?
Generally, an offer or sale of securities must be registered unless a valid exemption is available. The appropriate route depends on the issuer, investors, offering size, solicitation approach, geography, resale plan, and disclosure capacity.
Can Retail Investors Buy Digital Securities?
Potentially, but access depends on the offering pathway and applicable requirements. Certain structures can support broader participation, while private offerings often restrict sales to defined investor categories. Retail access also increases the need for clear disclosures, investor-protection controls, and suitable distribution processes.
Can Investors Resell Regulated Digital Securities Immediately?
Not necessarily. Resale may be limited by the original exemption, holding conditions, transfer restrictions, investor qualification, jurisdiction, and venue requirements. Technical transferability does not itself create a lawful secondary market.
Who Should Maintain The Legally Authoritative Ownership Record?
The issuer, transfer agent, or another authorized recordkeeper should be identified in the governing framework. The design must state whether a qualified blockchain transaction updates the master securityholder file automatically, through an agent review, or only after another legally required process.
What Happens If The Smart-Contract Ledger Conflicts With The Issuer’s Records?
The governing documents and procedures should identify the authoritative record and establish a remediation process. That process may involve pausing transfers, investigating the discrepancy, correcting the legal register, replacing or invalidating tokens where authorized, notifying affected investors, and documenting the resolution.
Sources/References
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.