How to tokenize real world assets with ERC 3643 compliance
By Jeremy Ryan, Founder & CEO · October 2026
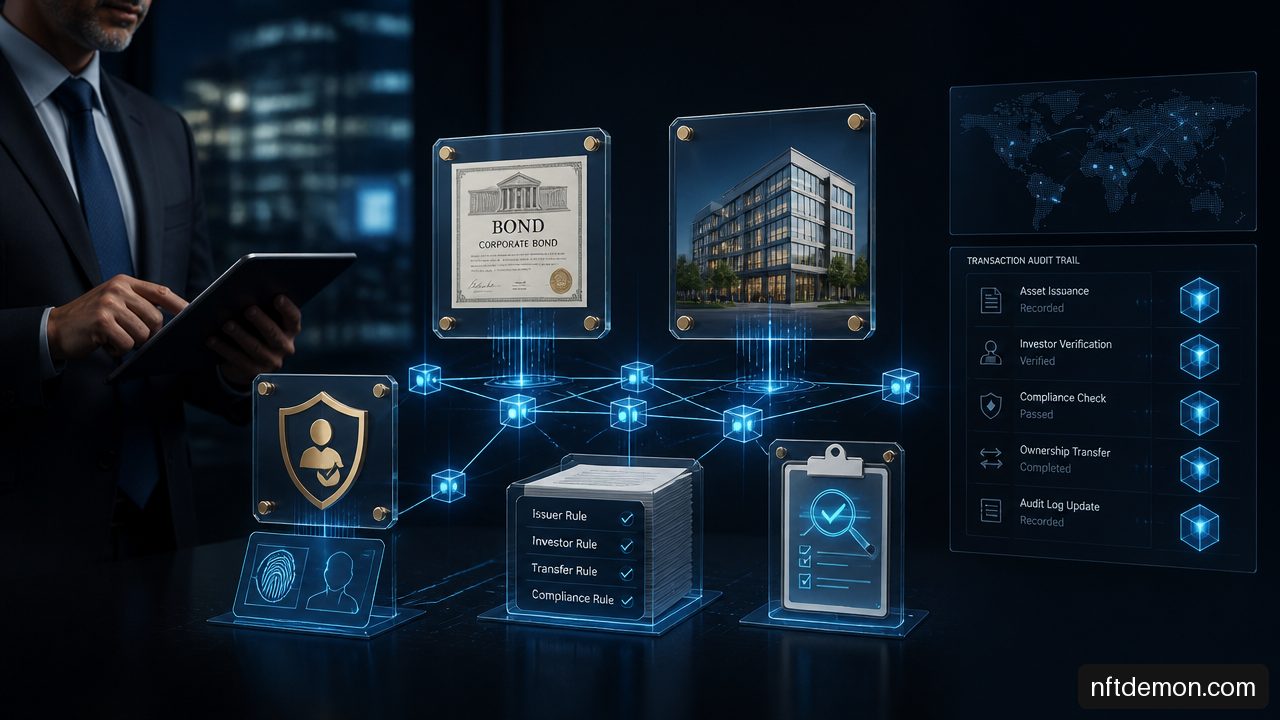
Tokenization is not simply the act of placing an asset reference on a blockchain. For institutions, how to tokenize real world assets under institutional compliance frameworks ERC-3643 begins with a harder question: what legal rights, investor restrictions, operating procedures, and recovery controls must remain enforceable after the token is issued?
ERC 3643 provides a permissioned-token architecture for regulated securities and other real world assets. It can prevent transfers that fail configured identity and eligibility requirements. It cannot, by itself, create legal ownership, replace securities counsel, settle tax obligations, or administer distributions. The institutional value comes from connecting the protocol to a disciplined legal and operational control model.
- What ERC 3643 Controls And What It Does Not
- Translate Legal Terms Into A Compliance Control Matrix
- Operate The Token Across Its Full Institutional Lifecycle
- Key Takeaways
- Frequently Asked Questions
- Sources
What ERC 3643 Controls And What It Does Not
ERC 3643 is designed for tokenized assets where ownership and transfer must be restricted to eligible participants. Rather than treating every wallet as an interchangeable holder, it combines a token contract with identity and compliance components. The result is a permissioned token that can operate on a public blockchain while enforcing rules at the token layer.
The core distinction matters. A public blockchain can remain broadly accessible even when the asset itself is not. As the ERC3643 built in compliance framework explains, permissioning can be applied through the token and related smart contracts instead of requiring the entire network to be permissioned.
For a decision maker, that architecture creates a useful separation: blockchain infrastructure may be shared, while investor access is controlled asset by asset.
The Required Contract And Trust Components
An institutional implementation generally has several connected elements. Each component has a technical role, but it also needs an accountable business owner.
| Component | Primary Function | Institutional Owner To Define |
|---|---|---|
| Token contract | Issues, transfers, freezes, and burns asset backed tokens | Issuer and authorized administrators |
| Identity Registry | Links wallet addresses to validated identity records | Transfer agent, platform operator, or compliance function |
| Trusted Issuer framework | Defines who may attest investor claims | Compliance leadership and legal governance |
| Compliance contract | Coordinates whether a proposed token action meets configured rules | Issuer, legal, and compliance stakeholders |
| Compliance modules | Apply offering specific conditions such as caps or restrictions | Product, legal, and engineering teams |
| Custody and servicing systems | Maintain records, payments, reporting, and operational evidence | Custodian, fund administrator, or operations team |
ERC 3643 documentation describes tokenized transfers that incorporate identity and eligibility checks through a permissioned token architecture. The important institutional implication is that a wallet address should never be treated as sufficient proof of investor status. It is only a destination controlled by cryptographic keys.
A validated identity can still be ineligible for a specific offering. An investor may pass KYC, yet be prohibited because of residency, accreditation status, investment limits, sanctions risk, a lockup period, or the distribution rules for that asset class. Identity verification answers who is this participant? Asset specific eligibility answers may this participant hold or receive this particular token now?
Transfer Validation Is A Decision, Not A Checkbox
A compliant transfer should be evaluated as a set of explicit conditions. In practical terms, the system asks whether the sender and recipient are permitted, whether the amount is permitted, and whether the transaction is permitted at that time.
ERC 3643 transfer validation can inspect recipient certificates and offering wide restrictions before authorizing a transaction, as described in the protocol overview of transfer validation. This is the foundation for controls such as investor qualification, country restrictions, and holder limits.
A typical pre transfer decision may consider:
• Whether both addresses are linked to approved identities.
• Whether required claims are present, current, and issued by an authorized party.
• Whether the recipient is eligible for this offering and jurisdiction.
• Whether the transfer would breach a holder cap, concentration threshold, or token limit.
• Whether either address or a portion of the balance is frozen.
• Whether a lockup, redemption window, or court ordered restriction applies.
The read only canTransfer check is valuable because it
allows a platform to test the decision before submitting a state
changing transaction. It is not a substitute for full operational
review. A precheck can return an allowed result, then become outdated if
an administrator changes a claim, freeze, or compliance rule before
settlement. Systems should therefore handle failed execution gracefully
and preserve evidence of both the attempted transfer and the final
result.
What The Standard Cannot Establish
This boundary deserves plain language: an ERC 3643 token does not automatically establish that the token holder owns the underlying property or security under applicable law.
Legal enforceability depends on the offering documents, issuer entity, governing law, custody arrangement, investor agreements, recordkeeping, and the relationship between the token ledger and the legally recognized register. This is especially consequential for private fund interests, debt instruments, fractional real estate interests, and asset backed receivables.
Consider a token representing a limited partnership interest. The smart contract may prevent an unqualified recipient from receiving tokens. Yet the partnership agreement must still state how token ownership maps to partnership records, how transfers become legally effective, who can recognize a replacement wallet, and what happens in insolvency or dispute resolution. The blockchain control is evidence and enforcement infrastructure. It is not a legal instrument on its own.
This is why architecture should be planned alongside legal design. A broader discussion of enterprise blockchain architecture in regulated industries can help frame where smart contracts fit among custody, identity, audit, and reporting systems.
Translate Legal Terms Into A Compliance Control Matrix
The strongest ERC 3643 programs start before smart contract development. They create a control matrix that converts legal language into testable rules, responsible parties, required evidence, and exception procedures.
Without that translation step, teams often deploy technically valid contracts that enforce an incomplete version of the offering. The gap may not appear until a transfer is blocked incorrectly, a distribution reaches a restricted holder, or an investor requests recovery after losing access to a wallet.
Build The Matrix From The Offering Documents
Start with the subscription agreement, private placement memorandum or prospectus, investor representations, transfer restrictions, custody terms, and servicing obligations. Break each requirement into a control statement.
| Legal Or Operating Requirement | On Chain Predicate | Off Chain Control | Evidence To Retain |
|---|---|---|---|
| Only approved investors may acquire tokens | Recipient has valid required claims | KYC, AML, sanctions, and investor review | Verification record, claim status, decision log |
| Distribution limited by country | Recipient jurisdiction is permitted | Jurisdiction classification and legal review | Residency evidence and rule version |
| Maximum number of holders | Transfer does not exceed holder cap | Cap monitoring and exception handling | Holder reports and transaction logs |
| One year lockup | Transfer date is after lockup end | Investor communication and legal exceptions | Subscription date and exemption approval |
| Redemption at NAV | Tokens are surrendered and burned after approval | NAV calculation, payment, and reconciliation | Valuation record, redemption notice, payment proof |
The Compliance contract can enforce investor caps, token caps, and other offering rules through attached modules, according to the ERC3643 compliance documentation. That modularity is useful, but it creates governance work. Teams must decide who can add, remove, or reconfigure a module, and whether a rule change affects existing holders.
A compliance module should be selected when the condition is objective, consistently enforceable, and needs to block prohibited transfers automatically. Avoid forcing subjective or document heavy judgments entirely on chain. A dispute about beneficial ownership, fraud, inheritance, or court authority often requires a reviewed off chain process before an administrator applies an on chain action.
Establish Trusted Issuer Governance
Claims are only as reliable as the parties authorized to issue them. A trusted issuer may attest that an investor has completed verification, qualifies for a category, or meets another defined requirement. The issuer must therefore be governed like a critical control provider, not treated as a generic API integration.
A practical trusted issuer policy should define:
Which organizations can issue each claim type.
What underlying checks each claim requires.
How long each claim remains valid before renewal.
How revocation is handled after sanctions alerts, expired documentation, or changed investor circumstances.
Who reviews issuer performance and approves changes to the trust list.
Which events require immediate notification to the issuer, administrator, and affected investor.
Fair warning: a broad “KYC approved” claim is usually insufficient for institutional use. It may demonstrate that an identity was reviewed, but not whether the investor can hold this private credit instrument, fund interest, or jurisdiction restricted security. Use claims that are scoped to clear questions.
For example, an issuer may maintain separate claims for identity verified, jurisdiction eligible, professional investor status, and offering eligibility. A transfer rule can require all four where appropriate. If the professional investor claim expires, the system can block secondary transfers to that investor until renewal, while the legal and operational policy determines whether existing holdings must be frozen or merely prevented from expanding.
Design Administration As A Controlled Function
The ability to freeze, pause, recover, mint, or burn tokens is not merely an administrative convenience. It is a concentration of authority that can materially affect holders.
Administrative functions require segregation of duties. A sound model typically separates the person requesting an action, the compliance reviewer approving it, the authorized signer submitting it, and the party reconciling the outcome. Multi signature authorization, time delayed execution for nonemergency changes, immutable audit logs, and investor notice procedures may be appropriate depending on the asset and jurisdiction.
The ERC3643 compliance management model notes that compliance interactions extend to token creation, transfers, destruction, and pre transfer validation. That means governance must cover the full lifecycle, not just secondary market transfers.
For organizations building these controls into a broader deployment plan, enterprise blockchain strategy consulting for compliance is relevant because legal controls, technical configuration, and operating ownership must be aligned before issuance.
Operate The Token Across Its Full Institutional Lifecycle
Issuance receives most of the attention. Institutional reliability is determined by what happens afterward: subscription settlement, custody changes, distributions, redemptions, corporate actions, incidents, and audits.
Issue And Transfer With Reconciliation Built In
At issuance, the administrator should verify that the investor is approved, the wallet is linked to the correct identity, the subscription has settled, and the token amount matches the legal record. Minting should not be triggered solely because a payment message exists.
A useful sequence is:
Complete investor onboarding and asset specific eligibility review.
Register the approved wallet or custody address to the investor identity.
Confirm subscription acceptance and payment settlement.
Mint tokens through the authorized workflow.
Reconcile token supply, legal register, cash records, and investor statement.
Preserve the approval trail, transaction identifier, and rule version in force at issuance.
Secondary transfers should follow the same discipline. A buyer can be eligible and still be unable to settle if the transfer breaches a market level cap. Conversely, an apparent blockchain transfer may fail after a claim expires or an address is frozen. Operations teams need exception queues and clear investor communications, not just smart contract events.
Treat Asset Servicing As A Separate Workstream
A token’s transfer logic does not automatically calculate dividends, interest, NAV, tax withholding, voting entitlements, or repayment amounts. These are asset servicing obligations. They must be specified as deliberately as identity and transfer rules.
For a tokenized bond, servicing may require interest accrual, record date logic, withholding treatment, payment instructions, maturity redemption, and treatment of default. For a private fund interest, it may involve periodic NAV reporting, capital calls, distributions, voting, transfer windows, and investor communications.
The smart contract may help define a snapshot of balances at a record date, but institutions should decide which system is authoritative for valuation, payments, tax records, and legal notices. In many structures, the blockchain record and the administrator’s books must be reconciled rather than assuming one makes the other unnecessary.
A tokenized asset is operationally complete only when its cash flows, legal records, and holder rights can be administered as reliably as its transfers can be restricted.
Plan Recovery And Incident Response Before Launch
Lost keys and compromised wallets are predictable events, not edge cases to postpone. ERC 3643 implementations can support freezing and recovery related controls, but the proper use of those controls depends on the issuer’s documented authority and process.
A recovery procedure should state:
• What evidence is required to establish loss, compromise, or authority to act.
• Who approves a freeze and whether partial freezes are supported.
• How a replacement wallet is verified and linked to the existing identity.
• Whether tokens are moved, burned and reissued, or handled through another approved process.
• How the legal register, custody records, and investor statement are reconciled.
• When the investor, regulator, insurer, or other parties must be notified.
Consider an institutional custodian changing wallet infrastructure. The holder may remain the same legal entity, but the destination wallet changes. A recovery process should distinguish this controlled migration from a retail investor claiming a lost key, and from a court ordered transfer. Each scenario requires different evidence and approval thresholds.
This is where a blockchain operating model for ownership compliance becomes essential. Technology can freeze a balance in seconds. A defensible institution must also show why the freeze occurred, who approved it, what rights the holder retained, and how the case was closed.
Test Negative Scenarios, Not Just Happy Paths
Before production, test the transfer rules against failures that are likely to occur in real operations. A successful transfer from one approved wallet to another proves very little.
Use a formal test set that includes:
• An expired identity claim.
• A revoked eligibility claim.
• A recipient in a prohibited jurisdiction.
• A transaction that would exceed a holder or token cap.
• A partial freeze that permits only an unfrozen balance to move.
• A transfer attempted during a lockup period.
• A recovery request for a compromised wallet.
• A rule change proposed while transfers are pending.
• A redemption that requires burning tokens only after external payment approval.
The objective is not merely to confirm that the contract rejects bad transactions. It is to confirm that operations, custody, compliance, investor support, and the legal register reach the same answer. Where they do not, the program has identified a process defect before capital is at risk.
Key Takeaways
• ERC 3643 is appropriate when a tokenized asset requires identity aware, eligibility based, and offering specific transfer controls.
• The token should represent rights defined in enforceable legal documentation, not an unsupported claim that blockchain ownership alone is legally sufficient.
• Separate identity verification from asset specific eligibility. A verified investor may still be unable to hold a given token.
• Create a compliance control matrix before configuring smart contracts. Every legal restriction should map to an on chain rule, an off chain procedure, or both.
• Govern trusted issuers, administrative roles, claim expiration, revocation, and contract changes with the same rigor applied to other regulated control functions.
• Design servicing, reconciliation, recovery, and incident response before issuance. Transfer restrictions are only one part of institutional tokenization.
Frequently Asked Questions
What Is ERC 3643 And Why Is It Suitable For Institutional RWA Tokenization?
ERC 3643 is a permissioned token standard for securities and tokenized assets that require controlled issuance and transfer. It is suitable when the issuer needs to validate investor identity, eligibility, and transaction conditions before token movement. It is not automatically necessary for unrestricted assets where open transferability is the intended feature.
How Does ERC 3643 Differ From A Standard ERC 20 Token?
A standard ERC 20 token generally allows transfers between any valid addresses with sufficient balance. ERC 3643 adds identity and compliance architecture so a transfer can be blocked when the recipient or transaction fails configured requirements. The difference is not cosmetic: it changes who may hold the asset and how the issuer manages exceptions.
What Legal Rights Does An ERC 3643 Token Represent?
The token represents only the rights established by the issuer’s legal documents and governing framework. It may represent equity, debt, a fund interest, a revenue right, or another contractual claim. The smart contract should align with those documents, but it does not independently determine legal enforceability.
Can ERC 3643 Enforce KYC, AML, Accreditation, And Jurisdiction Rules?
It can enforce the presence and validity of relevant identity claims and offering rules during token operations. The underlying KYC, AML, sanctions, accreditation, and jurisdiction assessments generally occur off chain through approved compliance processes. The token enforces the resulting eligibility decision; it does not replace the investigation behind it.
How Are Lost Keys Or Compromised Wallets Handled?
The issuer can use documented freezing and recovery procedures where the implementation and legal authority permit them. A robust process verifies the claimant, freezes the affected balance if warranted, validates a replacement address, obtains required approvals, and reconciles the token action with the legal register and custody records.
Can ERC 3643 Handle Dividends, Interest, Redemptions, And Voting?
It can support token balance records and lifecycle actions that are relevant to these processes, but it does not by itself perform complete asset servicing. Institutions still need defined processes for valuations, payment approvals, tax treatment, notices, record dates, voting administration, and reconciliation.
Is ERC 3643 Enough To Make A Token Legally Compliant In Every Jurisdiction?
No. ERC 3643 is a technical compliance framework, not universal legal clearance. Legal classification, offering exemptions, disclosure requirements, custody rules, transfer restrictions, privacy duties, and reporting obligations vary by asset and jurisdiction. The standard should be implemented as one part of a broader regulated operating model.
Sources
ERC3643 — ERC-3643 Permissioned Tokens: https://docs.erc3643.org/erc-3643
ERC3643 Documentation — Compliance: https://erc-3643.github.io/documentation/docs/suite/compliance/
ERC3643 Documentation — What is ERC3643?: https://erc-3643.github.io/documentation/docs/abstract/
ERC3643 — Built-in Compliance Framework: https://docs.erc3643.org/erc-3643/overview-of-the-protocol/built-in-compliance-framework
ERC3643 — Compliance Management: https://docs.erc3643.org/erc-3643/smart-contracts-library/compliance-management
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.