Audit trail creation for autonomous AI financial decision making systems
By Jeremy Ryan, Founder & CEO · September 2026
Audit trail creation for autonomous AI financial decision-making systems should begin before an agent is allowed to approve a payment, post a journal entry, alter a credit limit, or route an exception. The core question is not simply whether the model produced a plausible answer. It is whether the organization can later prove what happened, why it happened, who or what authorized it, and what financial action followed.
For decision makers, the objective is practical: create evidence that supports control testing, incident response, financial reconciliation, model governance, and regulatory review without making the operating workflow unusable.
Define The Financial Decision Record
An audit trail is not a transcript of model activity. It is a structured evidentiary record that connects a financial decision to the authority, policy, data, model state, human intervention, and downstream transaction involved. A chat transcript might help diagnose a failure, but it is not enough to establish control accountability.
Start With A Governance Envelope
Before an autonomous agent executes, it should submit a governance envelope: a bounded request describing the proposed action and the authority under which it is acting. This is the control boundary between a useful automation and an unaccountable actor.
The Monetary Authority of Singapore’s Safeguards for Agentic Finance at Runtime defines a structure in which the submitted governance envelope, mandate checked, disposition outcome, applied rules, outcome basis, and elapsed time are captured as an immutable audit-log record.
In practice, the envelope should answer five questions before execution:
• Who is acting? Record the agent identity, service account, workflow instance, and delegated authority.
• What is being requested? State the proposed payment, posting, hold release, portfolio action, or account change in business terms and machine-readable fields.
• What mandate allows it? Identify the policy, approval limit, customer instruction, contractual rule, or operating procedure being invoked.
• What constraints apply? Include risk thresholds, sanctions screening status, segregation-of-duties rules, transaction limits, and required approvals.
• What will happen if approved? Specify the downstream system, expected transaction type, and any irreversible effects.
Consider an accounts-payable agent that proposes a $48,000 supplier payment. A useful envelope does not merely say “invoice matched.” It identifies the legal entity, supplier, invoice record, purchase order, matching tolerance, payment date, agent authority, policy version, bank-account verification result, and required approval tier. If an investigation occurs six months later, that package gives reviewers a real starting point.
Use A Minimum Decision Schema
I recommend a fixed schema rather than free-form event logging. Fixed fields improve reconciliation, make control gaps visible, and prevent teams from discovering too late that one workflow never recorded the person who approved an override.
| Record Group | Required Fields | Why It Matters |
|---|---|---|
| Identity and authority | Decision ID, correlation ID, agent ID, invoking workflow, service identity, delegated mandate | Establishes who acted and under whose authority |
| Time and scope | Submitted timestamp, decision timestamp, stage timestamps, jurisdiction, legal entity, business process | Supports sequencing, latency analysis, and accountability |
| Input state | Source-system IDs, input hashes, data snapshot reference, document versions, context reference | Shows exactly what the system evaluated |
| Model and configuration | Model provider or model ID, model release, prompt or instruction version, parameters, retrieval set, rules version | Enables point-in-time reconstruction |
| Control evaluation | Rules applied, threshold values, validation results, screening outcomes, disposition | Proves the policy path taken |
| Outcome and rationale | Recommended action, confidence or score, decision basis, limitation flags, exception reason | Makes the decision reviewable without exposing unnecessary internal traces |
| Oversight | Reviewer ID, approval or rejection, override reason, escalation owner, follow-up status | Preserves management challenge and accountability |
| Financial execution | Transaction ID, journal ID, payment ID, settlement reference, execution status, reversal reference | Closes the chain from decision to financial effect |
| Integrity | Entry hash, prior-entry hash, signature ID, retention class, storage location | Makes alteration detectable and evidence retrievable |
The fields should be captured at decision time. Reconstructing them later from changing databases, model registries, and workflow tables is risky. A supplier master record may be corrected after the payment; a prompt template may be edited; a rule may be retired. The audit record must preserve the state that existed when the action was authorized.
Separate Evidence From Reasoning Traces
This distinction is easy to miss. Auditability is not identical to explainability.
An explanation answers: “Why did the system suggest this action?” An audit trail answers: “What evidence proves this action was authorized, controlled, and executed?” Provenance answers: “Where did the underlying information come from and how did it move?” All three are useful, but they should not be treated as the same artifact.
A model’s internal reasoning trace may contain sensitive data, speculative intermediate statements, or protected prompt content. It can be useful for model-risk testing, but it should not automatically become the permanent financial evidence record. Instead, preserve a decision basis that is specific enough for review: cited source records, matched controls, score, confidence band, applicable policy, and triggered threshold.
EY’s AI governance guidance for financial reporting calls for logging inputs, prompts, context, model and version, parameters, outputs, timestamps, reviewer identity, and evidence that outputs used in controls can be reproduced where feasible at the point in time they were used.
Make Evidence Tamper-Evident And Reproducible
A log stored in a production database is not automatically trustworthy. Administrators may have broad access, retention jobs may delete records, and incident responders may not know which copy is authoritative. Financial evidence needs integrity controls designed into the architecture.
Choose The Right Integrity Pattern
“Immutable” is often used too loosely. No system should assume records are metaphysically impossible to alter. The operational goal is tamper evidence: unauthorized modification or deletion becomes detectable, attributable, and recoverable.
| Pattern | Best Fit | Strength | Limitation |
|---|---|---|---|
| Append-only storage | High-volume workflow events | Simple write-once operating model | Requires access and retention controls |
| Hash chaining | Ordered agent actions | Reveals altered, removed, or reordered records | Chain breaks require investigation and recovery process |
| Digital signatures | High-value approvals and external evidence exchange | Binds a signer or system identity to a record | Key management becomes a critical control |
| Periodic external anchoring | High-assurance evidence sets | Creates an independent integrity checkpoint | Does not replace searchable operational logs |
For most organizations, a layered design is better than selecting one mechanism. Use append-only event storage for operational scale, hash-chain entries within a decision session, sign high-risk decisions or daily log manifests, and store integrity verification results separately from the application that generated them.
Praesidia’s financial-services guidance on AI agent governance describes structured logs containing agent identity, invoking authority, timestamp, resource, and outcome, while noting that cryptographic signing or chained entries can make deletion detectable.
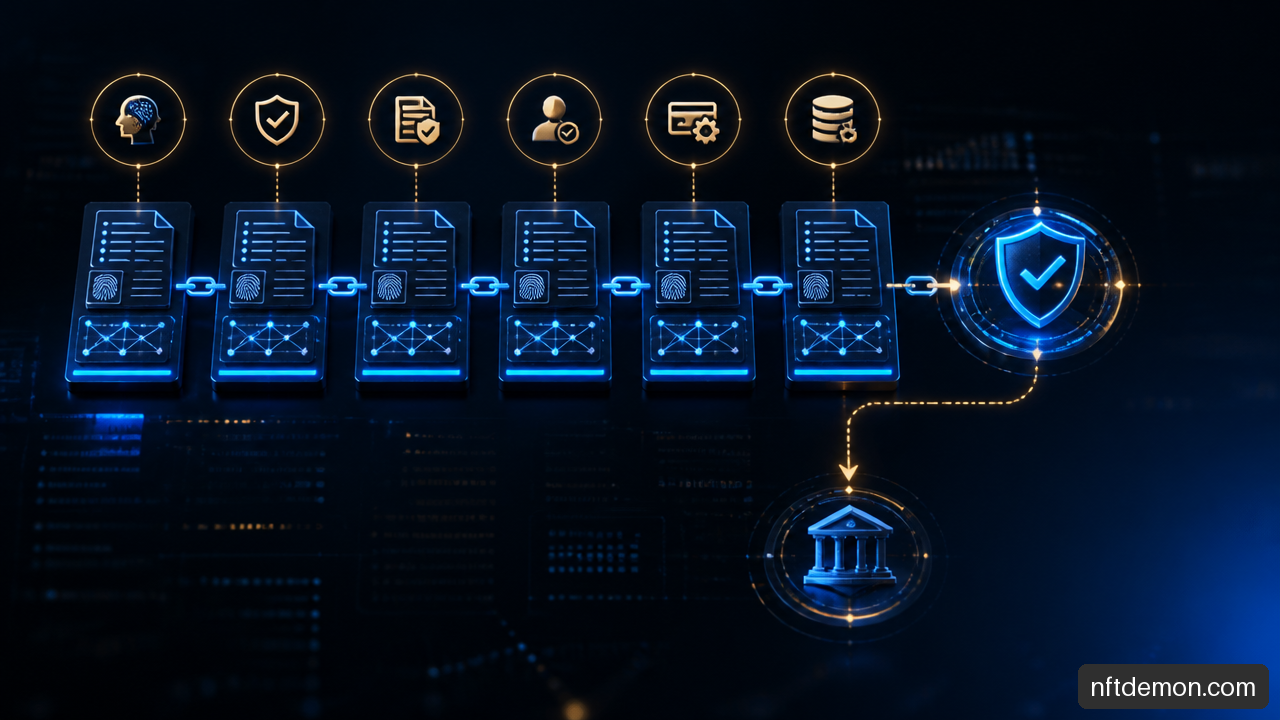
A blockchain is not required for this design. It can be appropriate when multiple parties need a shared integrity anchor, but it may add complexity, privacy constraints, and operational dependencies. The decision criterion is straightforward: use an externalized ledger only when the assurance benefit exceeds the cost of operating and governing it. For teams evaluating that boundary, designing governance for blockchain networks offers a useful framework for assigning decision rights and accountability.
Capture Time As A Control Signal
Stage latency belongs in the audit trail. It is not merely a performance metric.
If a payment agent normally completes mandate validation in 200 milliseconds but suddenly takes 18 seconds, the delay may indicate a retrieval failure, timeout fallback, manual intervention, degraded screening service, or repeated policy evaluation. Each possibility changes the control posture. Logging elapsed time for submission, validation, disposition, approval, and execution helps reviewers distinguish a valid decision from one produced under abnormal runtime conditions.
Latency is particularly valuable in incident reconstruction. Suppose a fraud-prevention model allows a transfer after its external data source times out. The final “approved” status alone hides the relevant fact: the system reached that decision under a fallback mode. The record should identify the fallback, its permitted policy basis, and whether a compensating review was triggered.
Link The Decision To The Financial Effect
A decision trail that ends at model output is incomplete. The critical chain is:
- A source event or instruction enters the workflow.
- The agent evaluates data, rules, and authority.
- A disposition is issued: approve, reject, hold, escalate, or request review.
- A financial system creates a payment, journal, settlement, account update, or other transaction.
- The transaction reaches a final state, fails, reverses, or is amended.
The same correlation ID should travel across those stages. Where a downstream platform assigns a new identifier, record the mapping rather than relying on a loose timestamp match.
TFSF Ventures’ work on autonomous-agent audit trails emphasizes decision provenance, configuration versioning, and linkage from an agent decision to the downstream financial transaction. That linkage is what allows finance teams to reconcile an instruction all the way to settlement or reversal.
Operate, Test, And Retain The Audit Trail
The strongest schema fails if it is not embedded in operating controls. Audit trails are systems of evidence, not merely data stores. They need owners, tests, access rules, exception handling, and recovery procedures.
Treat Overrides As First-Class Events
Human oversight is meaningful only when the system records what changed and why. Do not overwrite the original AI recommendation. Store the original decision, the override, the actor, timestamp, authority, evidence reviewed, and final downstream effect.
A practical override taxonomy can include:
• Data correction: a source record was inaccurate, incomplete, stale, or duplicated.
• Policy exception: an authorized person allowed an action outside a standard rule.
• Model challenge: a reviewer disputed the recommendation, score, classification, or rationale.
• Operational contingency: a service outage, time-critical event, or fallback procedure changed the normal path.
• Control breach: the agent attempted an unauthorized action or bypassed a required gate.
Each category should route to a different follow-up workflow. A data correction may trigger source-system remediation. A policy exception may require periodic management review. A control breach should trigger security and model-governance investigation. Lumping them into a generic “manual override” field destroys that distinction.
The supporting operating model must define who can override, what evidence they must provide, and who reviews patterns over time. The same discipline applies to operational controls for blockchain deployment: privileged access, change approval, monitoring, and incident response cannot be afterthoughts.
Test Whether Reconstruction Actually Works
A quarterly report showing that logs exist is not a sufficient test. I recommend conducting controlled reconstruction exercises for representative high-risk decisions.
- Select a completed decision, an overridden decision, a rejected decision, and an exception.
- Retrieve the exact input references, model and rule versions, authority, disposition, and transaction mapping.
- Verify the hash chain or signature status.
- Reproduce the decision context where feasible without using altered current-state data.
- Confirm that a reviewer can explain the financial outcome and locate follow-up actions within the defined service level.
This process exposes hidden breaks. A common one is that the model registry holds a version number but not the retrieval corpus or ruleset that shaped the outcome. Another is that transaction IDs are available only in a separate treasury platform whose retention schedule differs from the AI workflow. The remedy is not a larger log. It is an explicit evidence contract between systems.
Set Retention By Obligation, Not Convenience
There is no universal retention period tailored solely to autonomous AI financial decisions. Retention depends on jurisdiction, regulated activity, instrument type, litigation holds, financial-reporting obligations, and contractual requirements. In many financial contexts, organizations use multi-year schedules, often in the five-to-seven-year range, but that range should not be treated as a substitute for legal and compliance review.
For example, a low-value internal expense-coding recommendation may follow ordinary accounting-record retention. An autonomous trading, lending, payment, or sanctions-related decision may need a more stringent schedule because the decision evidence intersects with additional regulatory duties. Retain the linked chain consistently: the AI decision, approvals, model configuration, source references, and final transaction record must not expire on incompatible schedules.
Retention also requires an operating model for access and discovery. Creating an enterprise blockchain operating model is relevant here because durable evidence depends on ownership, escalation paths, and lifecycle decisions as much as on storage technology.
Key Takeaways
• Design the record before granting autonomy. Every material AI action should carry identity, authority, point-in-time inputs, configuration, control results, outcome, oversight, and transaction linkage.
• Log the governance envelope and disposition path. This makes it possible to show not just what the agent did, but what mandate and rules permitted or blocked it.
• Use tamper-evident controls, not vague immutability claims. Append-only storage, hash chaining, signatures, and independent checkpoints address different risks.
• Preserve the original recommendation and every override. A modified final answer without its original state is weak evidence and poor model-governance data.
• Reconcile to settlement, posting, or reversal. The audit trail is complete only when the decision can be connected to its financial effect.
• Test reconstruction under pressure. If internal audit cannot rebuild a decision within a defined period, the evidence design is incomplete.
Frequently Asked Questions
What Should An Audit Trail Include For An Autonomous AI Financial Decision?
At minimum, capture the decision ID, agent identity, invoking authority, timestamps, source inputs or immutable references, model and configuration version, rules applied, outcome, confidence or threshold data, human review, override events, integrity metadata, and downstream transaction identifiers. For material actions, include the governance envelope and the policy basis for the disposition.
How Do You Make An AI Financial Audit Log Tamper-Evident?
Use controlled append-only storage, hash-chain related events, digitally sign high-value records or periodic manifests, restrict privileged access, and monitor verification failures. Tamper evidence is stronger when the integrity verification process is separated from the workflow service that produced the original log.
What Is The Difference Between An Audit Trail, Provenance, And An Explanation?
An audit trail proves the controlled history of a decision and action. Provenance describes where information originated and how it moved or changed. An explanation describes why a model produced a recommendation. A compliance-grade financial system should connect all three while retaining each according to its own sensitivity and evidentiary purpose.
How Should Human Overrides Be Logged?
Store the original AI recommendation unchanged, then create a separate override event containing reviewer identity, delegated authority, timestamp, new decision, reason category, evidence considered, and follow-up requirement. Never replace the AI outcome with the human outcome in the same field; that removes the history auditors need.
How Do You Prove Which Model Version Made A Financial Decision?
Record the precise model identifier or release, prompt or instruction version, parameter set, retrieval context, rules version, and deployment environment at decision time. A model name alone is insufficient when an implementation can change prompt templates, tool permissions, thresholds, or reference data without changing the model label.
How Long Should Financial AI Audit Records Be Retained?
Set retention based on the financial process, jurisdiction, instrument, regulatory duties, audit requirements, contractual commitments, and legal holds. There is no single AI-specific universal period. The key control is preserving all linked evidence for a compatible period so a decision is not retained after its supporting transaction history or configuration evidence has disappeared.
Sources And References
-
Monetary Authority of Singapore — Safeguards for Agentic Finance at Runtime: https://www.mas.gov.sg/-/media/mas-media-library/development/fintech/ai-safr/safr.pdf
-
EY — AI governance and risk for financial reporting: https://www.ey.com/en_us/insights/assurance/ai-audit-readiness-for-financial-reporting
-
Praesidia — AI Agent Governance for Financial Services: https://www.praesidia.ai/blog/ai-agent-governance-financial-services
-
TFSF Ventures — Audit Trails for Autonomous Agent Systems: https://www.tfsfventures.com/blog/audit-trails-autonomous-agent-systems
NFT Demon Holdings helps enterprises scope, evaluate, and build blockchain programs — start with a free evaluation call.
Talk through your use case
Free evaluation call — objective, constraints, and fit, before any proposal.